Published Saturday, October 24, 2026 at 04:58 PM PT

BLUF: An IPS signature (ET GAMES MINECRAFT “Server response inbound,” ID 2021701) fired on 192.168.1.1 and the traffic was allowed. This is a game-traffic match, not a confirmed attack or compromise. Nothing in the available data shows malware or exploitation.
DETAILS
- Signature: ET GAMES MINECRAFT Server response inbound (ID 2021701). Alert type: IPS.
- Action: allowed. The IPS did not block the traffic.
- Source: 148.113.223.138. Direction: inbound. Monitored target: 192.168.1.1.
- No payload, flow records, or internal host attribution were supplied, so the internal device involved is unidentified. Related memory context returned no matches.
IMPACT
- Scope unconfirmed. Any internal host that exchanged traffic with 148.113.223.138 during the alert window could be involved.
- 192.168.1.1 is a private (RFC 1918) address, often a gateway. The alert does not say whether it is the sensor, the gateway, or an endpoint.
- Inference, not verified: “server response inbound” usually means an internal client opened a session to an external Minecraft server.
- Depending on network policy, this may be a policy issue rather than a security incident.
RECOMMENDED ACTIONS
- Pull firewall or flow logs for the alert window and identify the internal host that communicated with 148.113.223.138.
- Confirm whether gaming or Minecraft traffic is permitted on this network.
- If it is not permitted, block the destination per policy and check the identified host for unauthorized software.
- If it is permitted, document the exception. Consider tuning the signature to reduce noise.
- Escalate to incident response only if follow-up shows unexpected data transfer, other indicators of compromise, or further alerts from the same source.
SOURCES
- IPS alert record as supplied (ET GAMES MINECRAFT, ID 2021701; 192.168.1.1; 148.113.223.138). No external corroboration was available. Signature detail is taken from the rule name only.
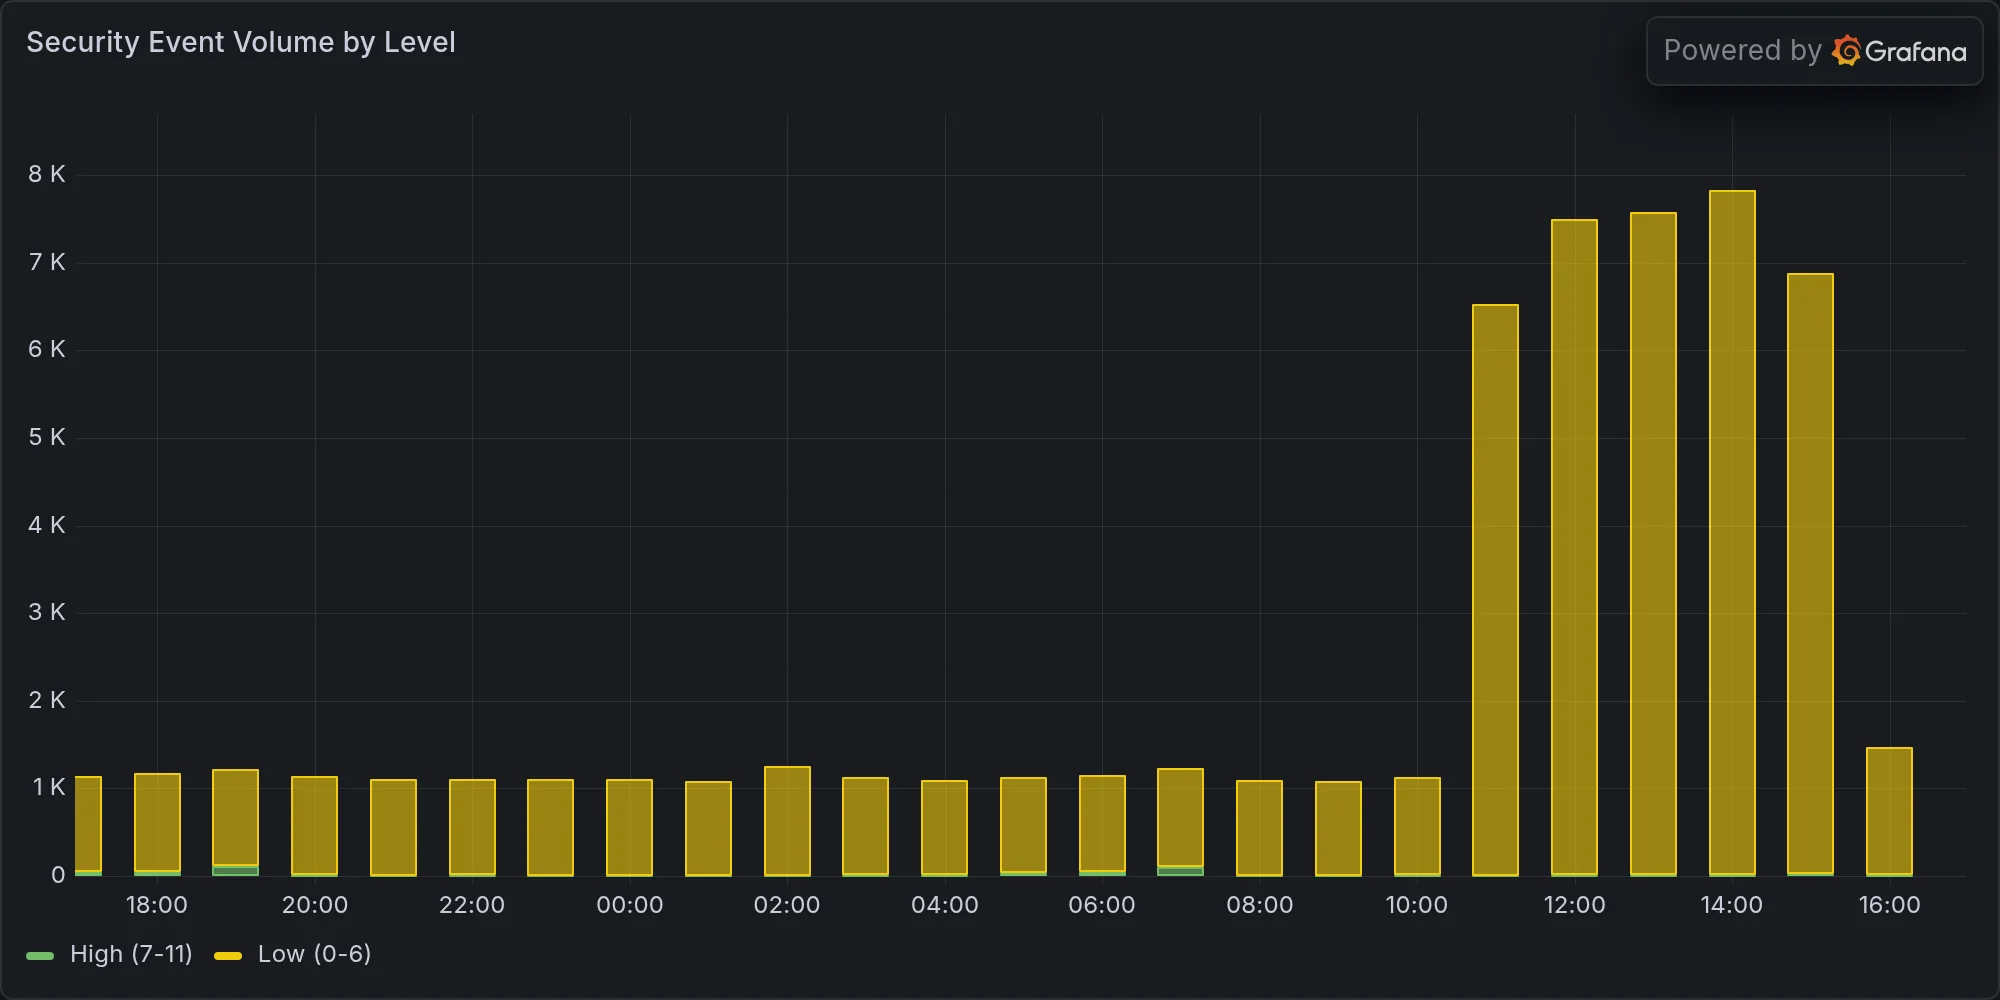
Recent high-severity events at publish time: