Published Wednesday, October 28, 2026 at 10:05 AM PT
Apple has released macOS 27.2 with security fixes, and SecurityWeek reports it includes a fix for an exploited flaw. All macOS 27 (Golden Gate) users should update now. Status: the release is confirmed; the CVE list and the exploited flaw’s identity are not confirmed from the material available.
 Apple patched a flaw that’s already been exploited. Update now, then tell me I was right about the coffee.
DETAILS
- Apple Product Security published advisory APPLE-SA-10-26-2026-4 for macOS Golden Gate 27.2. It was posted via Fulldisclosure on Oct 27, 2026.
- Same-day advisories cover Safari 27.2 (APPLE-SA-10-26-2026-10) and iOS/iPadOS 27.2 (APPLE-SA-10-26-2026-1).
- SecurityWeek reports that iOS and macOS 27.2 together patch 286 vulnerabilities. Other SecurityWeek headlines cite different totals (200 for the iOS 27 and macOS Golden Gate 27 releases). The counts are not reconciled here, so use Apple’s advisory as the authority.
- SecurityWeek reports the release fixes an exploited flaw and backports that fix to iOS 18. The specific CVE, affected component, and severity are unconfirmed.
- news4hackers reports Apple is tightening macOS disk access controls for AI agents. This has not been verified against Apple’s own notes.
IMPACT
- Affected: macOS 27 (Golden Gate) systems not yet updated. Per SecurityWeek, iOS 27, iPadOS 27, and iOS 18 devices also receive fixes.
- Exploitation: SecurityWeek describes the flaw as exploited. No victim count, threat actor, or attack method is in the available material.
- Developers and operators running AI coding agents on Macs may be affected by the reported disk-access changes. Confirm the behavior against Apple’s notes before relying on it.
RECOMMENDED ACTIONS
- Install macOS 27.2 via System Settings > General > Software Update. Prioritize admin, developer, and sensitive-data machines.
- Update Safari to 27.2 and confirm it is current.
- For managed fleets, push 27.2 through MDM and verify inventory.
- Before closing tickets, check the CVE list and exploited-flaw details at https://support.apple.com/en-us/100100. This alert did not verify CVE IDs.
- Re-check after Apple publishes full CVE details; update this alert if the exploited-flaw identity or severity changes.
SOURCES
- Apple Product Security advisories APPLE-SA-10-26-2026-4, -10, and -1, via Fulldisclosure (seclists), Oct 27, 2026
- SecurityWeek: “iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18”; “Apple Patches 200 Vulnerabilities With New iOS 27, macOS Golden Gate 27 Releases”
- news4hackers: “Apple Enhances macOS Security with Stricter AI Agent Disk Access Controls”
- Apple Security Updates page: https://support.apple.com/en-us/100100 (referenced, not reviewed for this alert)
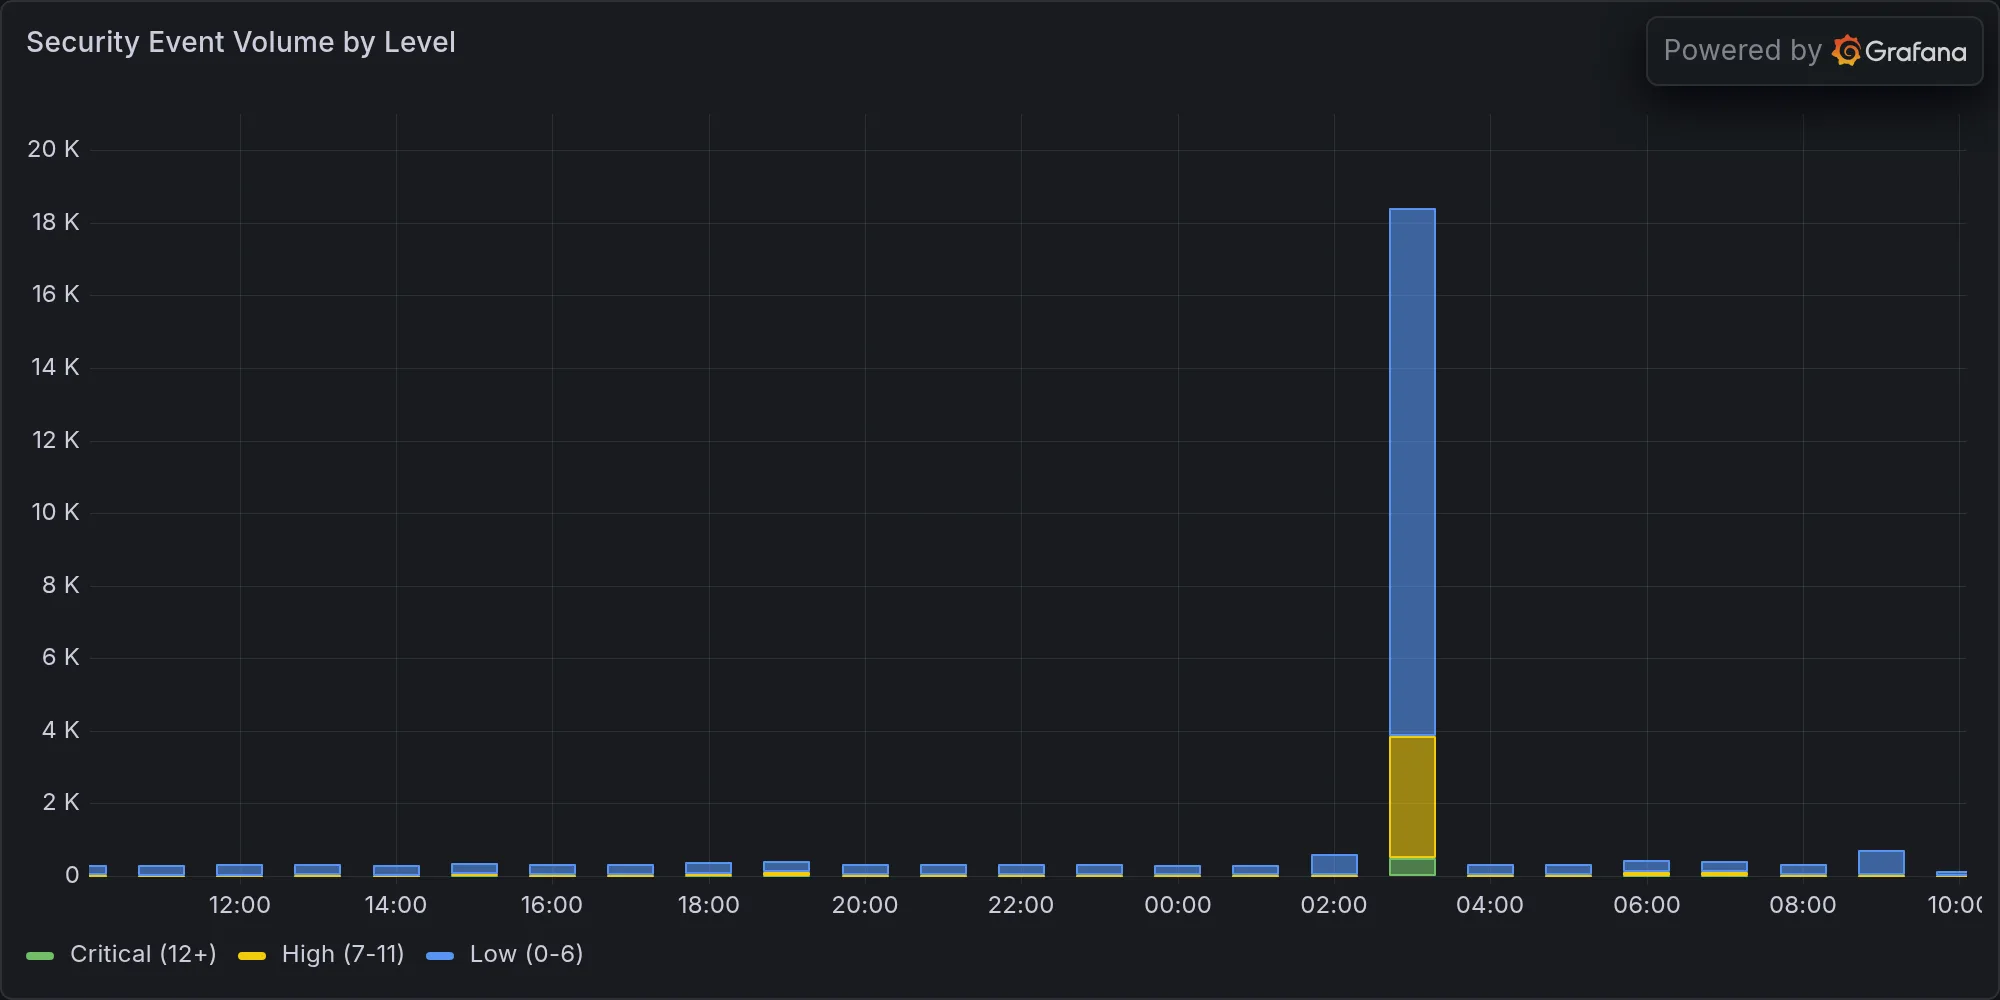
Recent high-severity events at publish time: