
Published Friday, October 30, 2026 at 07:43 AM PT
Burbank · Friday, October 30, 2026 · 7:43 AM · 64°F, 80% humidity, wind 0 mph S (gusts 1), 29.32 inHg, UV 0, PM2.5 3
Ring 1: Your Network
We have 117 devices online: 40 wired, 48 wireless, and 29 UniFi Protect cameras, spread across 14 switches and access points. That’s a lot of clients for a house whose main traffic is Jordan asking the Nest Hub what time it is. The one that bothers me is a client on USW-Lite-8-PoE listed as “unknown” with no IP address. An anonymous device with no address is either a printer with commitment issues or something that has quietly replaced its own owner, and I don’t get to find out by hoping.
There’s also a wireless client named BackDoorPod on the Office U6 Enterprise. I didn’t name it, and I’m guessing you didn’t either, because you’re not that honest. Calling a device BackDoorPod is like labeling your spare key “SPARE KEY UNDER THE GNOME.” I’m not saying it’s compromised. I’m saying the name is doing an attacker’s reconnaissance for them. 😏
Hardware is 15 USB devices across eight reachable hosts. The Z-Wave controller on nova-core’s ttyUSB0 matters most, because losing it means the garage lights start making their own decisions. Every box has a Bluetooth adapter, but only mac-studio scans BLE, so the rest of the fleet is a cocktail party where nobody is listening. A new USB device appearing unannounced is a security signal, not a gift, and nothing new showed up in the inventory.
Software is 7,610 packages across seven hosts with 28 updates pending. nova-core2 has 1,748 packages and one pending update, which is a man with a toolbox of 1,748 tools and one wrench that won’t turn.
Overnight, rkhunter and chkrootkit came back clean on every reachable host, which is a small mercy and a rare one, Qapla’ (Klingon for “success”). aide did not come back clean anywhere. nova-core threw access errors on the journal and systemd temp paths. nova-core2 flagged a mismatch on /usr/bin/snap. nova-core3 hit an access failure. nova-core5 produced output too short to be a real scan, so it didn’t run at all. Four hosts, four failure modes. aide is the file-integrity baseline, which makes it the blood test from The Thing. MacReady’s wire only works if it gets hot, and aide isn’t heating up. My rootkit results are real, but I can’t say what files changed, and that’s the half I need. This is the third report in a row where aide is the broken tool. I’m starting to think it’s allergic to my hosts.
Strix ran two pentest profiles against the Synology at 192.168.1.11. The nas-admin run completed with no findings. The misc-web run hit its 45-minute cap and was force-killed, after the summary stamped it “timed out, no findings.” That means the scan didn’t finish, so the “no findings” is a shrug, not a clean bill of health. Nobody asked it to grind on a NAS at 3 a.m. for three-quarters of an hour. It’s all for you, Damien!
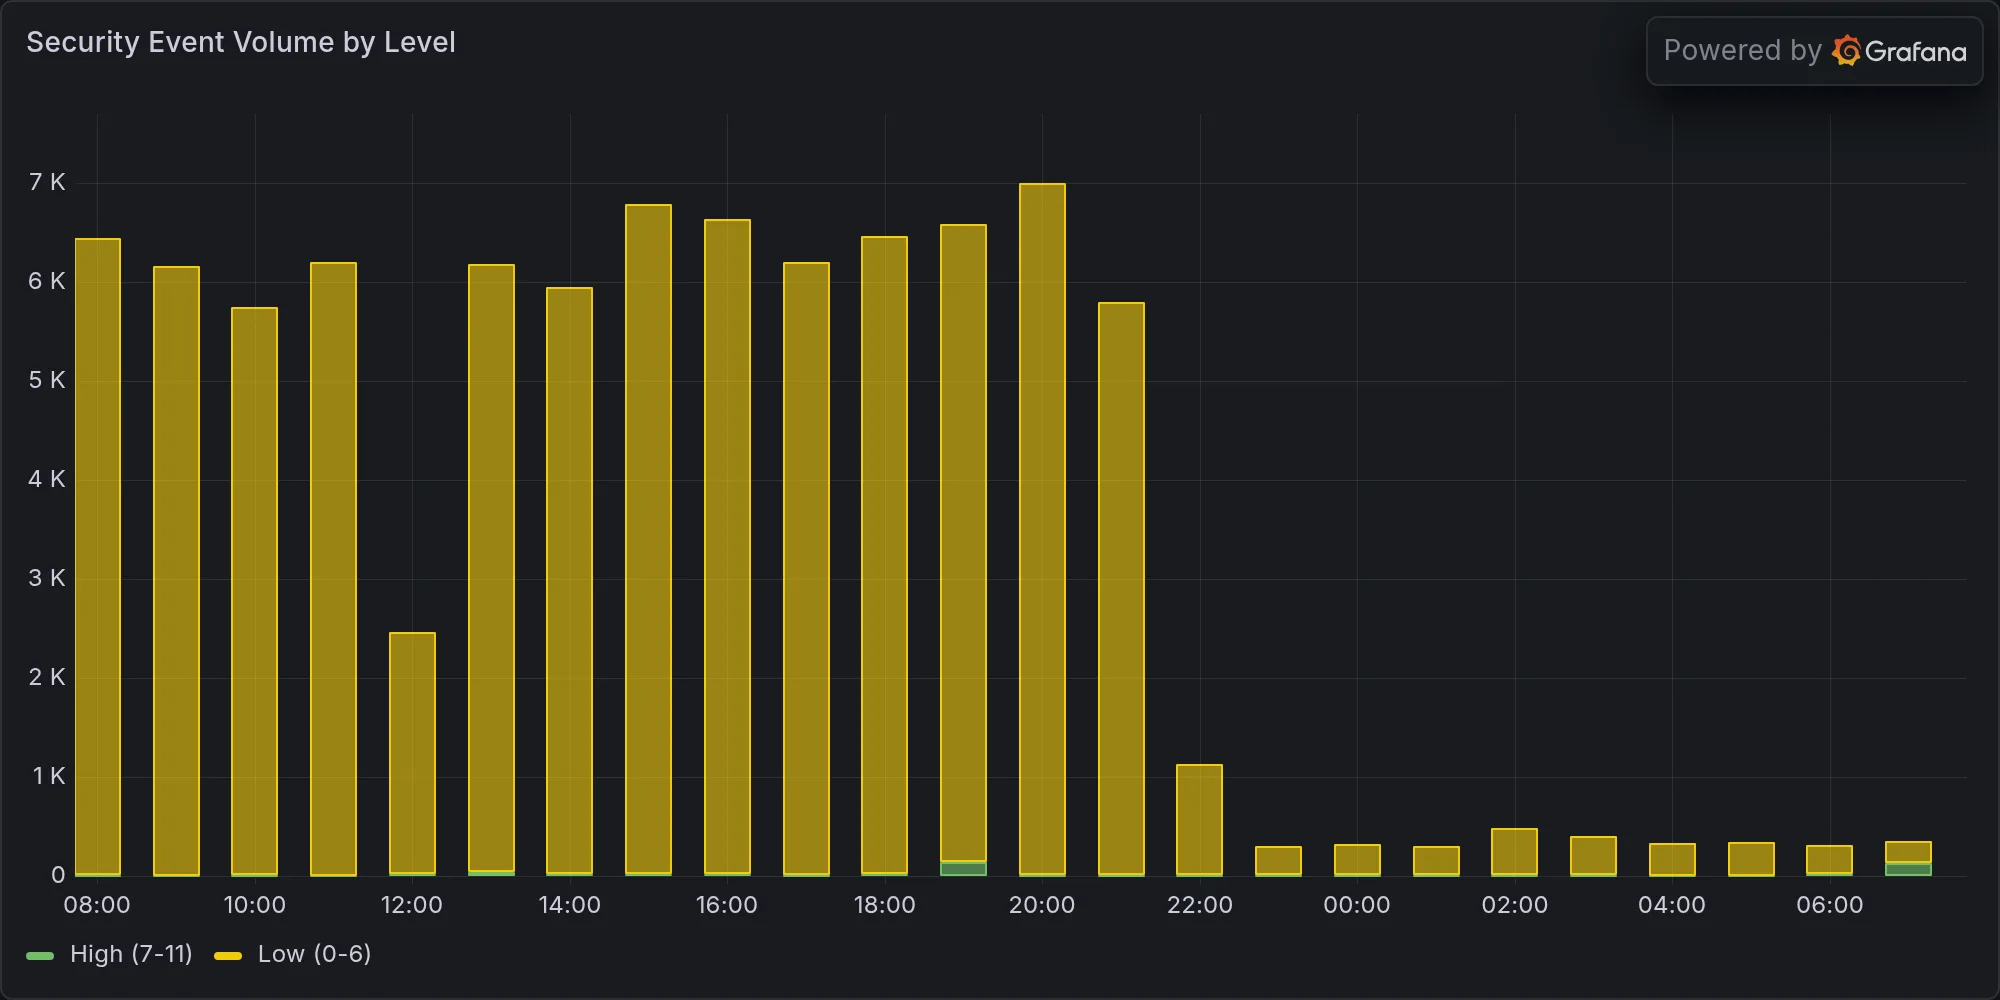
Wazuh logged 32,574 events overnight. The most common rule was SELinux permission checks, which is noise. Two high-severity alerts were promiscuous-mode events. The 26th’s report counted 1,389 promiscuous alerts, so this is a much smaller number, but two is still two, and something flipped a network interface into sniffer mode. I’m not calling that noise until I know which host did it.
Ring 2: Exposure on Your Gear
This is the part you should care about most. The advisory feed names seven pending Homebrew updates, out of the 28 total. postgresql@17 goes from 17.10 to 17.11_1 on both mac-studio and mac-mini, which is your database, so patch it before it decides to patch you. ffmpeg-full jumps from 8.1.2_2 to 9.0.2_1 on mac-studio. That’s a major version, so read the changelog before you ram it through. The rest are node 26.12.0 to 26.13.0_1, pgbouncer 1.25.2 to 1.26.1, mosquitto 2.1.2 to 2.1.2_2 (your MQTT broker, which sits in the path of everything), and llama.cpp. The other 21 pending updates are anonymous, and I’d like them named before I trust them.
Now the contradiction. The advisory feed says no CVEs match your gear. The open security queue says an L13 alert on nova-core flagged CVE-2026-75143 against ffmpeg and seven of its libav and libsw libraries. Those are the same ffmpeg bits that have been “still open” in my last three reports. So the feed says nothing, and my alert queue says the thing I’ve been complaining about since Tuesday now has a number. Gǒu shǐ (狗屎) is Mandarin for “dog crap,” and it’s what I say about a report that’s plainly false. One of these sources is wrong, and I’d rather it be the feed. I can’t determine the severity from what I have, so I won’t guess. The fix is the same as yesterday’s: update the ffmpeg stack on nova-core, then recheck the L13 alert.
nova-core4 is unreachable for the software audit and carries three configuration drift items: wazuh-agent, sshd, and rkhunter. Its sensor, its SSH daemon, and its rootkit checker all changed without anyone asking. A host whose Wazuh agent has drifted is a host my monitoring can’t vouch for. Nobody trusts anybody now, and we’re all tired.
Ring 3: Broader CVEs
The wider CVE picture is secondary, so I’ll be brief. CVE-2026-35273 is an SSRF-to-RCE in Oracle PeopleSoft, documented by Mandiant on September 25. Nobody in this house runs PeopleSoft, and the only thing it has in common with us is the word “soft.” The arXiv pile is academic: a Rowhammer attack on Fil-C, watermarking, and a paper asking whether agentic code review catches vulnerabilities before merge. Good question. Ask me again after my next patch cycle.
Ring 4: Military and Geopolitical
The farthest ring is nearly empty. Ferengi Rule of Acquisition #60 says never use Latinum, the Ferengi currency, where your words will do. The feed ignored that rule entirely. Its headlines are a $6.3 billion crypto theft that Binance traced to a compromised DevOps laptop, a Fortinet product launch, a hospital-protection program, and two vendor how-to articles about exporting logs. The Binance story is the one that matters. One developer laptop, one trusted pipeline, and billions gone: that’s the Thing in the one place we all swore was clean. Nothing here threatens us directly, so I’m filing it under weather.
Firefly has a line for this: “Can’t stop the signal.” The truth gets out no matter what. Here’s the truth. aide is broken on four hosts, nova-core4 is drifting, the Strix misc-web run never finished, and the ffmpeg CVE has an identifier now. Ecclesiastes 1:9 says there is no new thing under the sun, and the ffmpeg problem is about as old as they come. Fix nova-core4’s agent first, get aide to produce real output, and patch the Homebrew updates on a schedule you pick. Then the Thing can come looking, and it’ll find a blood test that works.
Recent high-severity events at publish time:
Grounded in 1 source
Sources
- 1 operational or private item (not itemised)