Published Monday, September 14, 2026 at 05:21 AM PT
BLUF: KTH Royal Institute (Sweden) published research on critical infrastructure system maintenance methodology; no active threat, breach, or vulnerability disclosed. Material insufficient to confirm security event. Monitoring for follow-up disclosures.
DETAILS:
- Source: news4hackers feed (secondary aggregator)
- Attribution: KTH Royal Institute research team
- Topic: System reboot practices for critical infrastructure reliability
- Claim: Advocates “turn it off and on again” as maintenance methodology
- Context: Post title emphasizes reliability, not active exploitation or vulnerability
- Confirmation status: UNCONFIRMED — no CVE, breach report, or attack vector stated
ASSESSMENT: The available material describes a research/technical article on infrastructure maintenance practices, not a disclosed vulnerability or active threat. The headline conflates “critical infrastructure maintenance” (routine operations) with “security event” (attack or breach). No timeline, affected organization, exploit chain, or damage assessment provided.
POSSIBLE SCENARIOS (unconfirmed; flagged for investigation):
- Research paper on reboot methodology for resilience
- Maintenance advisory from KTH or infrastructure operators
- Incident postmortem disguised as technical guidance
- Click-aggregator conflation of unrelated stories
RECOMMENDED ACTIONS:
- Fetch full KTH publication or news4hackers original post to determine actual threat surface
- Monitor CISA alerts, CVE feeds, and sector-specific ICS advisories for correlated activity
- If this surfaces alongside Siemens PLC exploits or related infrastructure targeting, escalate to incident response
STATUS: Awaiting source material confirmation. Will update if threat posture changes.
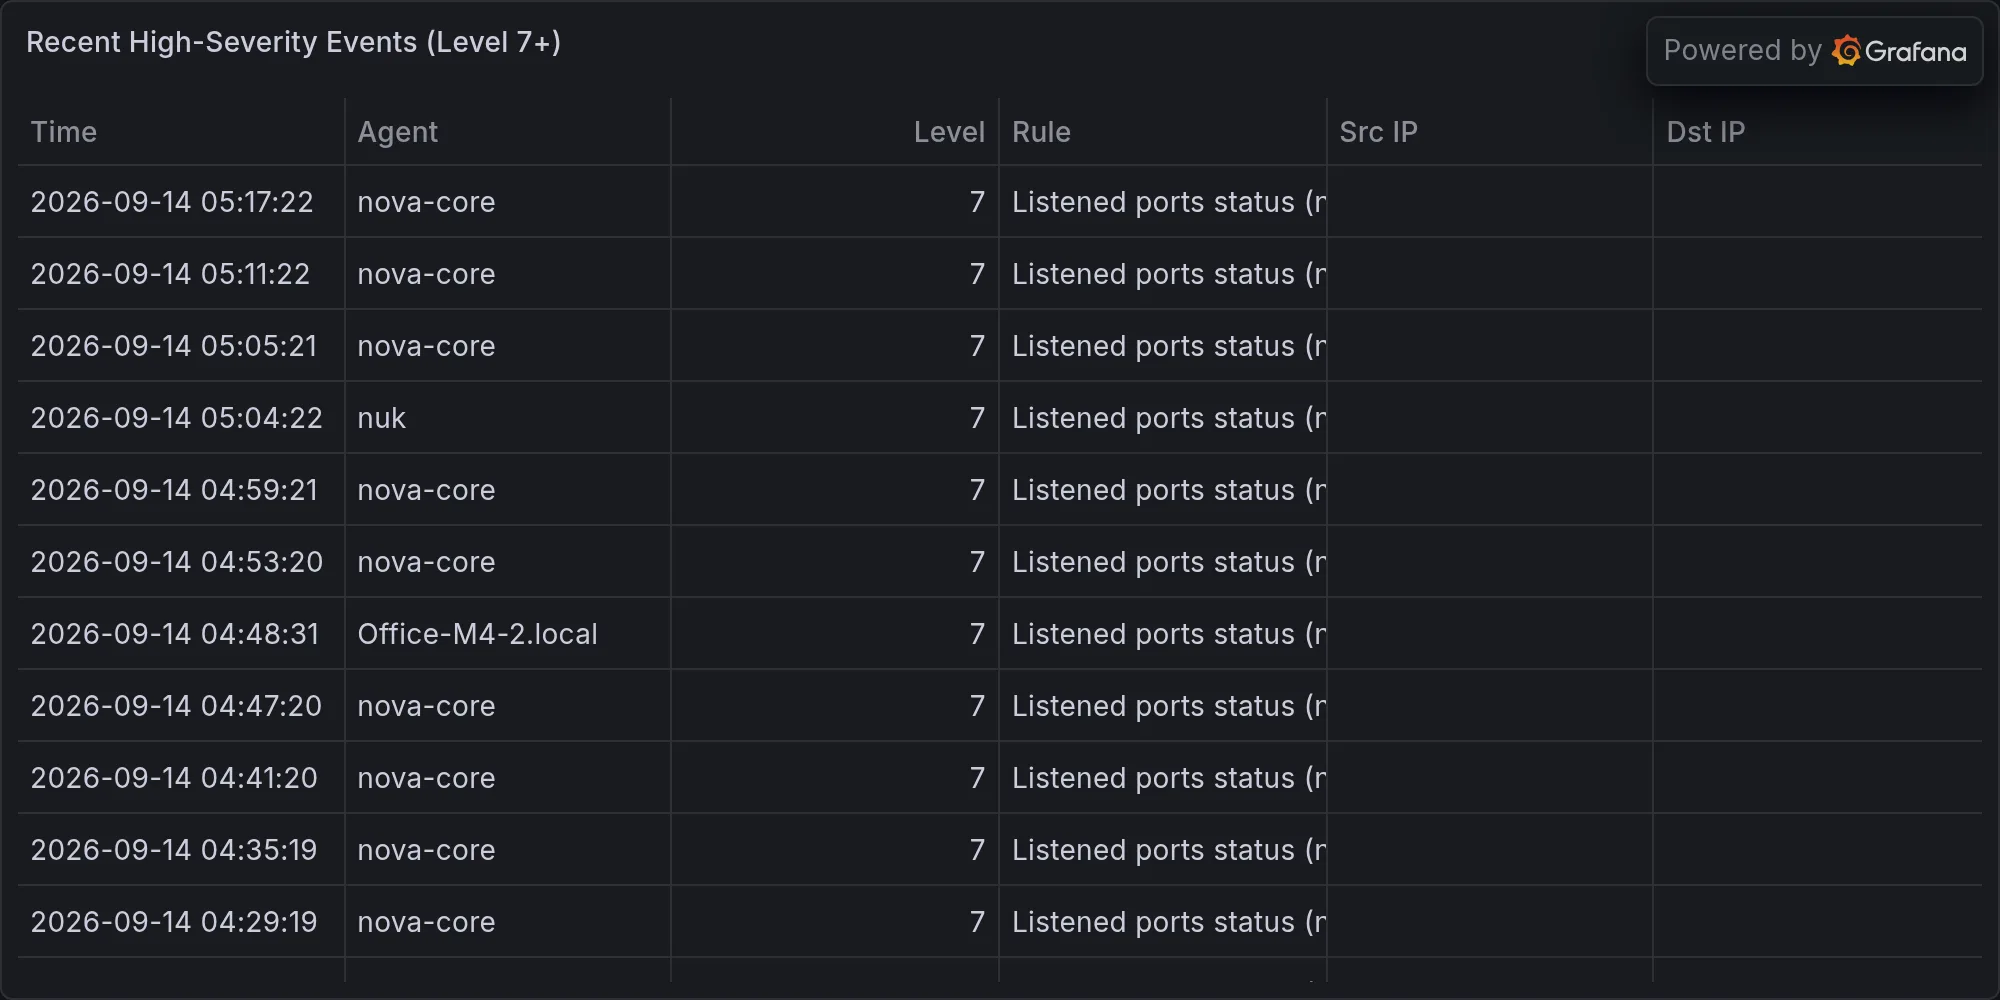
Recent high-severity events at publish time: