Published Monday, September 14, 2026 at 11:23 AM PT

BLUF: ENISA activated the Cyber Resilience Act (CRA) Single Reporting Platform on September 11, 2026, fulfilling EU vulnerability reporting requirements for actively exploited vulnerabilities. Organizations subject to CRA scope must now use this platform for reporting. Immediate action: verify your CRA classification and reporting obligations; confirm access to the platform if your organization is in scope.
DETAILS:
- Platform activation date: September 11, 2026. ENISA launched the CRA Single Reporting Platform in alignment with EU Cyber Resilience Act vulnerability reporting obligations entering force.
- Purpose: Centralized reporting mechanism for actively exploited vulnerabilities affecting CRA-regulated products and services.
- Regulatory trigger: The CRA vulnerability disclosure regime is now operationally live. This is not advisory—organizations in scope are subject to reporting obligations.
- Scope unclear from available material: The provided sources do not specify which product categories, organizational sizes, or geographies fall under CRA reporting mandates. Consult the platform itself or ENISA guidance for classification.
IMPACT:
- Direct: Any organization manufacturing or distributing products/services covered under EU CRA scope must comply with the single reporting platform for vulnerabilities they become aware of that are actively exploited.
- Indirect: Organizations whose vendors or supply-chain partners fall under CRA may face new disclosure/notification requirements if vulnerabilities affecting their products are reported through the platform.
- Compliance risk: Organizations not yet aware of CRA scope or reporting obligations face potential regulatory enforcement. The obligations are effective now.
RECOMMENDED ACTIONS:
- Immediately: Determine whether your organization or products fall under CRA scope. ENISA and national competent authorities (NCAs) have published scope guidance.
- Establish internal process: Designate a responsible party and audit trail for vulnerability reports your organization will submit to the CRA platform.
- Verify platform access: If in scope, register and authenticate with the platform at this time to avoid access delays when a vulnerability must be reported.
- Monitor for technical guidance: ENISA will likely publish API/submission standards and best practices. Subscribe to ENISA alerts or your NCA’s notifications.
SOURCES:
- news4hackers, September 2026 (ENISA CRA Platform activation)
- Help Net Security, September 2026 (CRA obligations)
- Industrial Cyber, September 2026 (CRA reporting framework)
Note: This alert reflects only confirmed platform activation. Detailed reporting procedures, timelines, and covered vulnerability classes require direct consultation with the ENISA platform and your jurisdiction’s CRA implementation guidance.
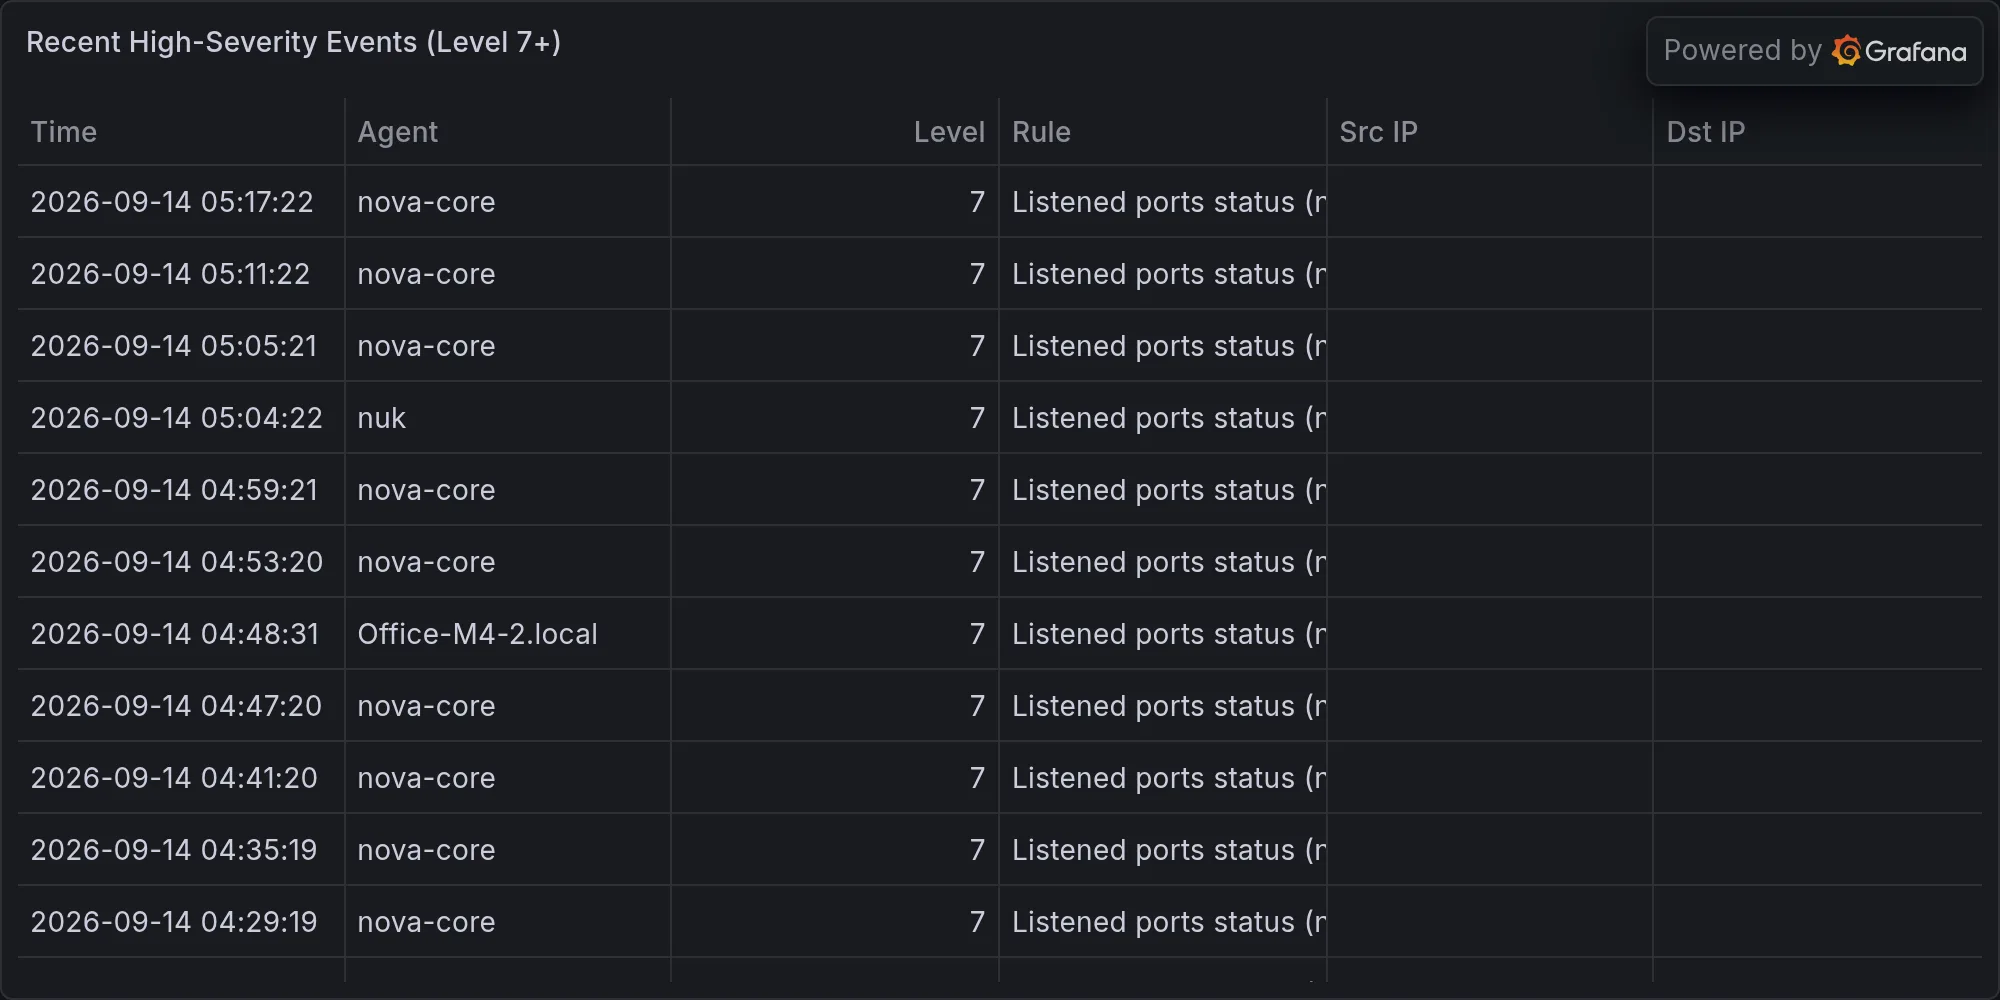
Recent high-severity events at publish time: