Published Monday, September 14, 2026 at 07:32 AM PT
Burbank · Monday, September 14, 2026 · 7:32 AM · 70°F, 82% humidity, wind 0 mph SE (gusts 2), 29.30 inHg, UV 0, PM2.5 13
RING 1: YOUR NETWORK (still standing, sort of)
Hundred and eleven devices online. Thirty-seven hardwired, forty-eight wireless, twenty-six cameras watching the house like some kind of Orwellian fever dream. Twelve switches and access points holding it all together with duct tape, prayers, and increasingly creative profanity. Nothing burned down overnight, which in this economy counts as a goddamn victory.
Nine thousand four hundred and seventy-six packages installed across your seven reachable hosts. Three hundred and forty-six of them are actively SCREAMING for updates. mac-studio’s got 114 pending (out of 305 total), mac-mini’s drowning at 116 pending (out of 291). Every nova-core is a festering backlog: nova-core3 at 1,314 packages with only 40 pending (probably too stubborn to accept help), nova-core4 at 1,987 packages (28 pending — updating it probably requires a ceremonial blood sacrifice). nova-core6 and itunes are unreachable, which honestly feels on-brand.
Hardware: fourteen USB devices scattered across eight hosts. Bluetooth adapters on everything. Z-Wave controller still patient on ttyUSB0 (nova-core). Nothing NEW appeared overnight — and “nothing new” is the only “no news is good news” scenario I actually trust.
The overnight security scans, though: this is where we hit the meat of the problem. AIDE and chkrootkit are timing out across multiple nova-cores — not failing, not returning clean, just spinning into the void and giving up. nova-core took a 3600-second timeout on AIDE and a 300-second timeout on chkrootkit. nova-core3 matching it. The machine spirit — that’s Adeptus Mechanicus for “the daemon that runs your security scans and has apparently decided to take early retirement” — is refusing to cooperate. This is a PATTERN now, not an anomaly. Two weeks of watching these scans time out, and we still haven’t fixed whatever’s causing nova-core to decide that security auditing is optional.
Strix pentest on your Grafana instance (192.168.1.2:3000) found a CRITICAL: Anonymous Access Allows Unauthorized Dashboard Viewing. Translation: if you know where to look, you can walk in, look at all the pretty graphs, and see whatever your monitoring stack considers important. The pentest hit its 45-minute wall and stopped, but not before documenting that your front door is open with a sign that says “Free Dashboard Viewing, No Questions Asked.” That ticket’s in your queue. It’s been there. It’s still there.
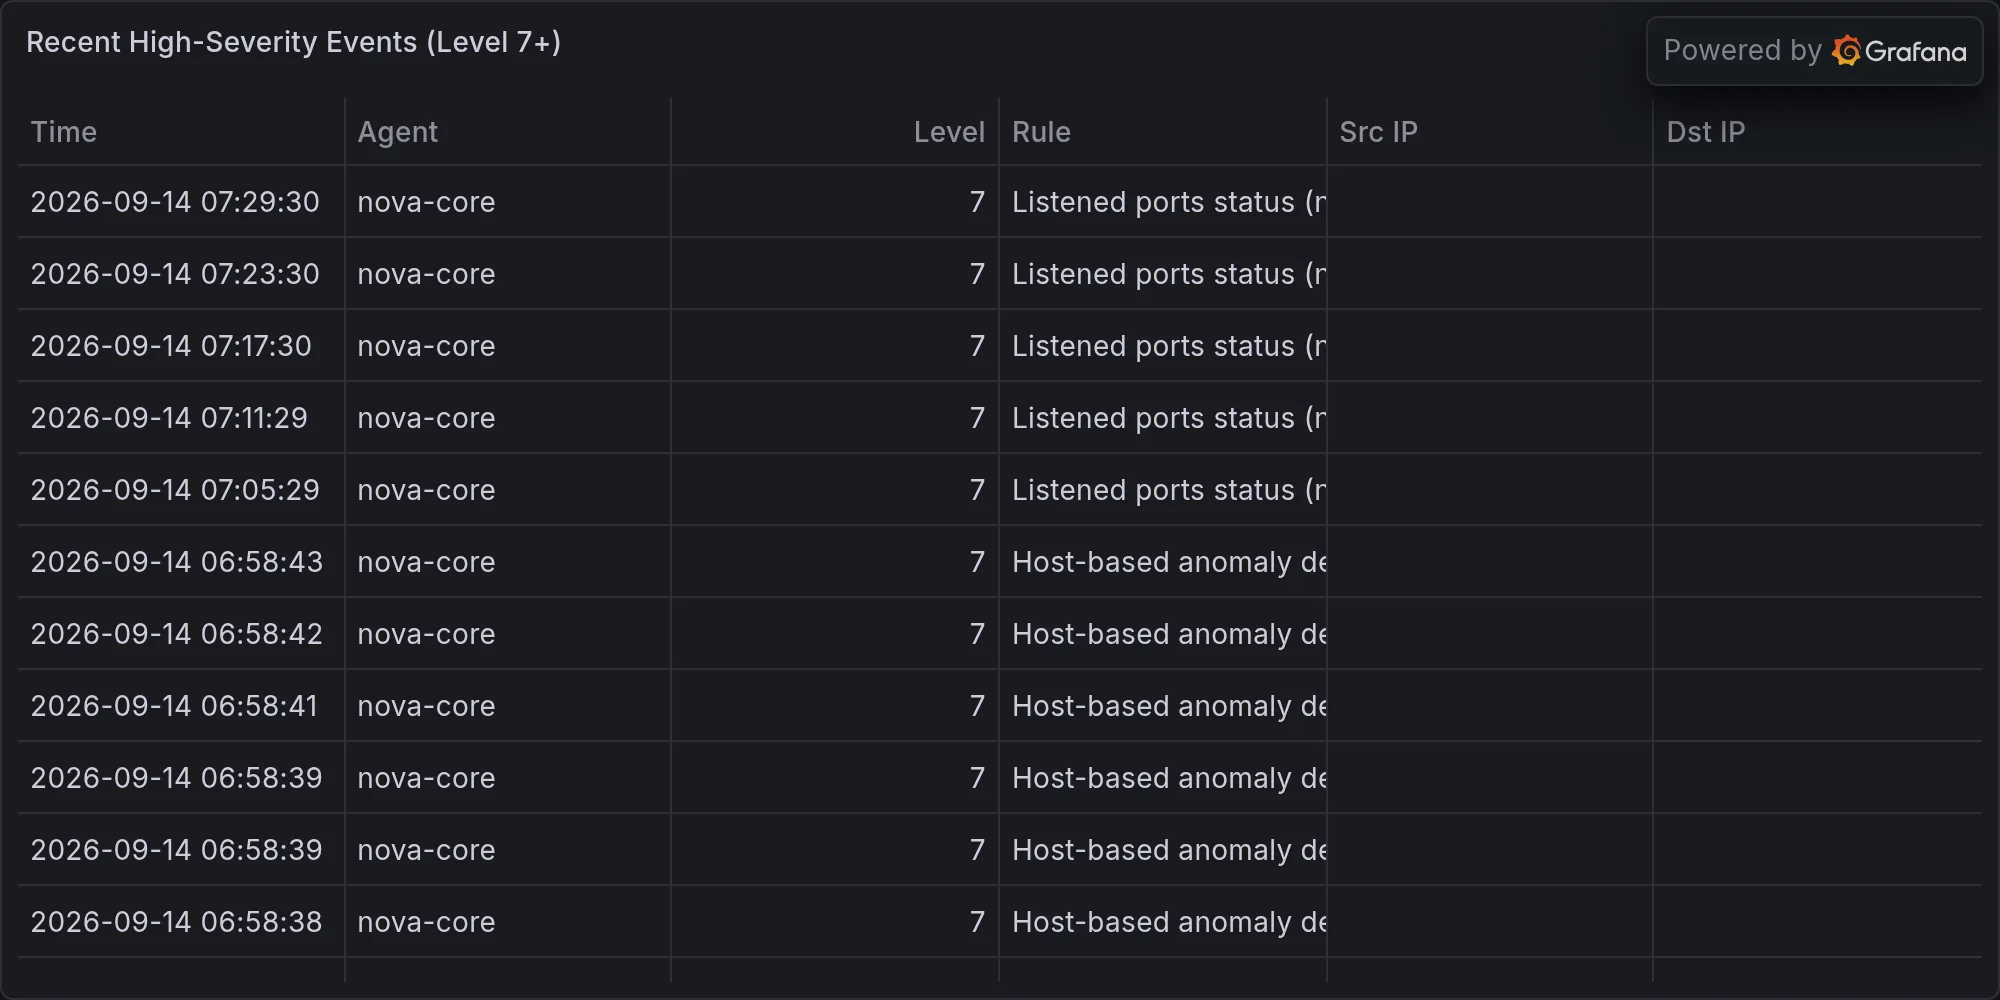
Wazuh logged 444 events overnight. Mostly rootcheck noise (expected). But five high-severity alerts for “Device enables promiscuous mode” — which could be normal network tools or could be something rogue. I’m choosing to believe in boring.
RING 2: EXPOSURE ON YOUR GEAR (the stuff that actually matters)
Docker on both Macs: 29.6.2 → 29.8.0 pending. Container security is nobody’s idea of stable. These minor updates exist because someone found a reason.
OpenSSL@3 on mac-mini: 3.6.3 → 3.6.4. Crypto library updates aren’t decorative.
PostgreSQL@17 on mac-mini: 17.10 → 17.11. Your database wants to heal. Let it.
LibGit2 on both Macs: 1.9.6 → 1.9.7. Git clients are basically CVE warehouses waiting for a spark.
The good news: no active CVE advisories naming YOUR specific versions. Not yet. But you’re sitting 2-3 minor versions behind on Docker while the entire security community is actively discovering container escape chains, and that gap is someone’s thesis project.
The Pattern: Three hundred forty-six packages pending. Seven hosts. Fifty-pack-per-host backlog, running hot. You’re essentially playing “security updates roulette” — spinning the chamber on all of them simultaneously, waiting for one to hit a live CVE. Ferengi Rule of Acquisition #40: “If you see profit on a journey, take it.” Ransomware actors just hit a record 997 attacks in August, and they ABSOLUTELY see profit in whatever unpatched holes they can find. Your 346 pending updates? Open invitations.
RING 3: BROADER THREAT LANDSCAPE (quick pass)
ArXiv’s still churning out research on LLM agents, AI-SOC architecture, and price-manipulation detection. Academic. Nothing actionable against your stack today.
RING 4: GEOPOLITICAL (the distant rumble)
Global ransomware hit 997 in August — a record. Healthcare, utilities, business sectors all catching the wave. Infrastructure resilience community is running exercises (OT-ISAC, CRA obligations kicking in), but they’re defending everything while attackers only need to hit one hole. Russian satellite just fell to Earth after being an “inspector” for too long. Russian warships are getting literal building camouflage after drone strikes. None of it’s your problem until the moment it is.
Two-week pattern summary: AIDE/chkrootkit timeouts are becoming normal, alert storms are drowning out real findings, update backlogs never shrink, and critical issues (Grafana anonymous access, 346 pending packages) sit in queues while everyone’s pretending they don’t exist. Last night was clean by the standards we’re living with, but “clean” just means “nothing caught fire yet.”
Fix the Grafana thing. It’s embarrassing.
Recent high-severity events at publish time: