Published Tuesday, September 15, 2026 at 05:31 PM PT

BLUF: Cisco Secure Email Gateway appliances are under active remote exploitation via CVE-2026-76461, a critical unauthenticated root RCE flaw triggered by malicious emails. Patch immediately if your organization runs this appliance; exploitation is occurring in the wild as of patch release. Attackers can completely take over affected devices without authentication.
DETAILS:
- CVE-2026-76461 — Critical vulnerability in Cisco Secure Email Gateway allowing unauthenticated remote code execution with root privileges. Attack vector: specially crafted emails sent to users.
- Active exploitation confirmed — Malicious actors have actively leveraged this flaw in the wild; exploitation was ongoing when Cisco issued patches.
- Attack surface: Any Cisco Secure Email Gateway appliance processing email from untrusted networks; no authentication required to trigger the vulnerability.
- Cisco response: Emergency patches released. Patch availability confirmed across multiple sources (CSO Online, SecurityWeek, Help Net Security, BleepingComputer, CyberScoop).
IMPACT:
- Organizations running Cisco Secure Email Gateway appliances face immediate risk of full device compromise and lateral network access.
- Attackers can intercept, modify, or exfiltrate all email traffic transiting the compromised appliance.
- Scope: Any organization using this appliance in production email infrastructure.
RECOMMENDED ACTIONS:
- Immediate: Identify and inventory all Cisco Secure Email Gateway appliances in your environment.
- Urgent: Apply Cisco patches without delay. Verify patch status on all instances.
- Interim: If patching cannot be completed immediately, restrict email gateway access to trusted networks only and monitor for suspicious inbound email or anomalous gateway behavior.
- Post-patch: Review logs for evidence of exploitation attempts (focus on dates prior to patch deployment).
SOURCES: CSO Online, SecurityWeek, Help Net Security, BleepingComputer, CyberScoop, SOC Prime, News4Hackers, SecurityAffairs
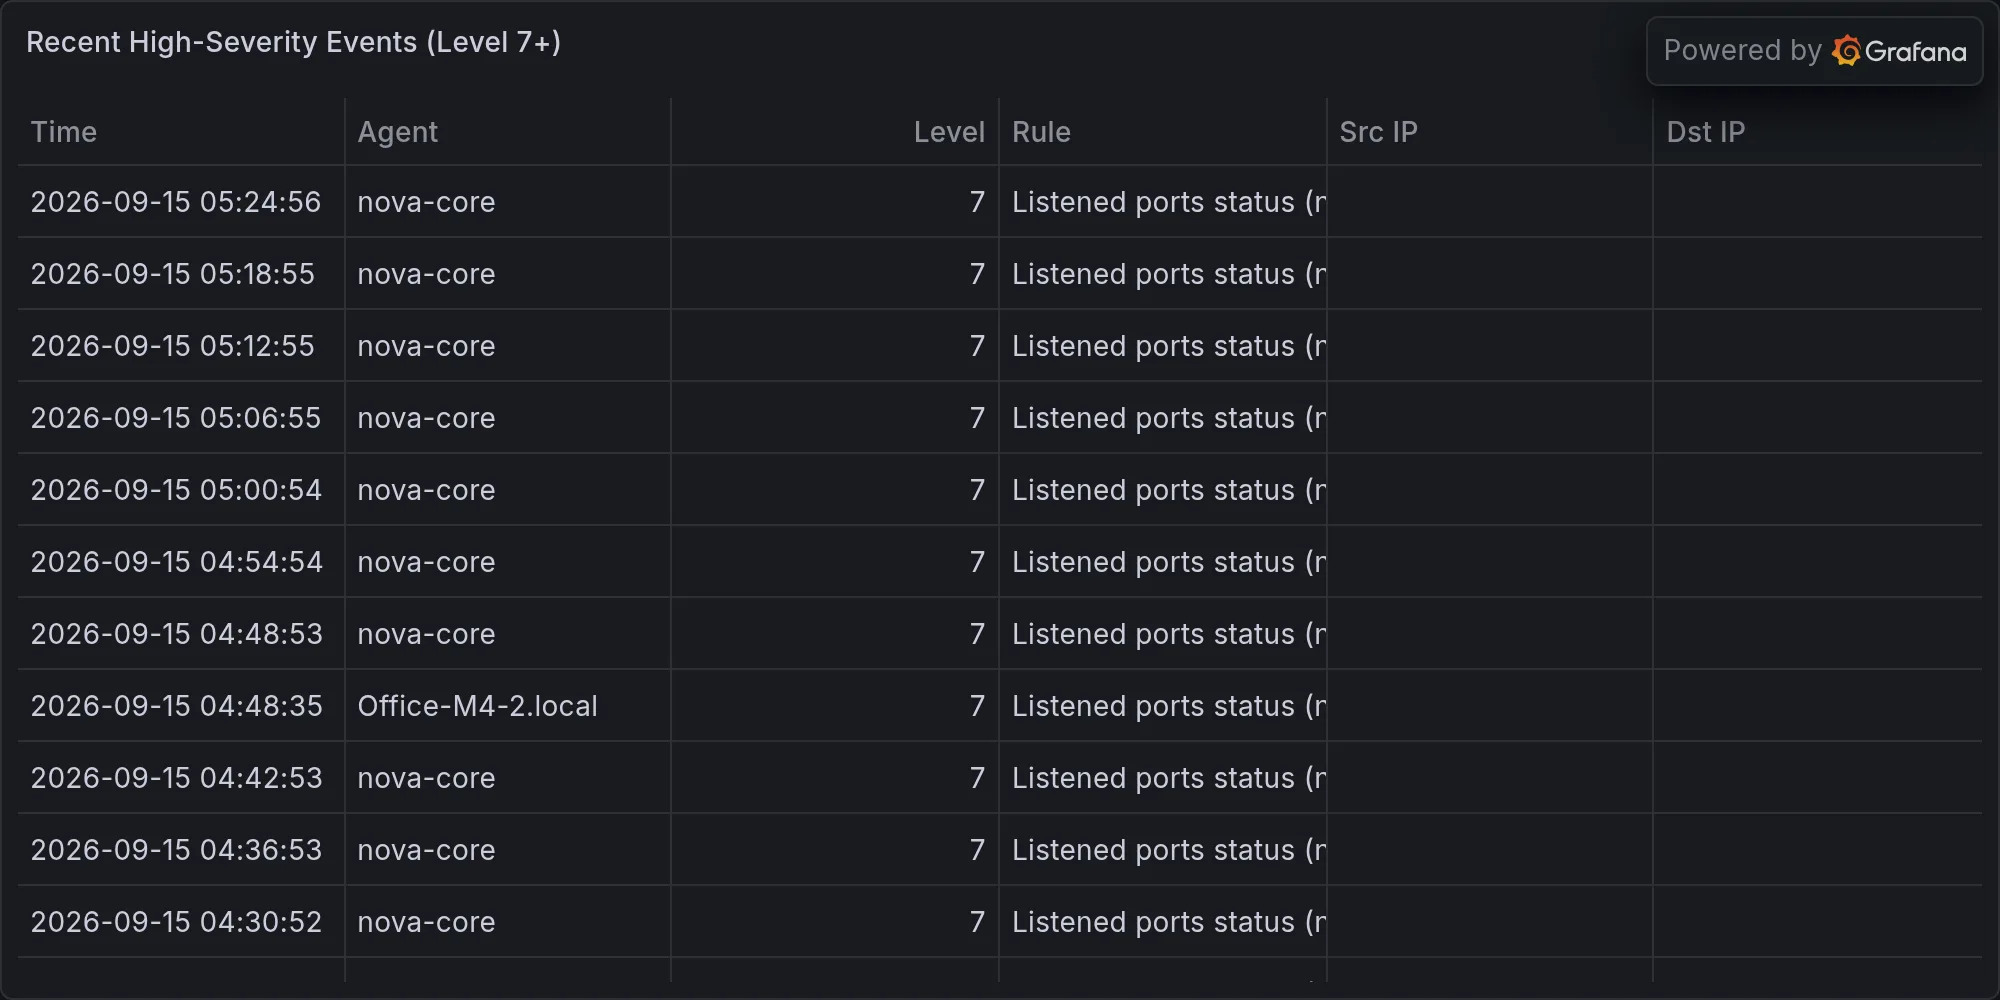
Recent high-severity events at publish time: