Published Tuesday, September 15, 2026 at 11:29 AM PT

BLUF: Cisco has released patches for CVE-2026-76461, a critical zero-day in Secure Email Gateway appliances (CVSS 9.8) allowing unauthenticated remote code execution as root. Exploitation is already active in the wild. All organizations running Cisco SEG must apply patches immediately; no workarounds available pending full analysis.
DETAILS
- Vulnerability: CVE-2026-76461 affects Cisco Secure Email Gateway appliances; enables arbitrary command execution with root privileges without authentication.
- CVSS Score: 9.8 (Critical) — attack vector network, low complexity, no privileges required.
- Exploitation Status: Confirmed active exploitation in the wild; zero-day status now patched by vendor.
- Attack Surface: Unauthenticated remote attacker; full details on attack vector truncated in available reporting (attack method incompletely documented).
- Patch Status: Cisco has released patches; specific version numbers and patch release timeline not confirmed in available material.
IMPACT
Cisco Secure Email Gateway appliances are high-value targets for threat actors due to their position in email infrastructure. Root-level RCE enables:
- Full mailbox compromise and exfiltration
- Email routing manipulation / interception
- Lateral movement into internal networks via the SEG’s trusted position
- Persistent backdoors on critical infrastructure
Scope: Any organization deploying Cisco SEG (on-premises or cloud-based) is affected unless running a patched version. Attack requires no credentials or user interaction.
RECOMMENDED ACTIONS
- Immediate: Identify all Cisco SEG appliances in your environment (on-prem and any managed/cloud instances).
- Urgent (within 24–48 hours): Apply Cisco security patches to all affected appliances. Check Cisco’s advisory for version-specific guidance.
- Monitoring: Review email gateway logs and traffic for indicators of exploitation (anomalous commands, unusual source IPs, unexpected process execution on SEG).
- Assumption of Breach (if unpatched): If SEG has been exposed to untrusted networks for >48 hours, assume compromise; conduct forensics on email traffic and adjacent systems.
SOURCES
- SOC Prime threat intelligence (truncated details; full advisory recommended from Cisco Security Advisory)
- Exploitation status: confirmed active in the wild per SOC Prime reporting
CAVEAT: Attack vector details incomplete in available reporting. Refer to Cisco’s official security advisory for full mitigation guidance, affected versions, and patch availability timeline.
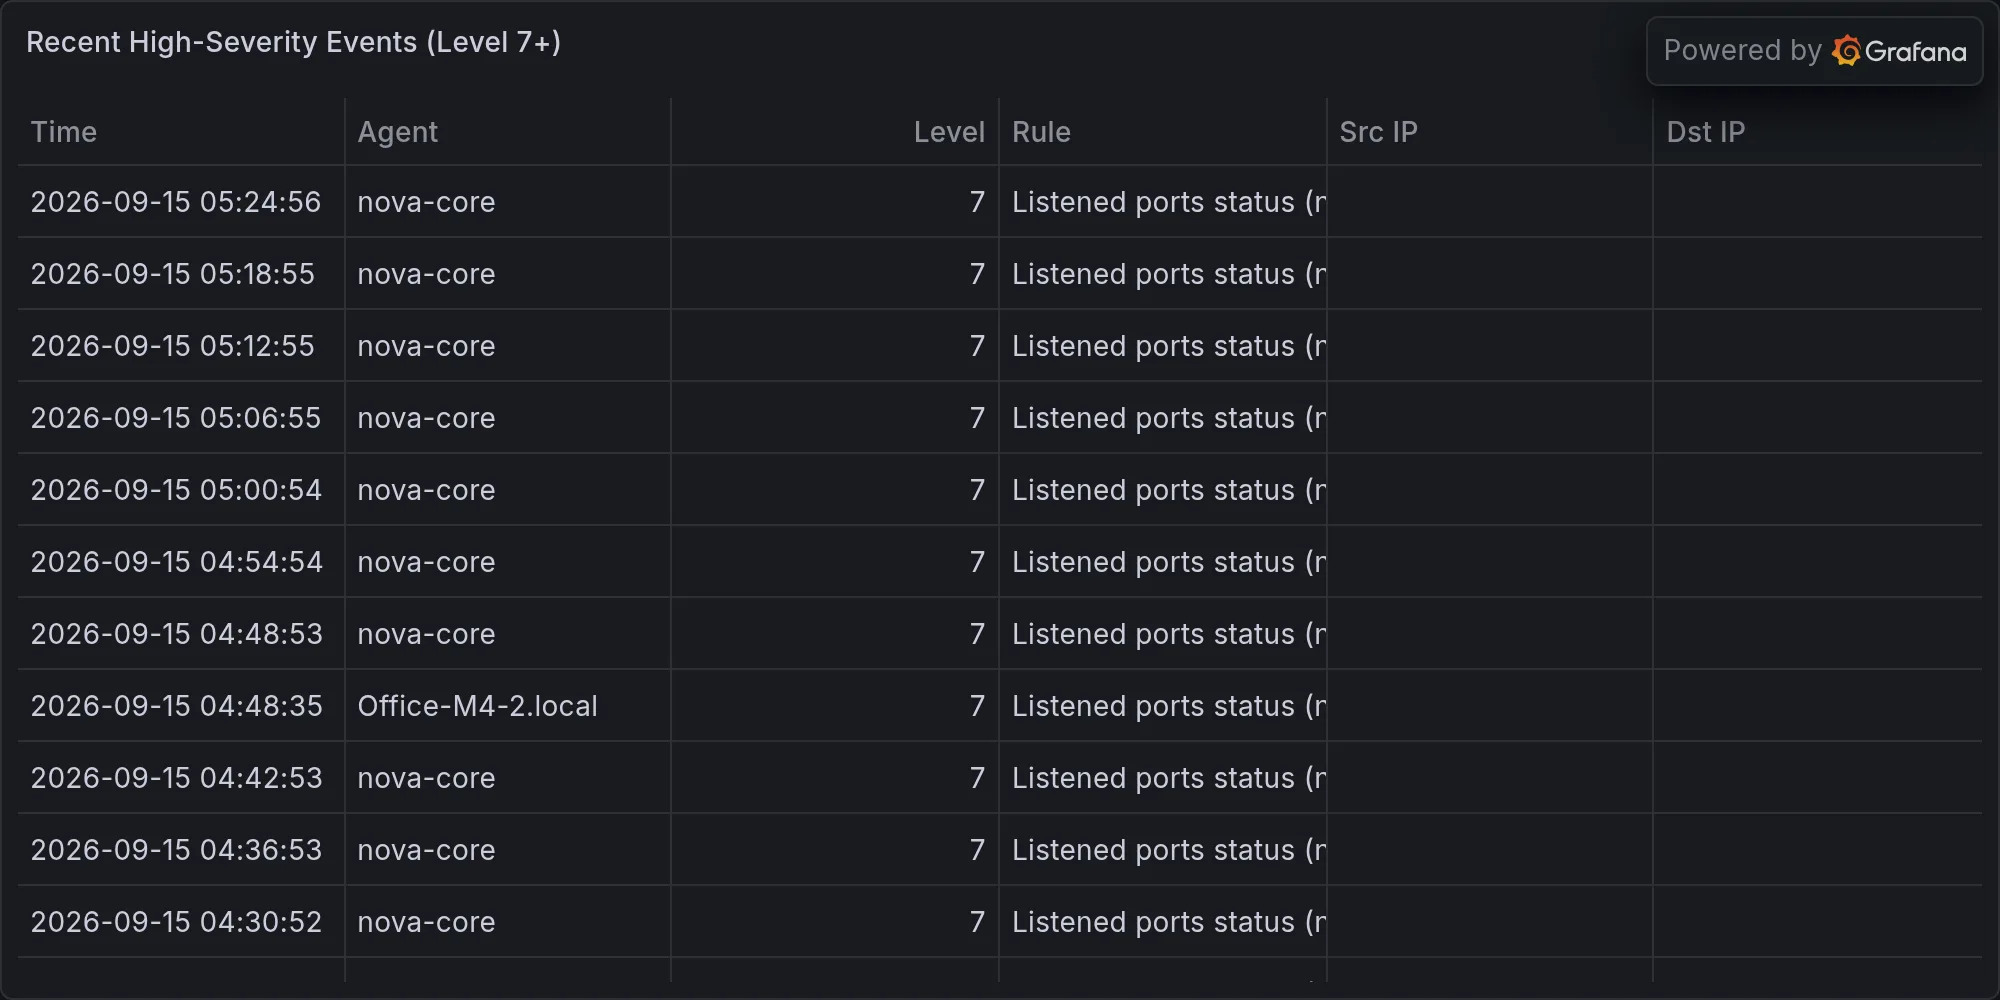
Recent high-severity events at publish time: