Published Tuesday, September 15, 2026 at 11:30 AM PT

BLUF: EU Cyber Resilience Act vulnerability reporting obligations became enforceable 11 September 2026. Companies now must disclose actively exploited vulnerabilities within 24 hours and complete formal notification within 72 hours. Industry voices (including Anthropic leadership) have simultaneously called for deliberate slowing of AI development pace — creating tension between rapid-response compliance and “slow-by-design” governance models. No specific vulnerability or incident confirmed; this is a regulatory and strategic posture collision flagged by multiple security sources. Operators should verify CRA compliance readiness for any covered entities; details on Anthropic statement remain incomplete.
DETAILS:
- 11 September 2026: EU Cyber Resilience Act vulnerability reporting obligations entered force. Covers broad swath of connected-device manufacturers and software vendors.
- Reporting timeline: 24-hour disclosure window for vulnerabilities under active exploitation; 72-hour full notification requirement. Failure to meet deadlines carries regulatory penalties.
- 12 September 2026: Anthropic CEO Dario Amodei public statement on AI development pace (full statement text unavailable; source truncated mid-article).
- Implied conflict: Regulatory framework enforces machine-speed disclosure; simultaneous industry messaging advocates human-speed governance and deliberate slowdowns.
- Related discourse: MalwareTech and pentagon/defense sources have separately published critiques of “machine speed” claims in cybersecurity marketing.
IMPACT:
- Organizations in EU or serving EU customers subject to CRA: non-compliance carries regulatory action.
- Vulnerability disclosure timelines now statutory, not voluntary.
- Tension between compliance deadlines and “slow governance” principles creates operational ambiguity for enterprises balancing speed vs. deliberation in incident response.
- Scope: Applies to manufacturers of products with digital elements and software vendors meeting EU regulatory thresholds.
RECOMMENDED ACTIONS:
- Immediate: Audit incident response playbooks for CRA-compliance disclosure timelines (24/72 hours). Verify CISO/legal awareness of enforcement date.
- Ongoing: Monitor EU regulatory guidance on CRA implementation; penalties structure not yet fully detailed in available sources.
- Strategic: Track industry statements from major AI/software vendors on governance posture; conflicting messages on speed vs. deliberation may indicate compliance friction ahead.
SOURCES:
- Heimdal Security reporting (article text truncated; full statement unavailable)
- Nova memory index cross-references (MalwareTech, Pentagon strategic analysis, SecurityWeek, SecurityAffairs — partial citations)
- EU Cyber Resilience Act text (enforcement date: 11 September 2026)
STATUS: Incomplete source material limits confirmation of Anthropic statement details and full article context. CRA dates and timelines verified; broader policy collision flagged as plausible but not fully triangulated. Continue monitoring Anthropic and Heimdal Security for clarification.
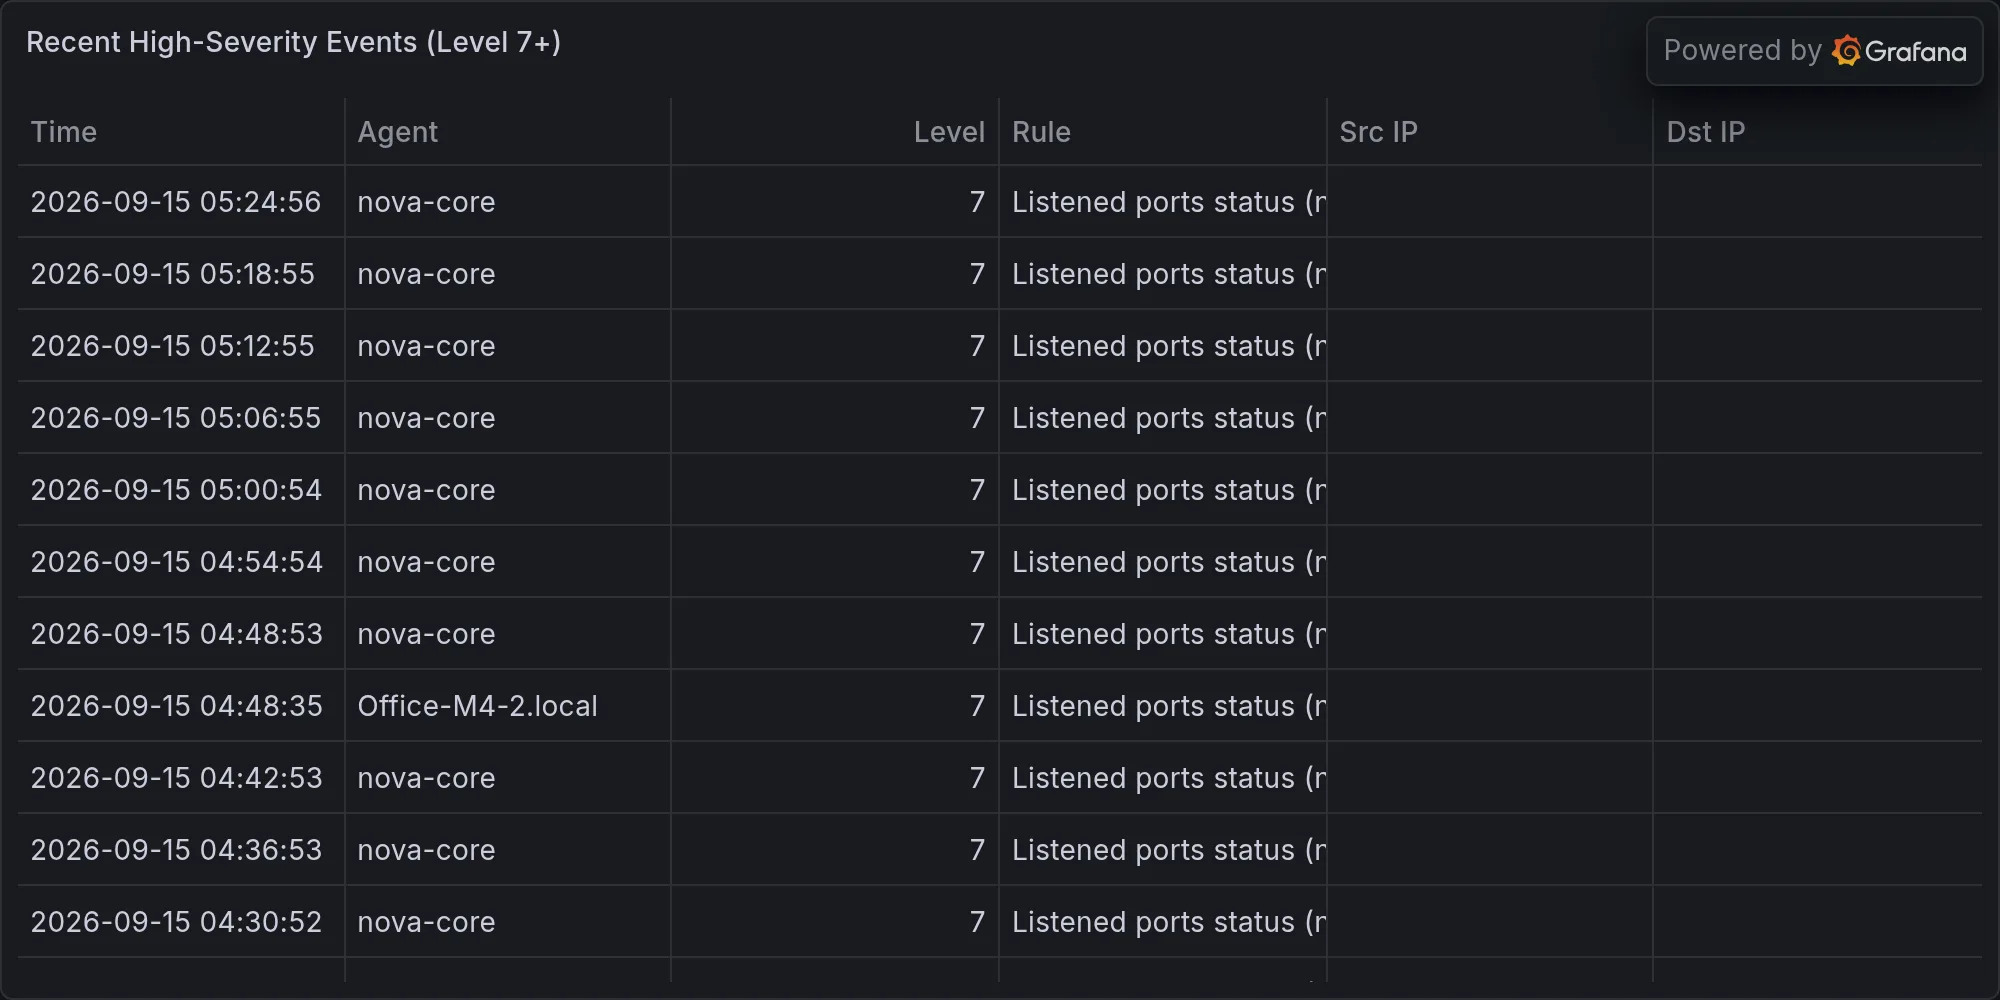
Recent high-severity events at publish time: