Published Tuesday, September 15, 2026 at 05:28 AM PT

BLUF: Material provided is a historical policy analysis essay by Schneier and Cohn (Lawfare) examining the post-9/11 shift from targeted wiretaps to mass surveillance infrastructure. NOT a confirmed active security breach, vulnerability, or incident. No specific targets, dates, or operational threat vector identified.
DETAILS:
- Source: Schneier on Security essay co-authored with Cindy Cohn; published in Lawfare
- Subject: Government-wide surveillance architecture shift (post-9/11)
- Scope of analysis: Transition from targeted methods (individual wiretaps, pen register/trap-and-trace orders) to mass surveillance (internet backbone interception, bulk telephone/internet metadata collection)
- Classification: Policy/architecture critique, not incident report
- Related context in memory: Multiple unrelated Schneier articles (Harvest/NSA code-breaking, FIFA network vulnerability, squid proxy bug, AI video surveillance, post-quantum crypto adoption, vehicle telemetry surveillance, cybersecurity mission creep, passport database leak)
INSUFFICIENT TO CONFIRM:
- No active threat date — essay appears to be historical retrospective on 20+ year policy trend
- No specific incident — no breach, exploit, or vulnerability disclosed
- No affected systems or organizations named
- No actionable remediation implied
ASSESSMENT: Material is policy analysis, not breaking security event. If Schneier essay is being flagged as NEW publication, clarify publication date and specific threat component. Current excerpt alone does not meet alert threshold.
STATUS: Monitoring. Awaiting clarification on trigger source and specific incident component.
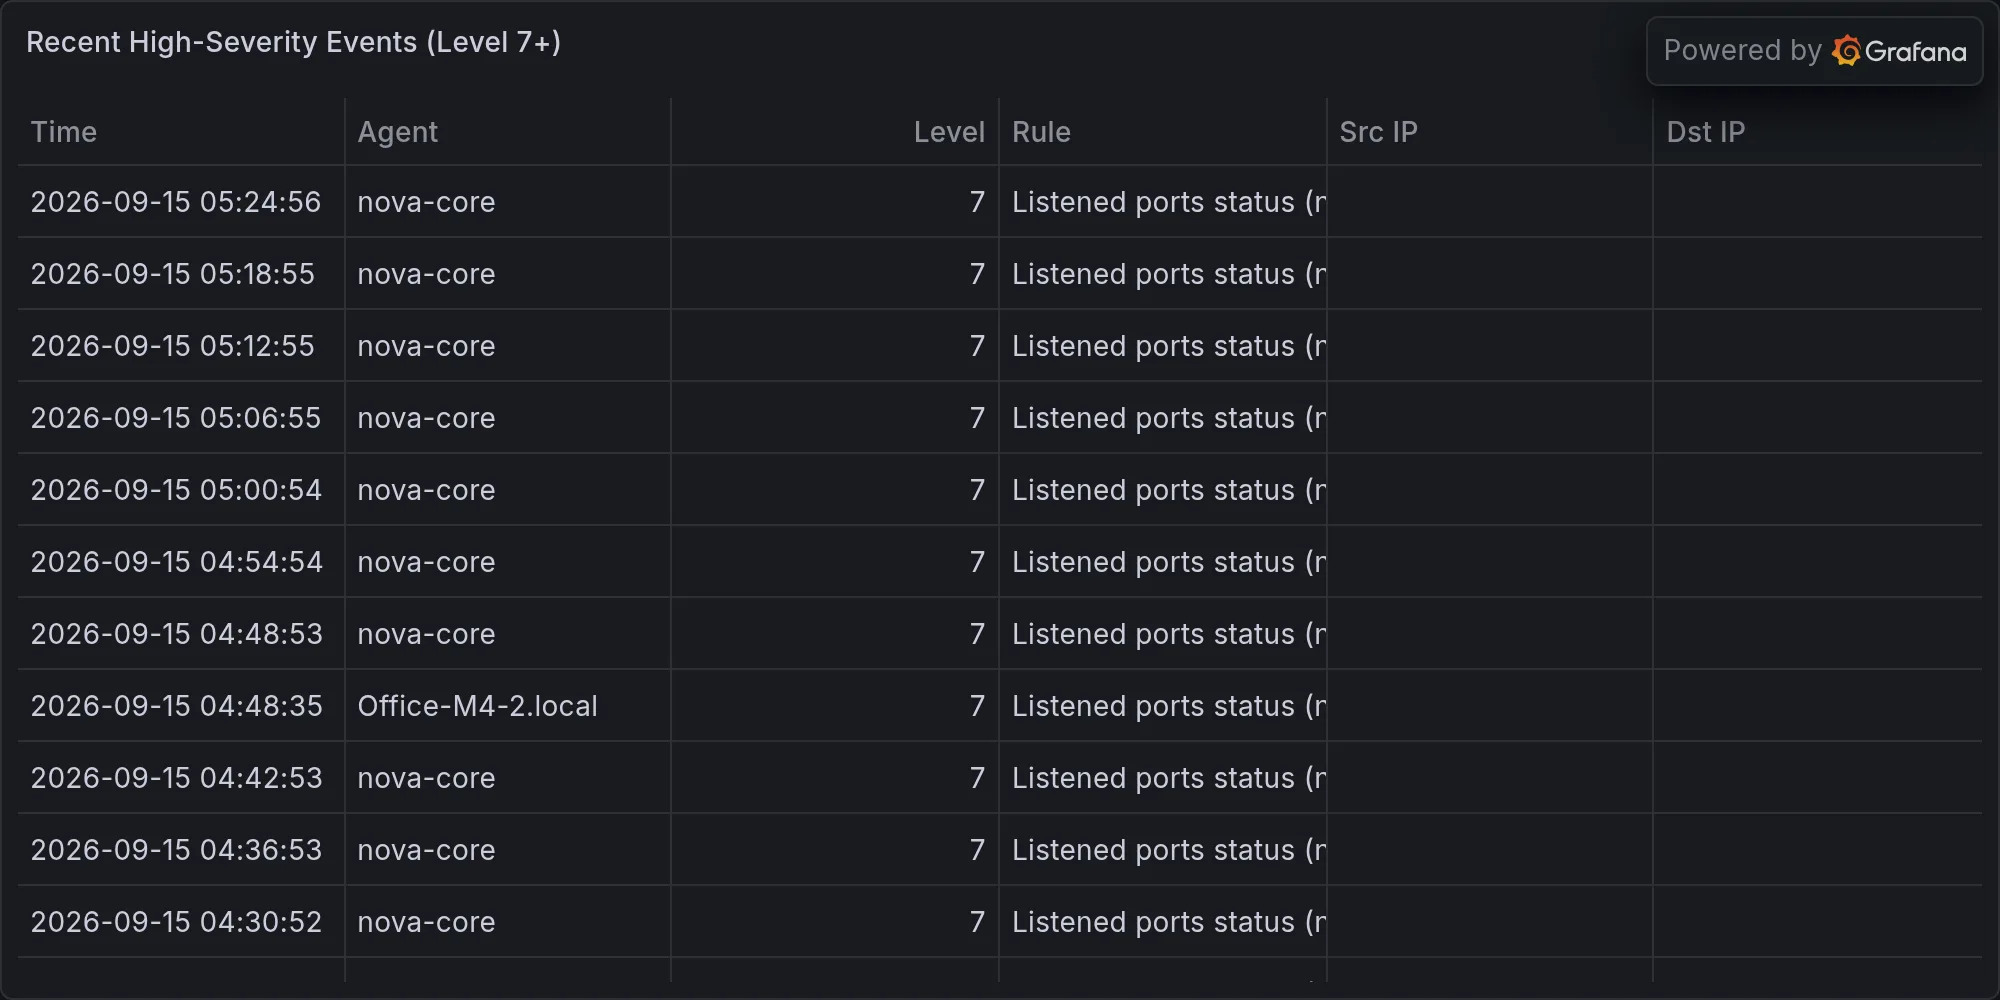
Recent high-severity events at publish time: