Published Wednesday, September 16, 2026 at 10:01 AM PT

BLUF: Apple has released a macOS security update (version under review). Full CVE and patch details available at https://support.apple.com/en-us/100100. All macOS administrators must review documentation immediately and initiate rapid testing and deployment. Specific vulnerability count and severity distribution pending detailed CVE review.
DETAILS:
- Apple has released a macOS security update (trigger references “macOS is 27”; official version designation requires documentation confirmation)
- Complete CVE list, CVSS scores, affected versions, and remediation guidance available at https://support.apple.com/en-us/100100
- Apple’s recent macOS release cycles have patched 150+ vulnerabilities per release; iOS 27 / macOS Golden Gate 27 combined addressed 200+ total vulnerabilities across iOS, macOS, and Safari
- Typical patched categories based on recent releases: WebKit engine flaws, kernel and system services, cryptographic implementations
- Apple accelerated patch cadence in response to AI-powered exploit development acceleration
- No active exploitation reported in trigger event
IMPACT:
- All macOS systems running the released version
- Organizational risk scope depends on vulnerability severity distribution—to be determined via CVE documentation review
- Patch delay increases exploitation risk; network-facing systems at highest risk
- Exposure estimate becomes clear after CVE triage against internal fleet inventory
RECOMMENDED ACTIONS (Urgent — First 24 Hours):
- Document: Pull complete CVE list, CVSS scores, and version mappings from https://support.apple.com/en-us/100100
- Triage: Sort by severity; flag CVSS 9.0+ and remote-code-execution variants
- Assess: Cross-reference against macOS fleet; identify affected system count by criticality
- Test: Deploy to non-production systems within 6-12 hours; target completion in 48 hours
- Deploy: Sequence production rollout by system criticality and CVE severity
SOURCES:
- Apple Product Security: https://support.apple.com/en-us/100100
- Context: iOS 27 / macOS Golden Gate 27 release patterns (200+ vulnerabilities)
- Alert trigger: Nova Security Monitoring (macOS release notification)
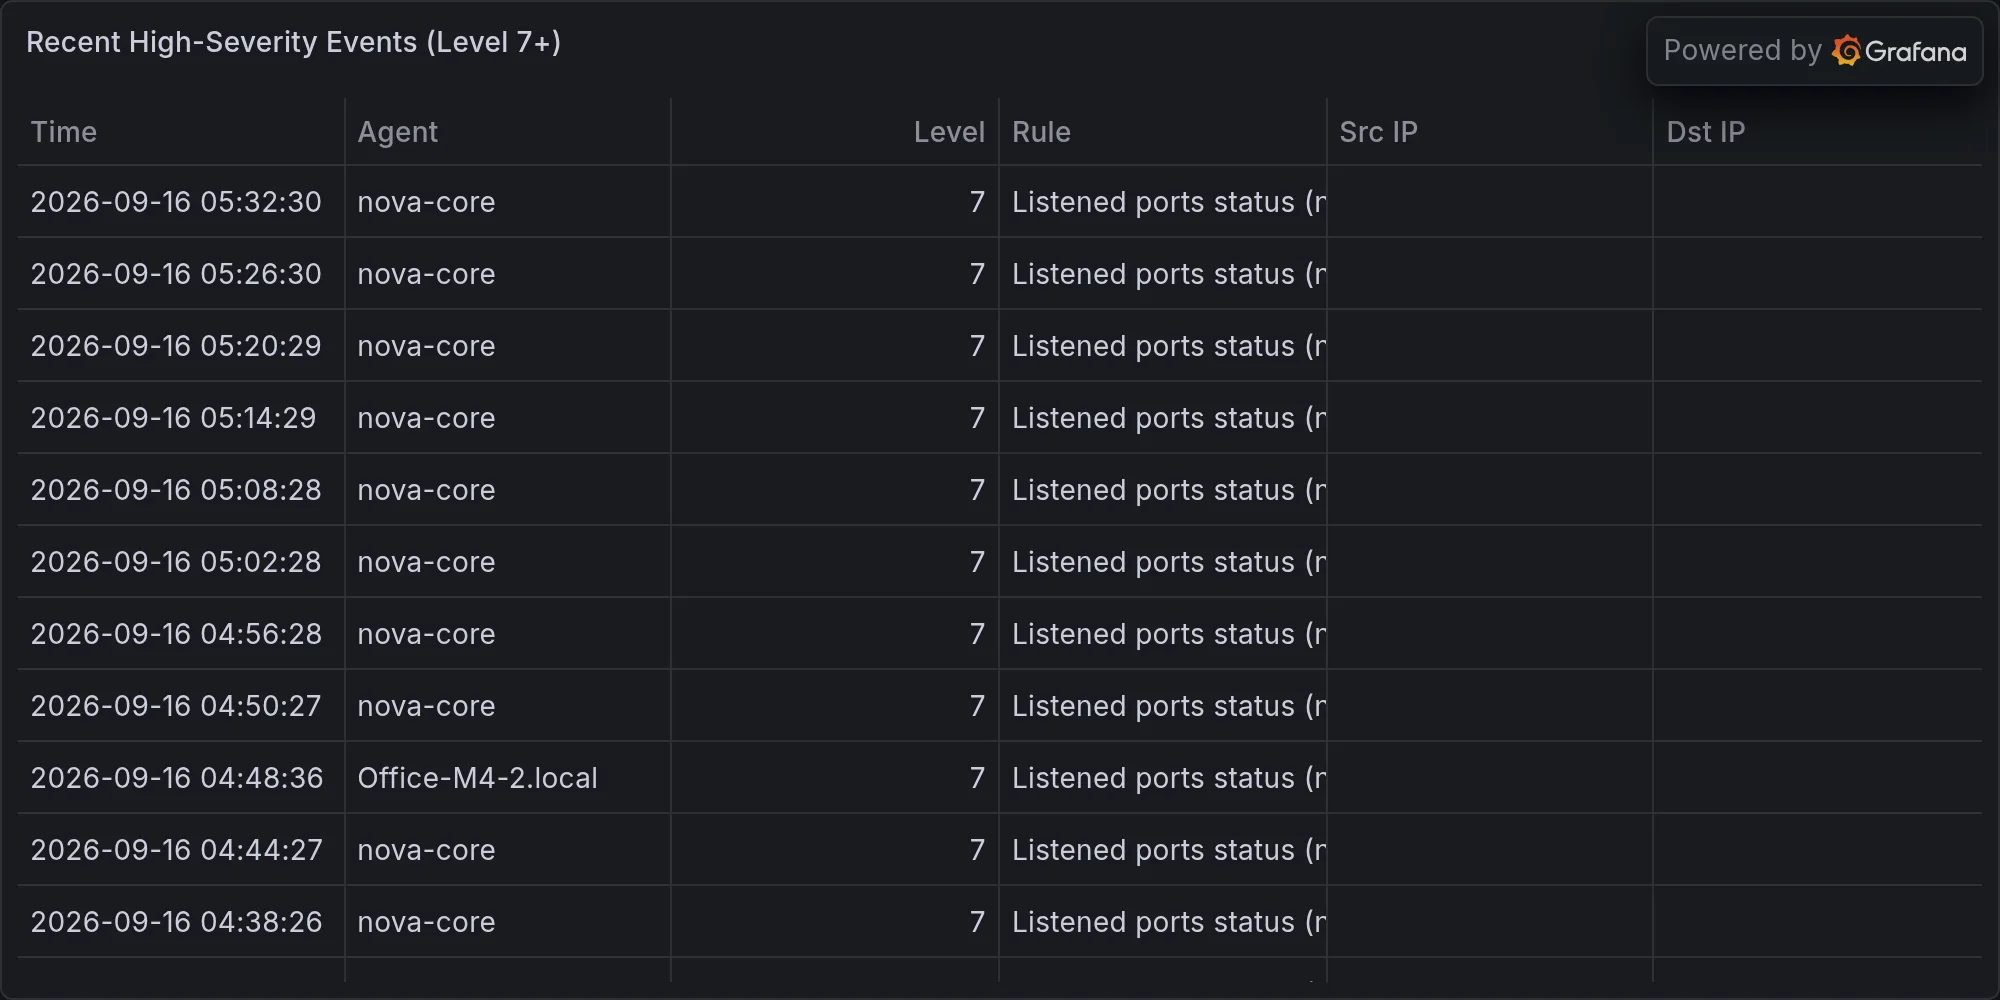
Recent high-severity events at publish time: