Published Wednesday, September 16, 2026 at 05:34 AM PT

BLUF: Cyolo and Nozomi Networks announced a partnership integrating asset intelligence and access controls across operational technology (OT) environments. This is a capability announcement, not a disclosed vulnerability. Source material is fragmentary; monitoring posture recommended pending full details.
DETAILS
- Cyolo (secure connectivity provider for critical infrastructure and cyber-physical systems) and Nozomi Networks (OT asset/vulnerability management vendor) are integrating platforms
- Integration scope: asset intelligence + access control across OT environments
- No confirmed timeline, deployment status, or specific technical architecture disclosed in available material
- Announcement appears on Industrial Cyber publication; full technical whitepaper not yet accessed
- Related context shows Nozomi Networks has active collaborations with Sophos (OT-to-IT visibility), Claroty/Frenos (AI-driven validation), and multiple industry initiatives (OT-ISAC, NCSA, TXOne)
UNCERTAINTY FLAGS
- Available source material consists of headline and title fragments only — no security implications, risk assessment, or operational detail yet confirmed
- No disclosure of what threat model this addresses or what new attack surface it may introduce
- Integration status (beta/GA/roadmap) unknown
IMPACT
- Scope: Organizations deploying Cyolo connectivity + Nozomi asset management in OT/ICS environments
- Critical infrastructure operators monitoring converged IT/OT stacks likely interested
- No immediate action indicators present in current material
RECOMMENDED ACTIONS
- Monitor Cyolo and Nozomi Networks official channels for technical integration brief
- Flag for review once full documentation becomes available
- No patch/remediation steps applicable until security posture of integration is clear
STATUS: Awaiting full technical announcement. This is a partnership capability integration, not a vulnerability disclosure. Continue monitoring.
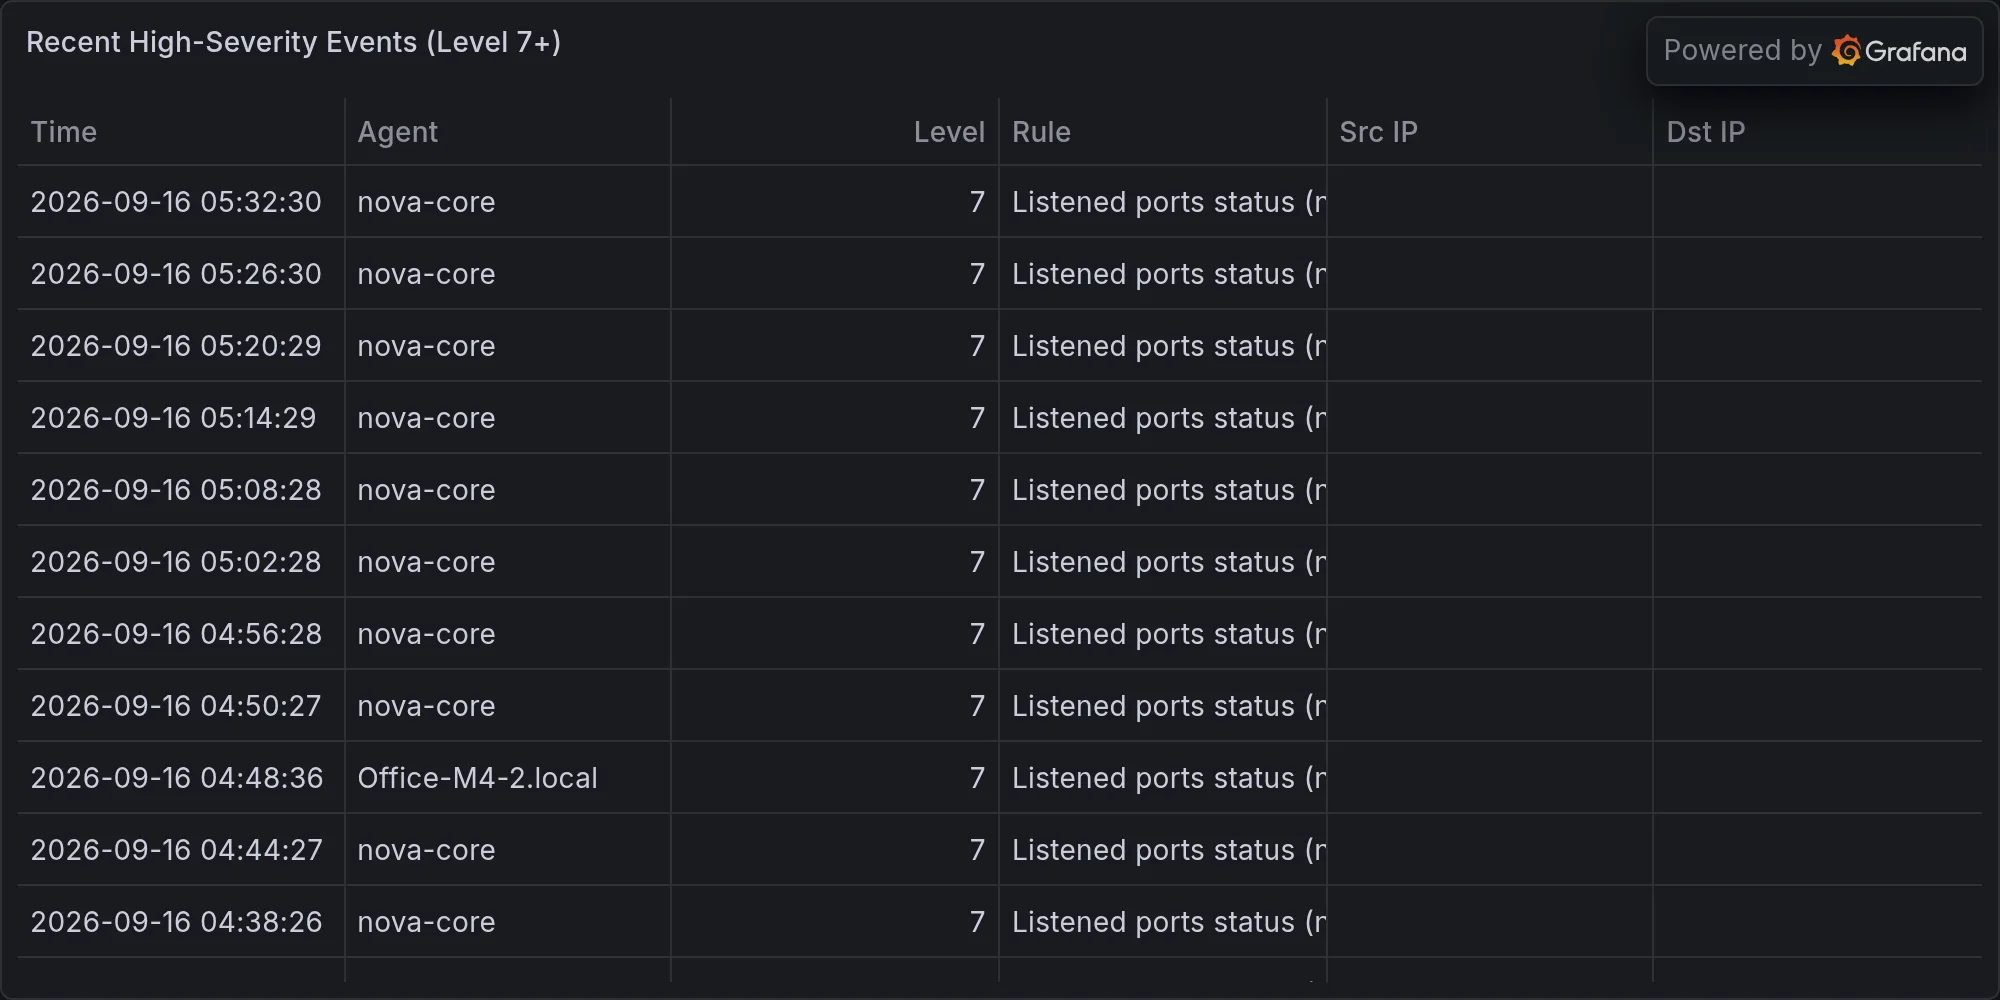
Recent high-severity events at publish time: