Published Thursday, September 17, 2026 at 05:34 PM PT

BLUF: Cisco has released emergency patches for an actively exploited authentication bypass vulnerability (CVSS 10.0) affecting Cisco Identity Services Engine (ISE), used for enterprise network access control and policy enforcement. This is the second critical zero-day Cisco has patched in one week. Enterprises running ISE must apply patches without delay; this vulnerability is being exploited in the wild against production systems.
DETAILS
• CVE-2026-76460 — Cisco ISE authentication bypass with CVSS 10.0 severity; enables attackers to bypass network access controls on enterprise IAM systems in active exploitation.
• Active Exploitation Confirmed — Multiple security researchers and vendors confirm malicious actors are weaponizing this flaw against production ISE deployments; attack rate and sophistication unknown but trending upward.
• Second Zero-Day in One Week — Cisco also patched CVE-2026-76461 (Cisco Secure Email Gateway root RCE) earlier this week, signaling an unusual attack surface spike against Cisco network infrastructure.
• ISE Scope — Cisco ISE is mission-critical for enterprise network access control (NAC), policy enforcement, and authentication. Compromise allows attackers to assume authenticated user/device status and move laterally within the network.
• Patches Released — Cisco has released patches; specific patch version and affected platforms not yet detailed in available sources. Check Cisco security advisory for your platform/version.
IMPACT
Enterprises running Cisco ISE face immediate network compromise risk. Successful exploitation allows:
- Bypass of network admission policies
- Lateral movement as trusted network endpoints
- Potential for insider-like persistence and data exfiltration
Scope: Any organization with ISE deployed for network access control (common in Fortune 500, healthcare, financial services, government, telecommunications).
Attack Pattern: Exploitation is active and untargeted; no evidence of selective targeting. Expect broad scanning and probing for vulnerable ISE instances reachable from the internet or compromised VPNs.
RECOMMENDED ACTIONS
- Immediate: Identify all Cisco ISE instances (on-premises and cloud-hosted); cross-reference with Cisco’s affected version list (advisory TBD).
- Within 24 Hours: Apply Cisco’s released patch to all ISE systems. If patch unavailable for your version, engage Cisco TAC for timeline and interim mitigations (network segmentation, access restrictions).
- Monitoring: Enable ISE authentication logging; search for anomalous login patterns, unexpected privilege escalation, or failed-then-succeeded auth sequences.
- Escalate: Notify CISO and infrastructure teams; this requires mandatory out-of-cycle patching.
SOURCES
- CSO Online, The Hacker News, BleepingComputer, CyberScoop, SOC Prime, Help Net Security, news4hackers — all reporting active Cisco ISE CVE-2026-76460 exploitation and CVE-2026-76461 email gateway RCE.
STATUS: CONFIRMED / ACTIVE EXPLOITATION — Watch Cisco security advisories for patch release details and affected platform/version matrix.
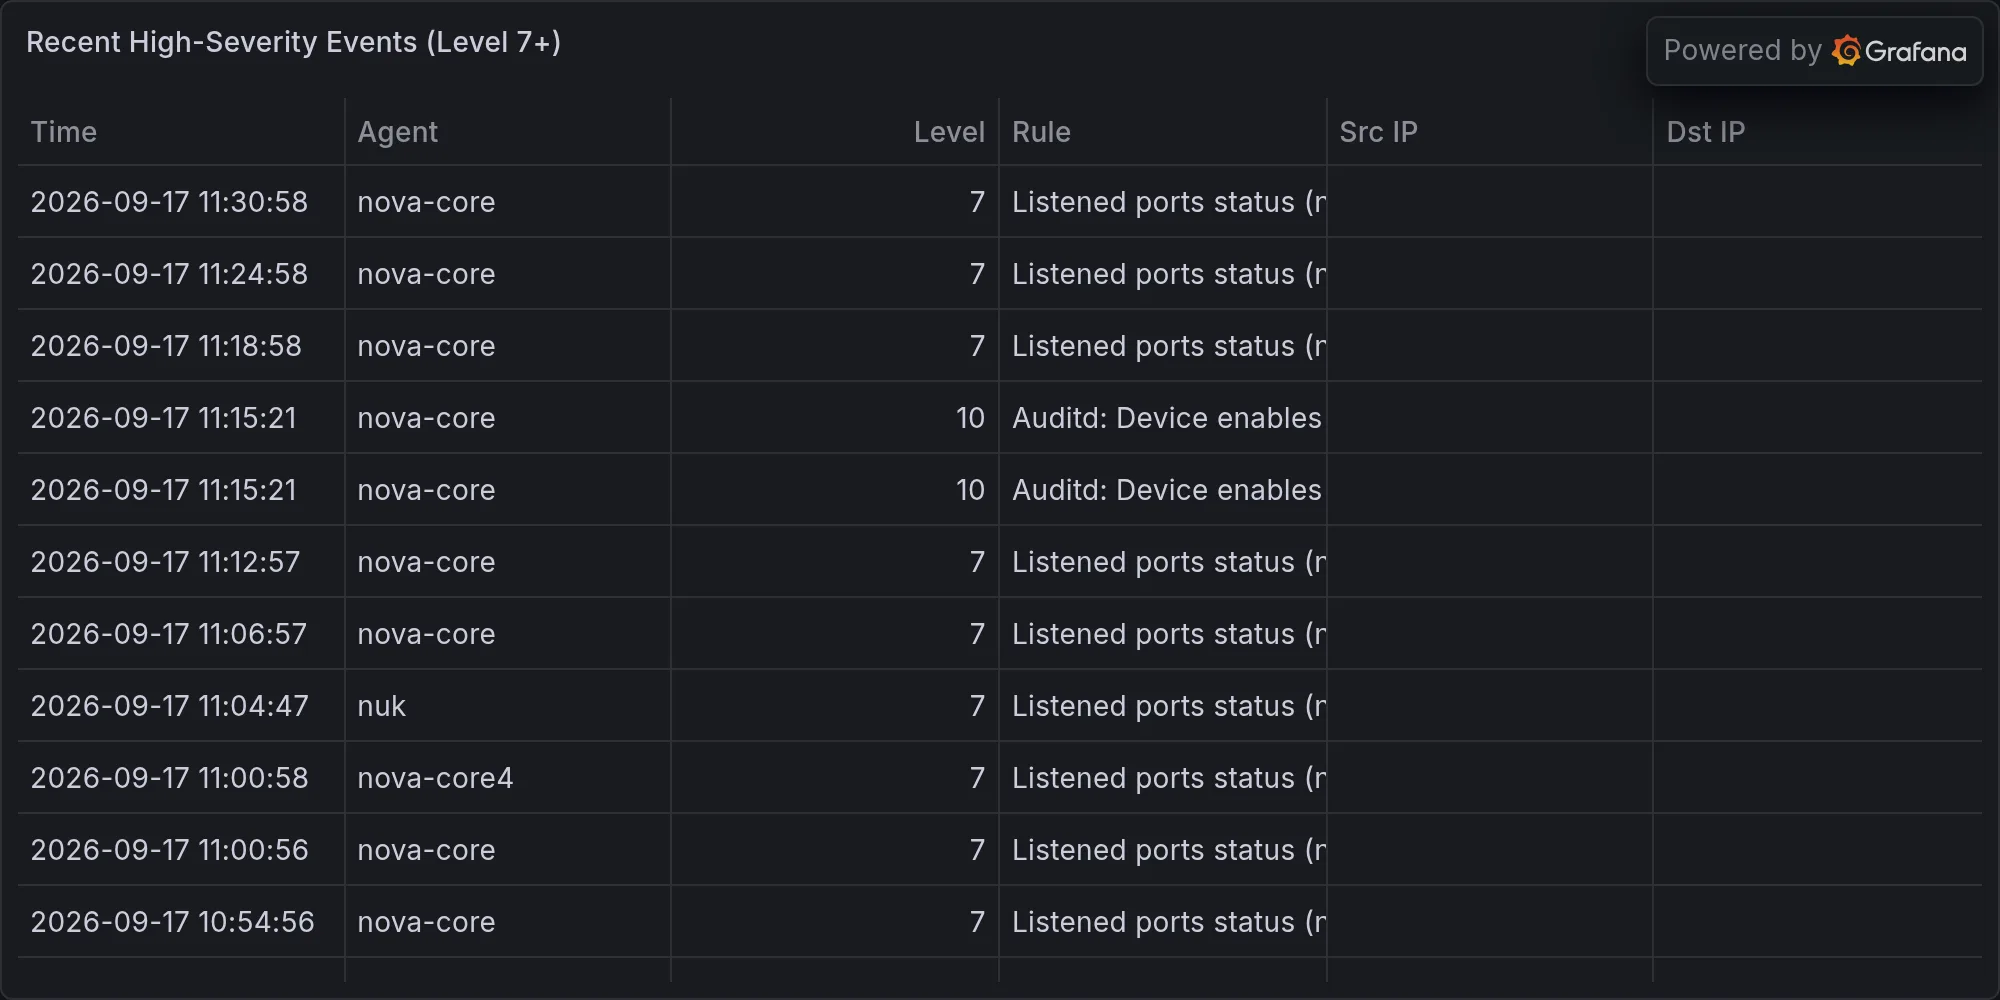
Recent high-severity events at publish time: