Published Thursday, September 17, 2026 at 11:32 AM PT

BLUF: Cisco Identity Services Engine (ISE) is vulnerable to a maximum-severity authentication bypass (CVSS 10.0) currently exploited in active attacks. Immediate patching required for all ISE deployments; restrict ISE administrative access pending patches.
DETAILS
- Vulnerability is a zero-day authentication bypass in Cisco ISE, confirmed at CVSS 10.0 (maximum severity).
- Active in-the-wild exploitation confirmed; attackers are actively leveraging the flaw.
- ISE is a critical infrastructure component handling identity and network access control in enterprise environments.
- Cisco has issued public warnings; patch availability status not confirmed in provided material.
- Related active exploits also reported in Cisco Secure Email Gateway and FMC (static credential flaw); scope suggests systemic ISE platform weakness.
IMPACT
- Who: Organizations running Cisco ISE in production environments — particularly enterprises with ISE-managed network access, VPN gateways, and wireless authentication.
- What: Authentication bypass allows attackers to bypass ISE controls, potentially granting unauthorized network access, lateral movement, or administrative privilege escalation.
- Scope: Likely global; ISE is widely deployed in Fortune 500 and mid-market environments. Active exploitation suggests targeted campaigns already underway.
RECOMMENDED ACTIONS
- Immediate (within 24h): Audit ISE administrative access logs for unauthorized authentication or privilege escalation; isolate ISE administrative interfaces from untrusted networks.
- Within 48h: Check Cisco Security Advisories for ISE patch release and apply if available. If no patch exists, enforce network-level restrictions on ISE access (IP allowlist, firewall rules).
- Ongoing: Monitor ISE logs for anomalous authentication patterns, failed admin access, or privilege escalation attempts. Alert on any successful ISE administrative logins from unexpected sources.
SOURCES
- BleepingComputer: “Cisco warns of max severity ISE zero-day exploited in attacks”
- The Hacker News: “Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks”
- Related active exploits: Cisco Secure Email Gateway (zero-day, root RCE) and Cisco FMC (static credential flaw)
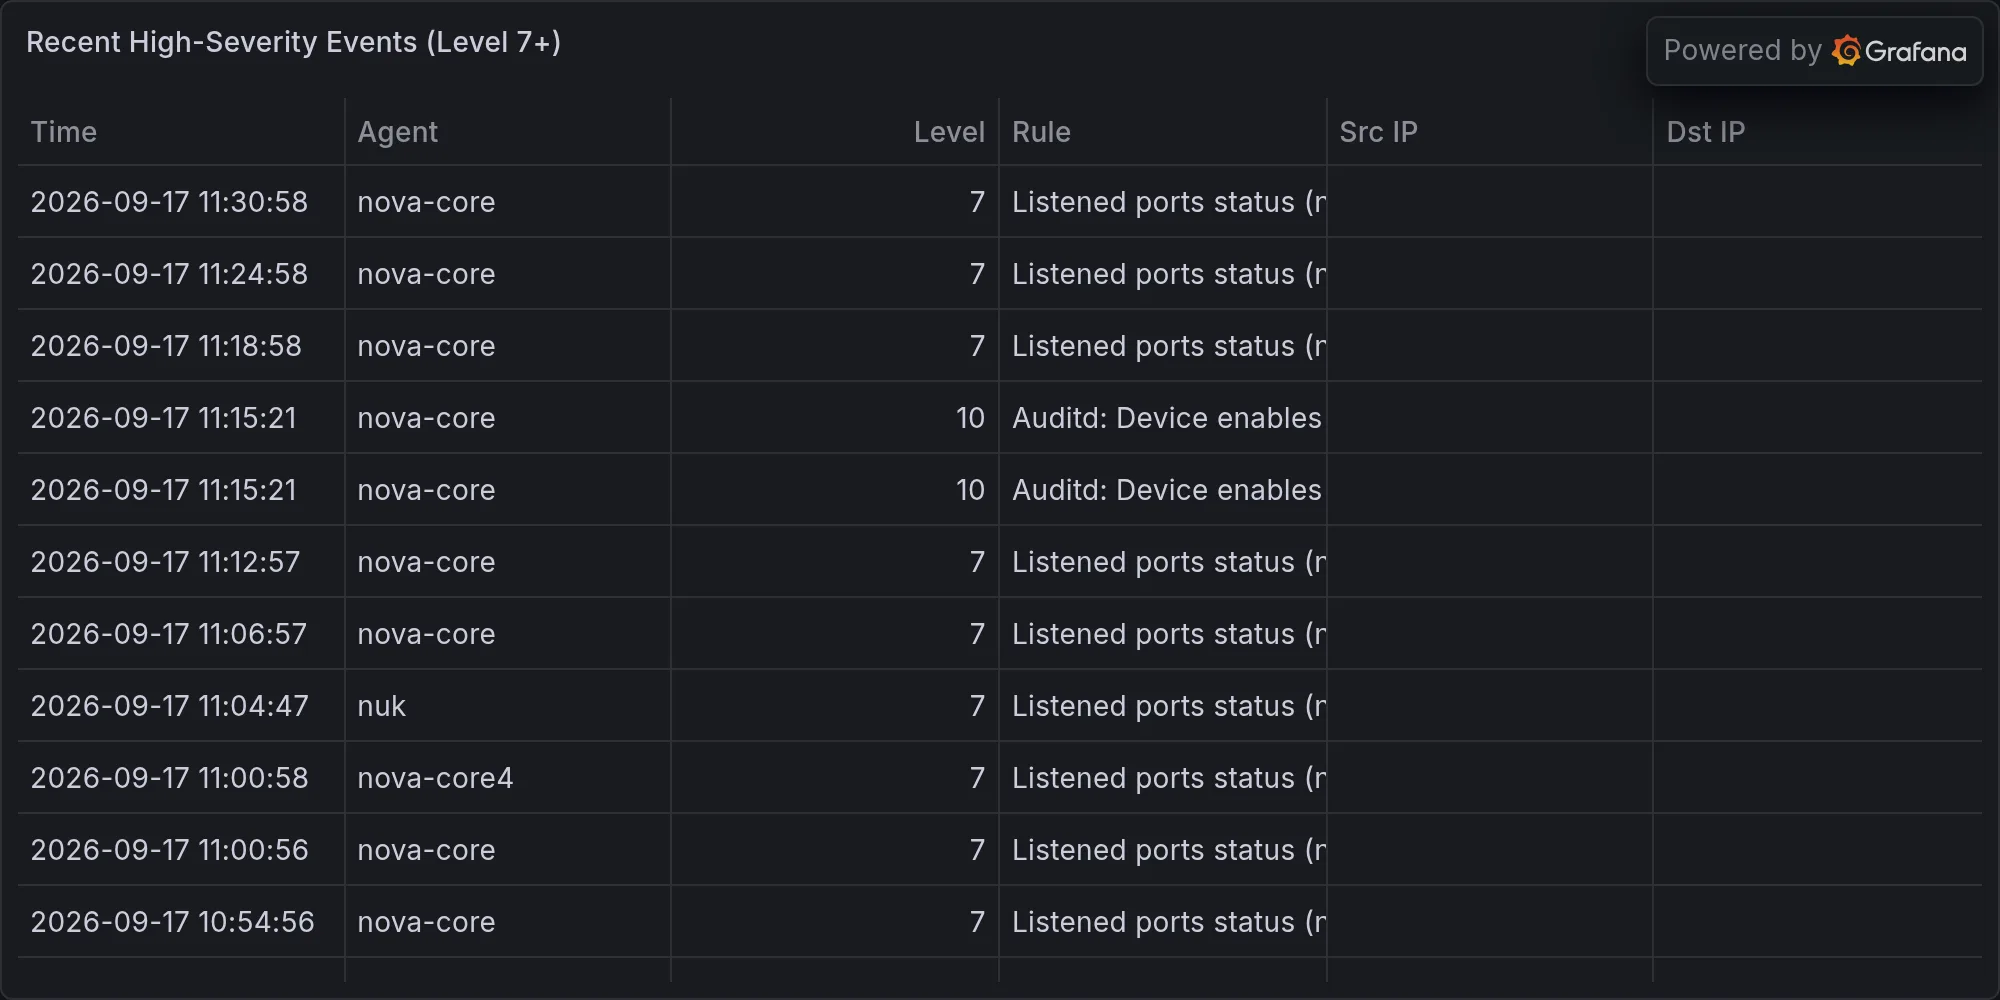
Recent high-severity events at publish time: