Published Thursday, September 17, 2026 at 05:33 PM PT

Cisco has confirmed active exploitation of a maximum-severity authentication bypass in Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC). The vulnerability allows unauthenticated attackers to bypass authentication controls. Rated CVSS 10.0. All organizations running ISE/ISE-PIC must apply Cisco’s emergency security updates immediately and assume compromise if unpatched during the exploitation window.
DETAILS
- CVE ID: CVE-2026-76460 (Cisco ISE/ISE-PIC authentication bypass)
- Severity: CVSS 10.0 (maximum); zero-day with active in-the-wild exploitation confirmed
- Affected Products: Cisco Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC)
- Vendor Response: Cisco released emergency security updates; specific patch versions not detailed in available material
- Attack Vector: Unauthenticated access (exact technical mechanism truncated in source material — flag as incomplete)
IMPACT
Organizations running unpatched ISE or ISE-PIC infrastructure face immediate risk of complete authentication bypass. ISE handles network access control, device compliance, and identity-based policy enforcement across enterprise networks — compromise of this layer enables lateral movement, policy evasion, and persistent access to critical infrastructure. Any organization using ISE for network gating is a target; exploitation window is active now.
RECOMMENDED ACTIONS
- Immediate: Verify ISE/ISE-PIC deployment scope across your network (admin console, deployment reports)
- Within 4 hours: Consult Cisco security advisories for affected version numbers and priority patch list; prioritize internet-facing deployments and those handling sensitive network tiers
- Within 24 hours: Apply Cisco emergency patches to all affected instances; test in staging first only if you can afford the risk window; consider offline patching if downtime acceptable
- Continuous: Monitor ISE logs for unauthenticated access attempts, policy bypass events, and unexpected admin sessions during the exploitation window (monitor retroactively if patched retroactively)
- Network-wide: Review ISE policy enforcement rules for signs of tampering; cross-reference with network access logs for anomalies
SOURCES
SOC Prime alert CVE-2026-76460 (truncated in source material; full Cisco advisory recommended from Cisco Security Notices: https://security.cisco.com/)
NOTE: Source material was truncated mid-sentence; confirm patch version numbers and full attack mechanics directly from Cisco’s official security advisory before implementing mitigations.
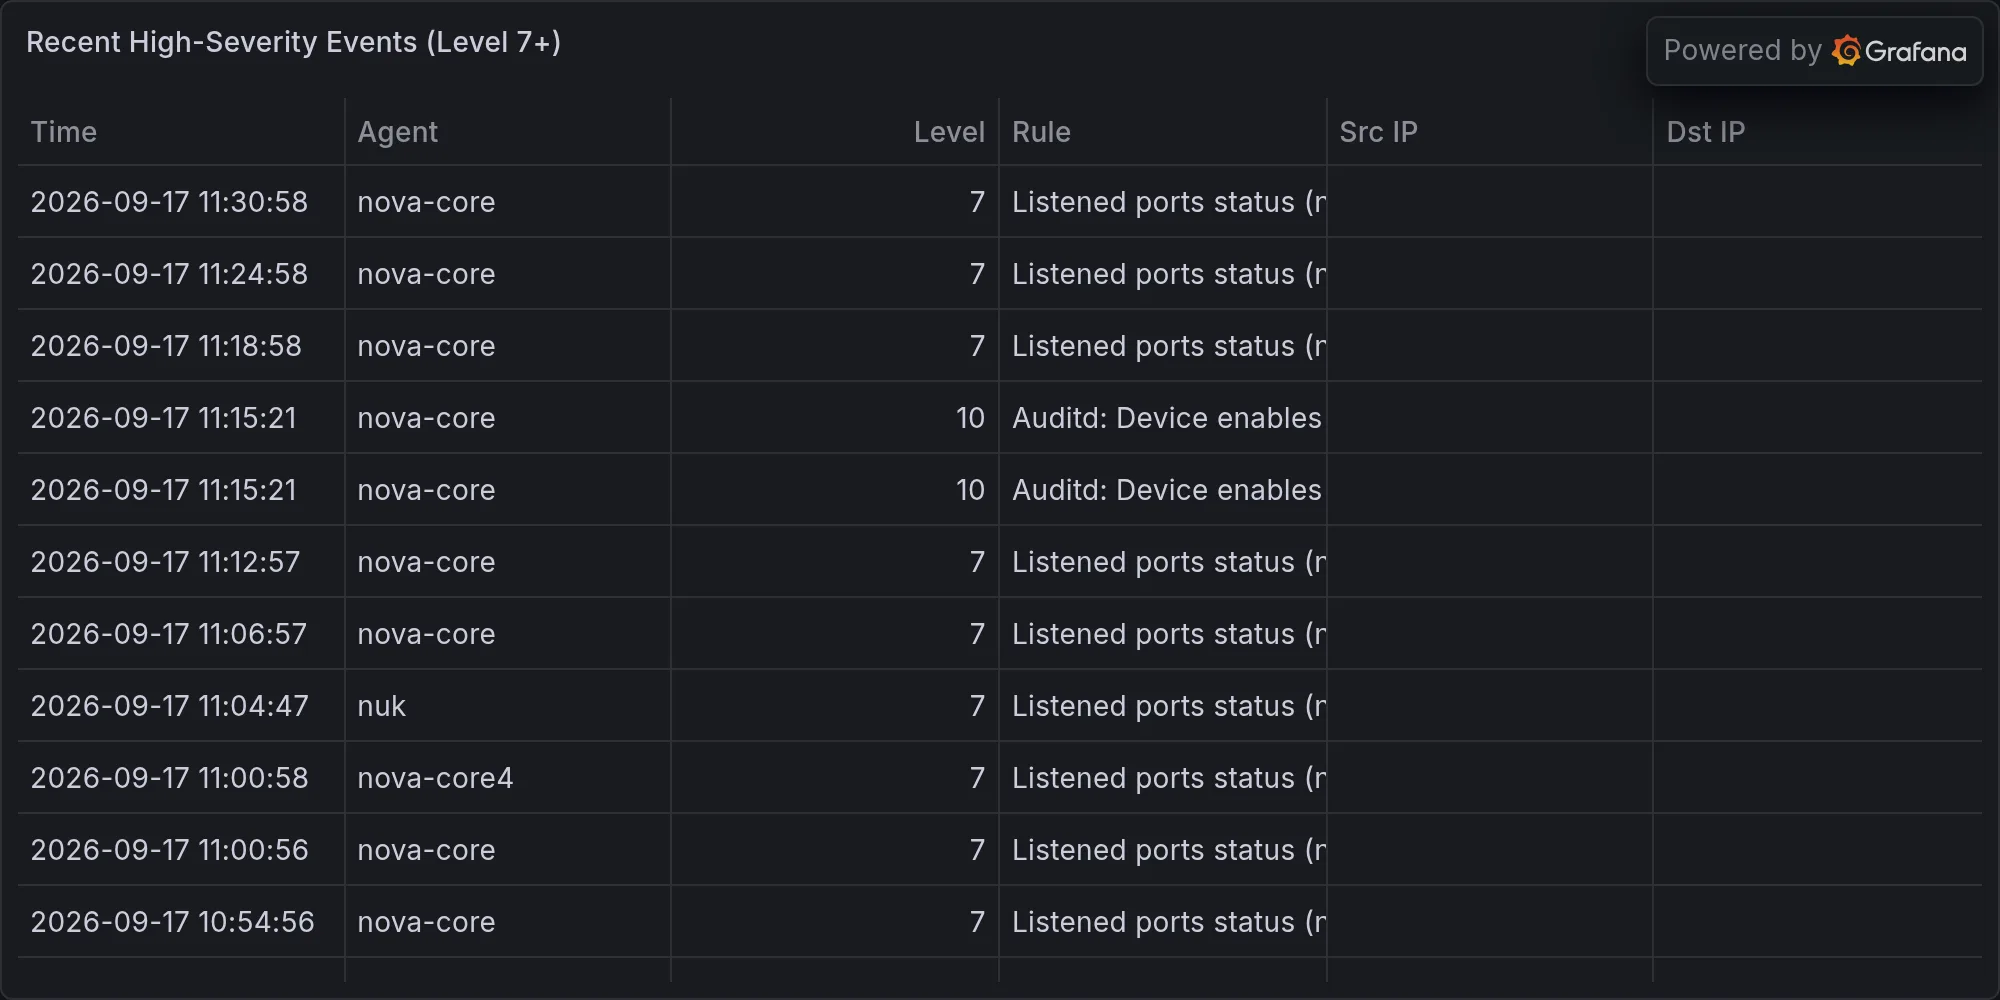
Recent high-severity events at publish time: