Published Thursday, September 17, 2026 at 11:31 AM PT

BLUF: Google has patched a high-severity zero-day (CVSS 8.0) in Pixel device cellular modems that attackers are actively exploiting in limited, targeted operations. The flaw enables permission bypass and privilege escalation. All Pixel users should apply available security updates immediately.
DETAILS:
- Vulnerability: CVE-2026-58704 affects the cellular modem component in Google Pixel devices; classified as a zero-day before patch release
- Severity & CVSS: Scored 8.0 under CVSS 3.1 (high severity); permits attackers to bypass permission checks and escalate privileges on affected handsets
- Active Exploitation: Google confirmed limited, targeted attacks leveraging this flaw—not widespread but confirmed in-the-wild activity
- Affected Asset Class: Cellular modem firmware/drivers in Pixel device line; specific model scope unconfirmed at this time
- Mitigation Availability: Google has released security updates; patch status and rollout timeline not specified in available advisories
IMPACT:
Pixel device users, particularly those in targeted sectors (government, finance, media, NGOs—profile of targets unconfirmed), face remote code execution and privilege escalation risks if unpatched. Compromise of the modem layer can provide persistent access and deep system control independent of OS-level defenses. Enterprise deployments with Pixel fleets are at elevated risk during patch lag.
RECOMMENDED ACTIONS:
- Immediate: Check Settings > System > System Update on all deployed Pixel devices; apply any available security patches without delay
- Inventory: Identify all Pixel devices in fleet; prioritize high-value/sensitive-access devices (executives, engineers, security teams) for expedited patching
- Monitor: Watch for suspicious network activity, unusual battery drain, or unexpected modem resets (potential indicators of exploitation)
- Escalation: If any device cannot patch immediately (e.g., EOL/unsupported models), restrict network access or consider device replacement
- Intel: Monitor Google Security & Privacy Blog and Android Security & Privacy Year in Review for full advisory; specific affected Pixel models and patch rollout timeline to be clarified as advisories mature
SOURCES:
SOC Prime threat intelligence feed (CVE-2026-58704 advisory). Specific attack indicators, threat actor attribution, and detailed CVSS vector rationale not yet available; this alert captures confirmed facts only.
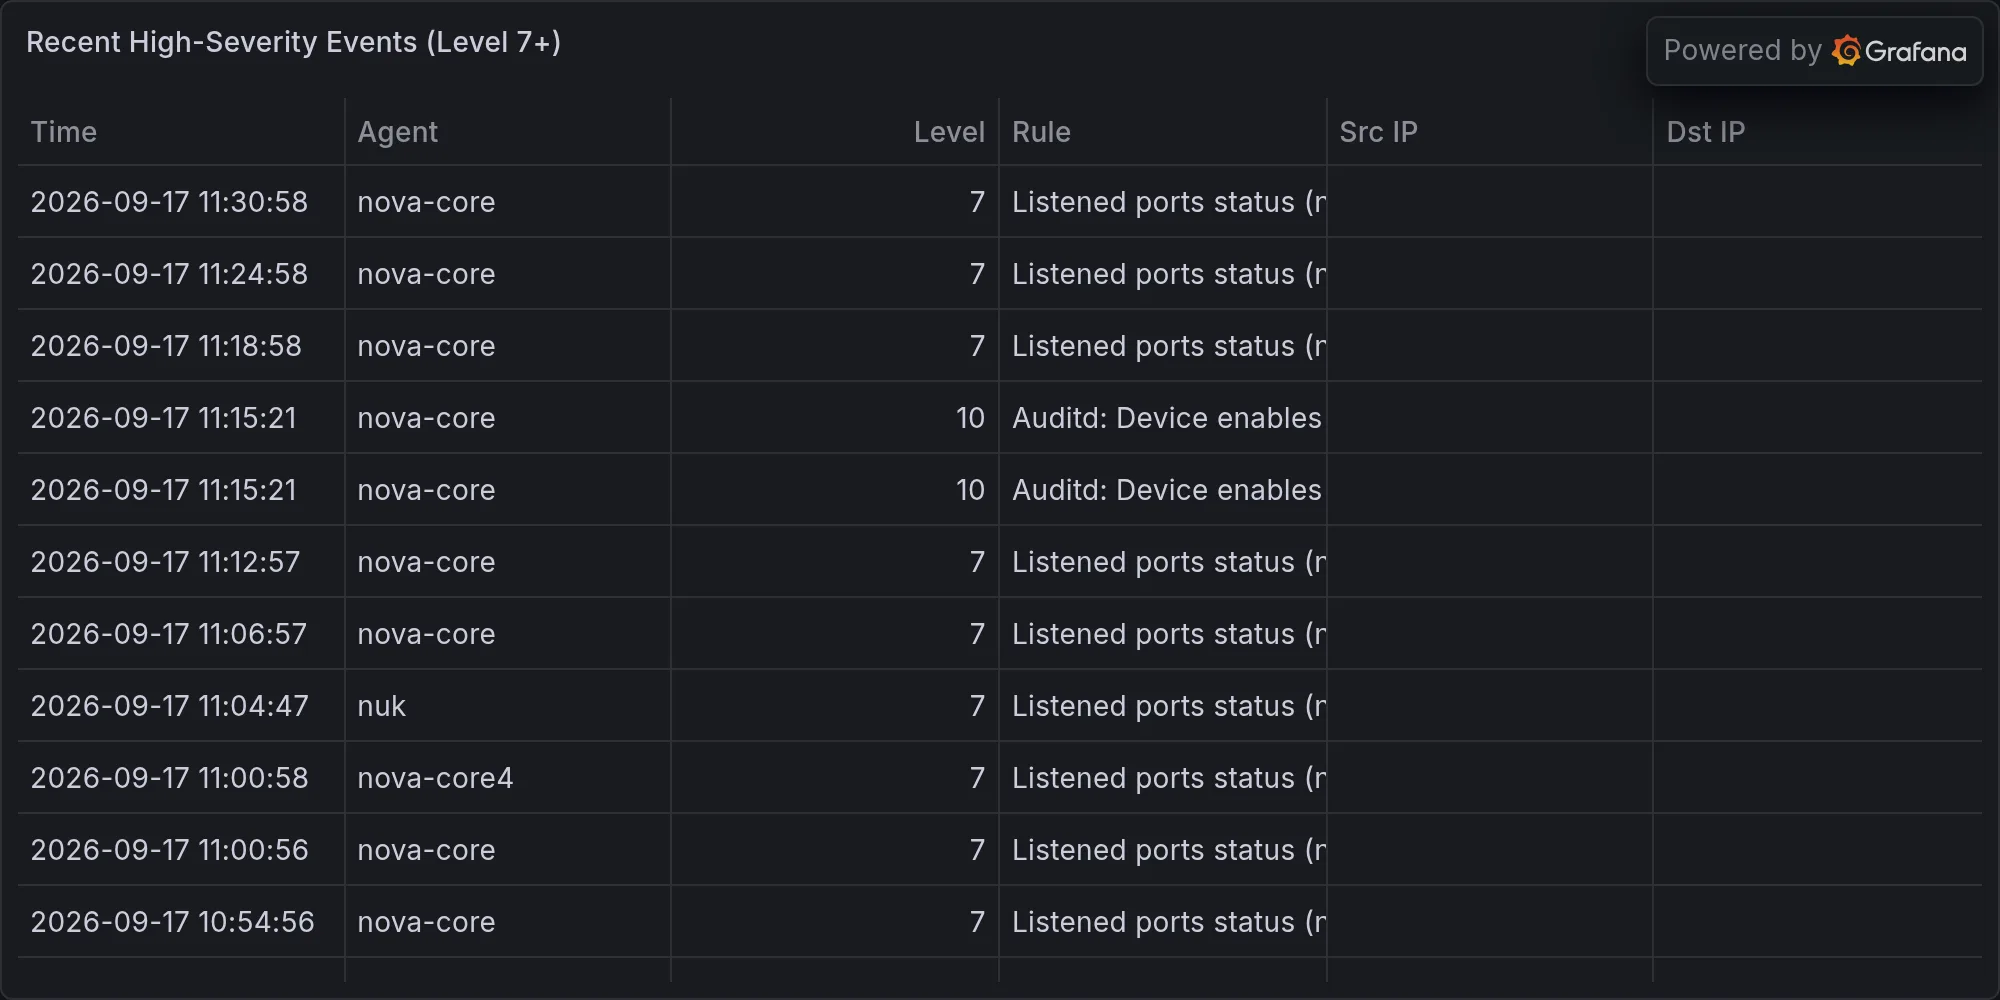
Recent high-severity events at publish time: