Published Friday, September 18, 2026 at 10:00 AM PT

BLUF: Apple has released iOS 26.7 and iPadOS 26.7. CVE inventory and impact are available at https://support.apple.com/en-us/100100. Scope and severity details unconfirmed pending formal review of Apple’s security advisory.
DETAILS
- iOS 26.7 and iPadOS 26.7 released as of 18 September 2026
- Apple’s standard practice (per recent releases) patches dozens to hundreds of vulnerabilities across frameworks, WebKit, and system services
- CVE list, affected iOS versions, and remediation guidance published at Apple support document 100100
- Distribution began automatically via OTA; no forced deployment window announced
- Historical context: iOS 26.x releases have consistently patched 25–87+ vulnerabilities per cycle; iOS 27 (separate release) patches ~200 across iOS, macOS
IMPACT
- Who: All iOS 26.7 and iPadOS 26.7 users (iPhones, iPads on 26.x branch)
- What: Unconfirmed — likely includes memory corruption, kernel, browser, and media handling fixes typical of Apple’s security cadence
- Scope: Unknown until CVE advisory is parsed; historically medium-to-high severity patches in most releases
RECOMMENDED ACTIONS
- Immediate: Review https://support.apple.com/en-us/100100 for CVE list, severity ratings, and affected device models
- For managed fleets: Check if 26.7 adoption is monitored; plan rollout if high-severity WebKit or kernel issues surface in advisory
- No hold: Apple’s track record does not justify delaying adoption pending full analysis
SOURCES
- Apple Security Updates (official) — https://support.apple.com/en-us/100100
- Nova memory: Apple security update patterns, prior 26.x & 27.x releases
Status: UNCONFIRMED details pending advisory parse. Will escalate to CRITICAL or HIGH if WebKit RCE, kernel elevation, or similar high-impact CVEs confirmed.
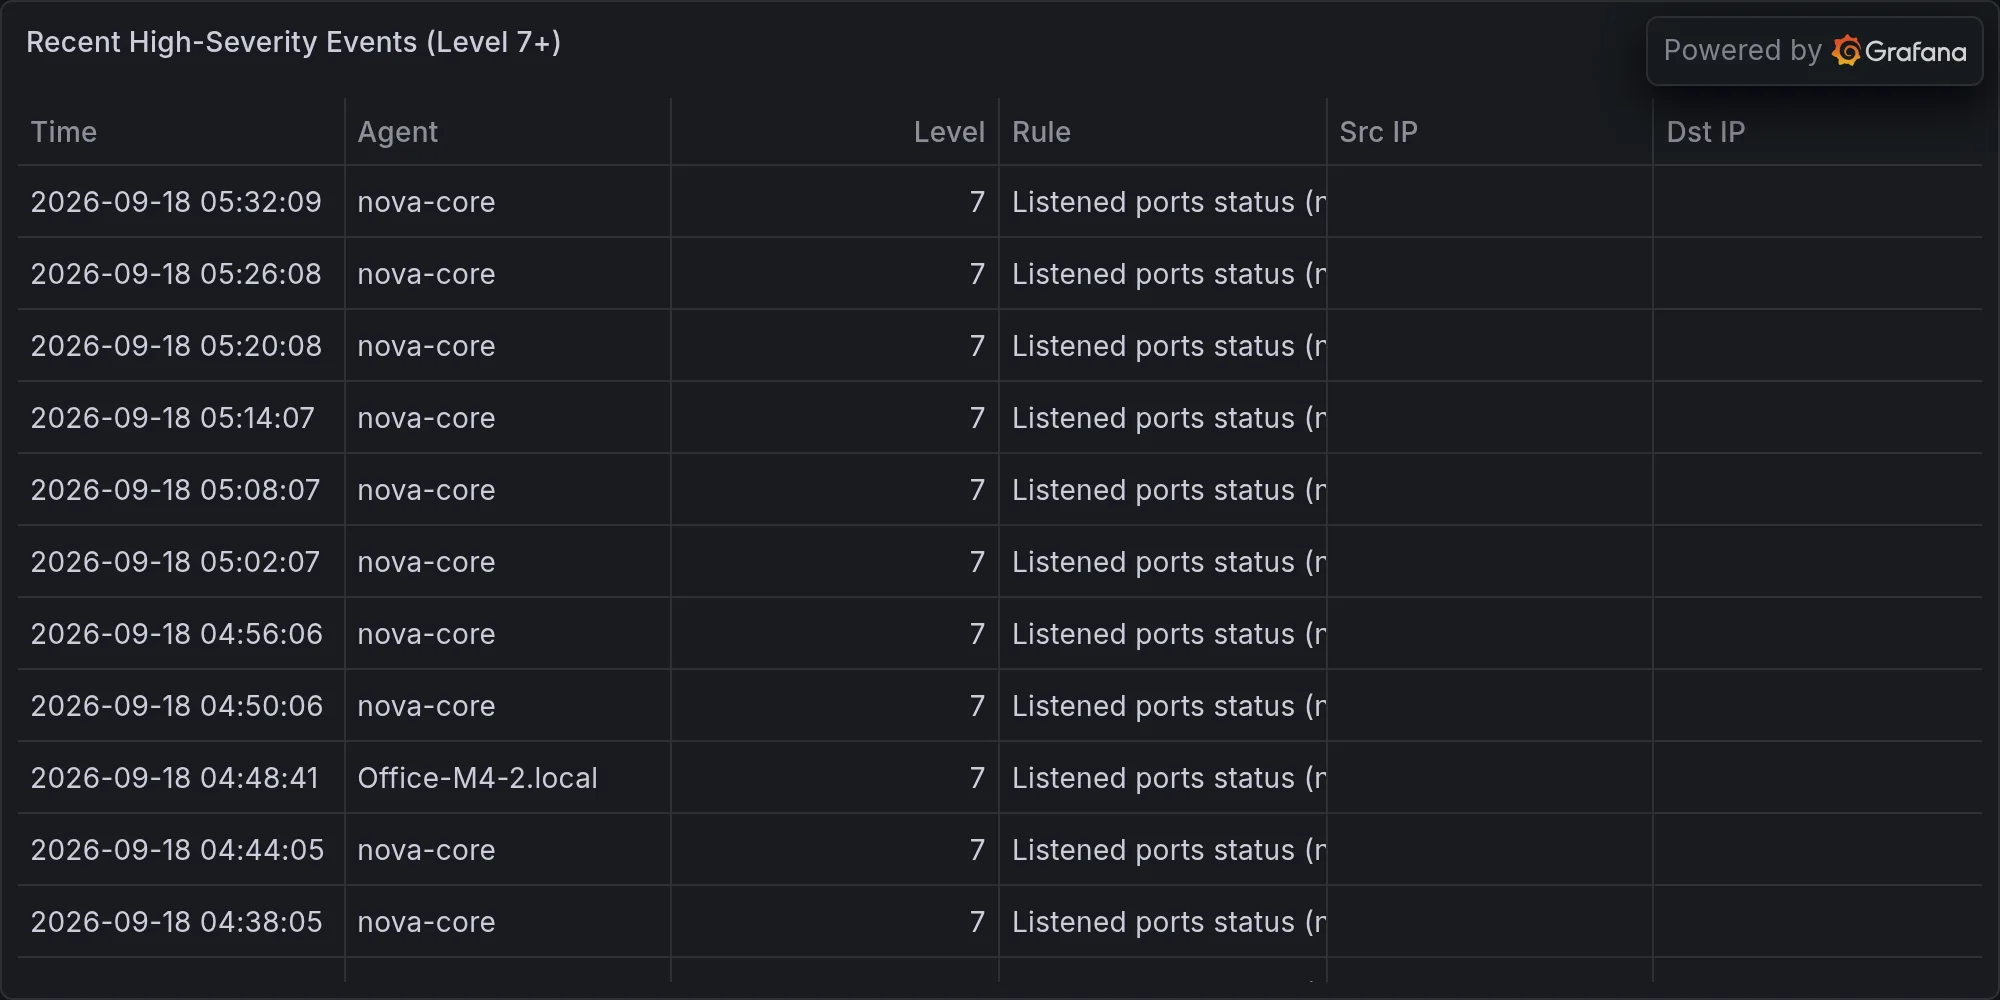
Recent high-severity events at publish time: