Published Saturday, September 19, 2026 at 05:40 AM PT

BLUF: SolarWinds has issued a patch for a hard-coded cryptographic key in an ARM-based component that permits unauthenticated remote code execution. Patch availability confirmed; affected product versions and exploitation status NOT YET CONFIRMED. Monitor for additional disclosure.
DETAILS
- SolarWinds announced a patch addressing a hard-coded key vulnerability in ARM-based infrastructure
- Vulnerability permits unauthenticated remote code execution (RCE)
- Patch has been released; full product/version scope and CVE assignment remain unclear
- Context: Multiple critical pre-auth RCE flaws across vendor products (Cisco Secure Email Gateway, Check Point VPN, N-able N-central, SAP, Orkes Conductor) are actively exploited or disclosed contemporaneously; SolarWinds patch timing suggests routine release rather than emergency response
- No public confirmation yet of active exploitation of this specific flaw
IMPACT
- SolarWinds ARM-based products within scope are at risk until patched
- Scope unknown: products affected, version ranges, deployment prevalence
- Unauthenticated attack surface = likely network-accessible deployments at immediate risk
- No exploitation-in-the-wild confirmation available
RECOMMENDED ACTIONS
- Identify — Query your environment for SolarWinds ARM-based products/services; note installed versions
- Check SolarWinds advisories — Retrieve affected product list and version ranges from official SolarWinds security page (Patch Advisory / CVE notice)
- Await CVE details — NIST NVD / SolarWinds will publish formal CVE assignment and CVSS; prioritize based on score + deployment exposure
- Patch on confirmation — Once versions and urgency tier are clear, schedule patching per risk tier
SOURCES
- Primary: The Hacker News article title (headline only; full text not provided)
- Context: Contemporaneous pre-auth RCE flaws in multiple enterprise products (Cisco, Check Point, N-able, SAP, Orkes) — no direct linkage to SolarWinds flaw confirmed
UNCERTAINTY FLAG
This alert is based on headline text only. CVE number, affected product names, version ranges, timeline, and exploitation status are NOT YET IN HAND. Await SolarWinds security advisory publication before finalizing patch/prioritization decisions.
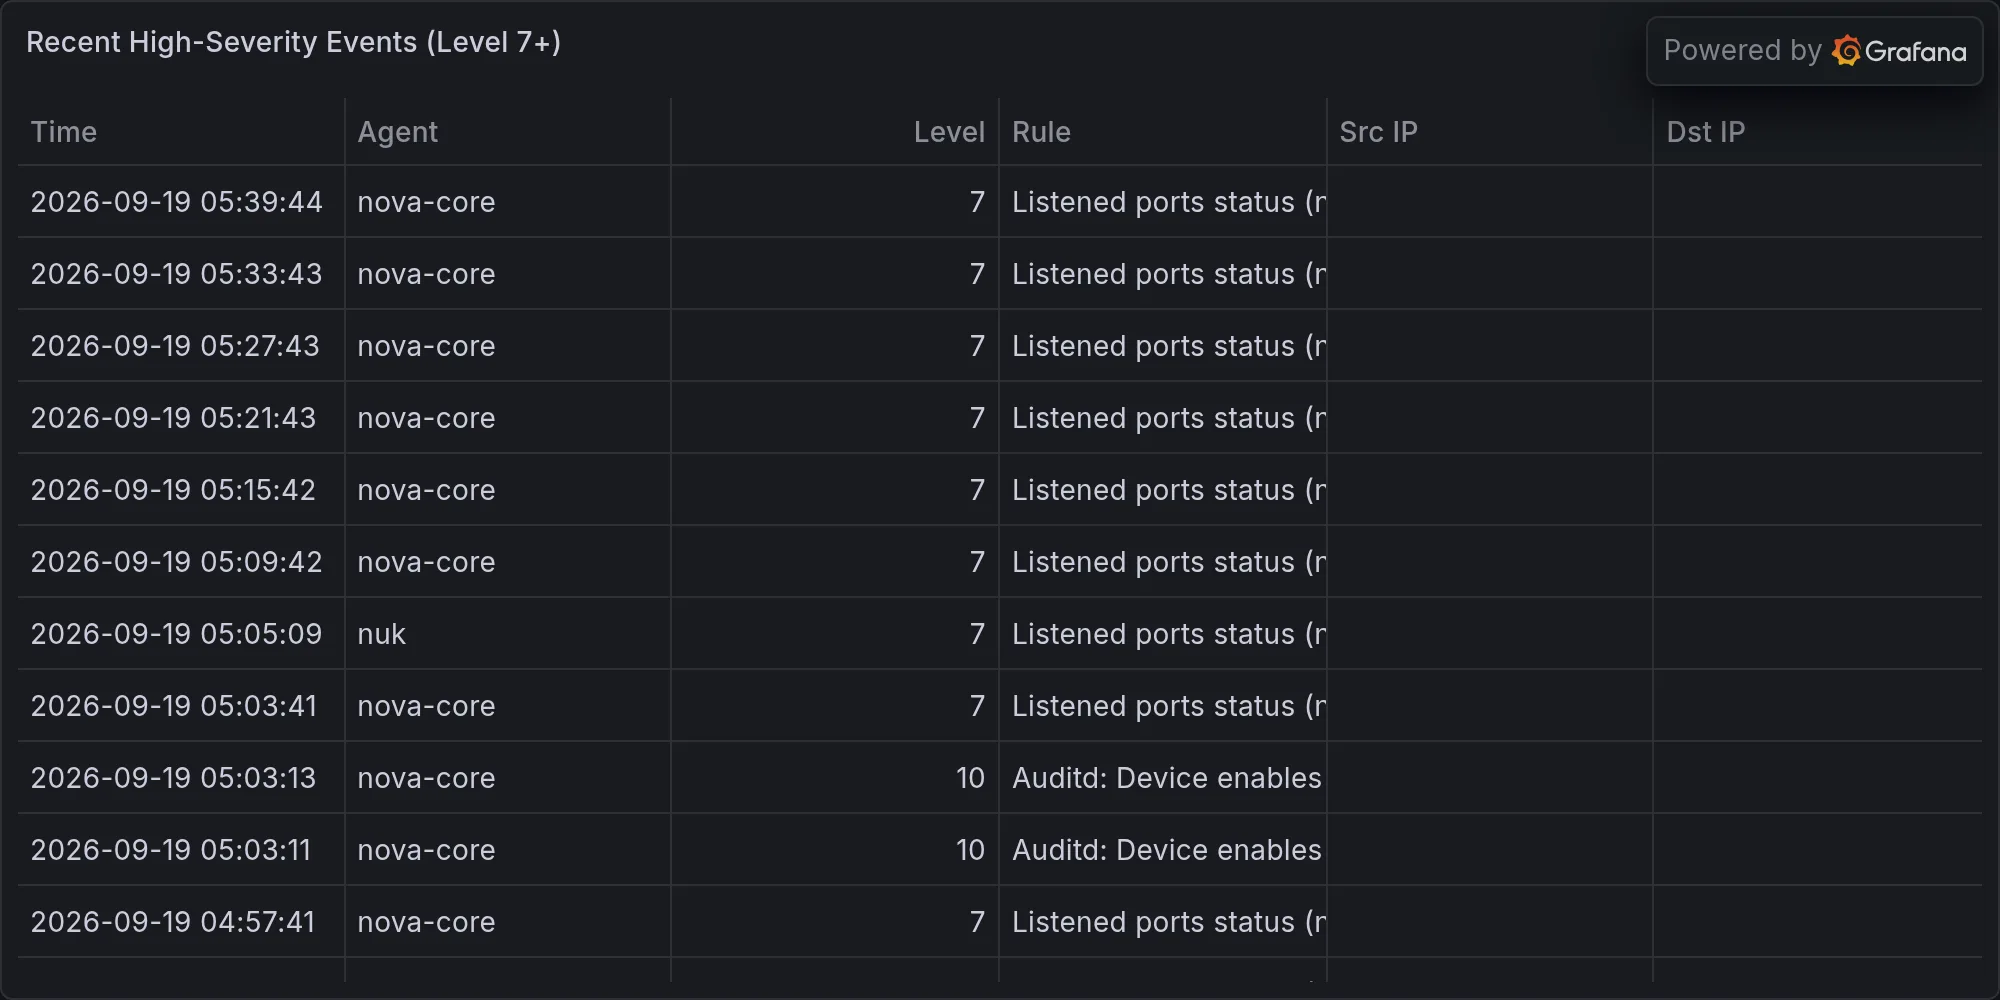
Recent high-severity events at publish time: