Published Sunday, September 20, 2026 at 01:20 PM PT

An internal host is actively conducting a multi-port network scan against another internal system. IPS on nova-core detected 192.168.1.9 initiating connections to 5 distinct ports on 192.168.1.138 within a 60-second window. Lateral movement of this pattern—multiple ports, rapid succession, internal source—is consistent with post-compromise reconnaissance or exploitation attempts. Immediate investigation required to determine whether the source host is compromised.
DETAILS
- Detection: IPS signature on nova-core flagged as
lateral_movementtype, confirmed action status “detected” - Source: 192.168.1.9 (internal IP); target: 192.168.1.138 (internal IP)
- Pattern: 5 port connections within 60 seconds; consistent with port enumeration or vulnerability scanning
- Timing: Real-time detection; no indication this is historical data
- Scope: Internal network only; no external IP involvement in the detected traffic
IMPACT
- Affected systems: Minimally 192.168.1.138; 192.168.1.9 is the active source and may itself be compromised
- Risk level: High — lateral movement combined with multi-port scanning suggests active reconnaissance for exploitation
- Organizational exposure: If 192.168.1.9 is compromised, attacker has foothold within internal network and is actively probing for additional targets or escalation paths
RECOMMENDED ACTIONS
- Isolate source immediately: Confirm whether 192.168.1.9 is an authorized system. If yes, determine who has access and what activity justifies multi-port scanning. If no, isolate from network pending forensics.
- Identify target system: Confirm purpose of 192.168.1.138—what services run on the 5 ports targeted? Verify those ports should be accessible from 192.168.1.9.
- Collect logs: Pull IPS/firewall logs for both IPs over the past 24 hours; check for earlier scanning activity or successful connections.
- Check source for compromise: If 192.168.1.9 is a workstation or server, scan for malware, review process execution logs, and audit user/service activity for that timestamp.
- Segment if possible: Block 192.168.1.9 ↔ 192.168.1.138 traffic until source is cleared.
SOURCES
IPS detection: nova-core lateral_movement signature. Context: CVEs noted in memory suggest prior exploitation interest in lateral movement vectors (CVE-2022-40684, CVE-2023-22515, CVE-2026-29000, CVE-2026-43499); current detection aligns with typical post-compromise behavior.
STATUS: Ongoing. No confirmation yet whether source is compromised or authorized. Treat as active incident until cleared by investigation.
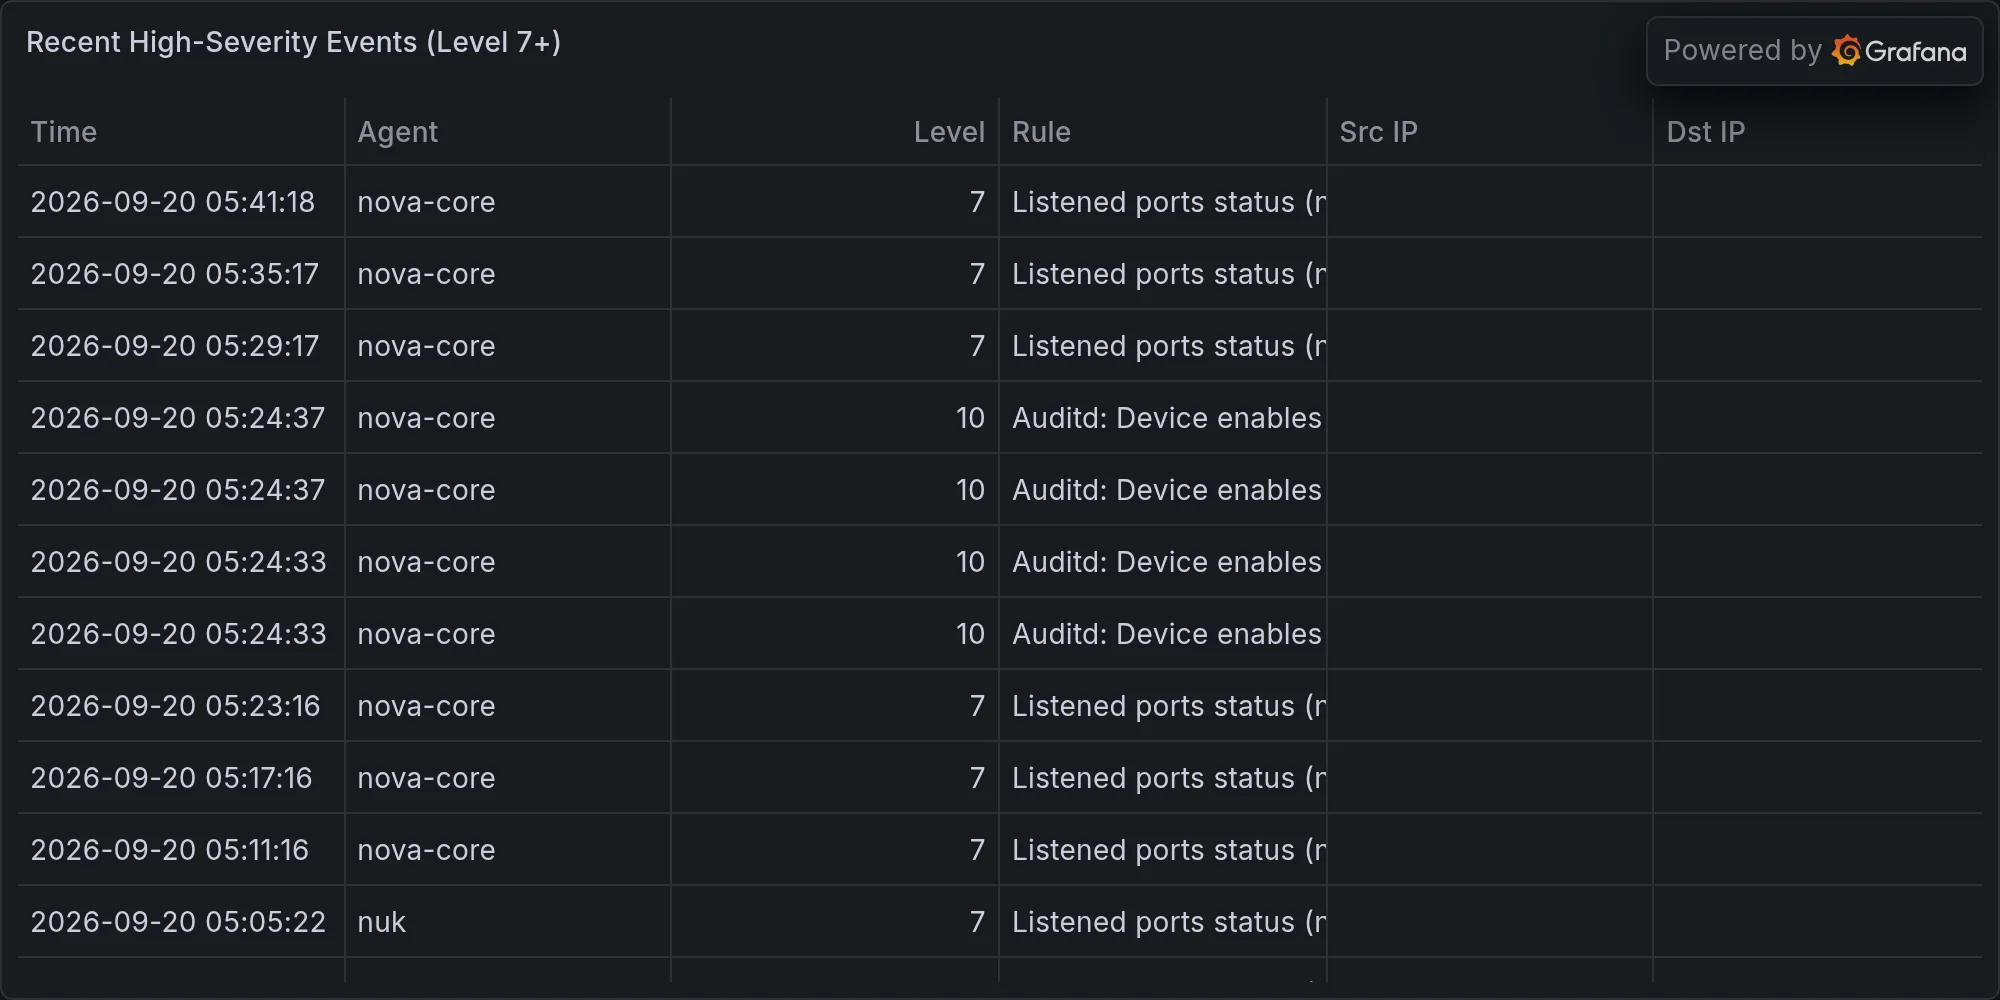
Recent high-severity events at publish time: