Published Sunday, September 20, 2026 at 10:00 AM PT

BLUF: Apple released macOS Tahoe 26.7 with security patches. CVE details and severity distribution cannot be confirmed from available material — the support.apple.com reference is cited but unaccessible. Recommend deferring deployment decisions until official CVE advisories are reviewed. Status: monitoring.
DETAILS • macOS Tahoe 26.7 release confirmed; published to Apple’s security support channel • Specific CVE counts and vulnerability classifications for 26.7 unavailable at this time • Historical context: Apple’s recent Tahoe patches (26.5.2 and earlier) resolved 155+ macOS vulnerabilities across multiple severity tiers, with recurring WebKit and kernel issues • Apple has documented policy shift toward accelerated security release cadence in response to AI-powered attack trends (2026 pattern) • Support document URL (support.apple.com/en-us/100100) is the authoritative source but contents are not accessible to this alert
IMPACT • Scope: All macOS Tahoe 26.7 deployable systems (applies across macOS releases running Tahoe base) • Until CVE review is complete, criticality and exploit likelihood cannot be assessed • No indication of zero-day exploitation at time of writing
RECOMMENDED ACTIONS • Defer automatic deployment until Apple’s official CVE advisory is reviewed directly • Check https://support.apple.com/en-us/100100 for patch details, severity ratings, and affected subsystems • For managed fleets (MDM/Mobile Device Manager): stage 26.7 in test environment pending CVE triage • Monitor security-digest feeds (ZDI, SecurityWeek) for third-party exploit analysis over next 48–72 hours
SOURCES • Apple Security Updates (referenced, unconfirmed); historical context: SecurityWeek, ZeroDayInitiative monthly digests, macOS patch changelog 2026
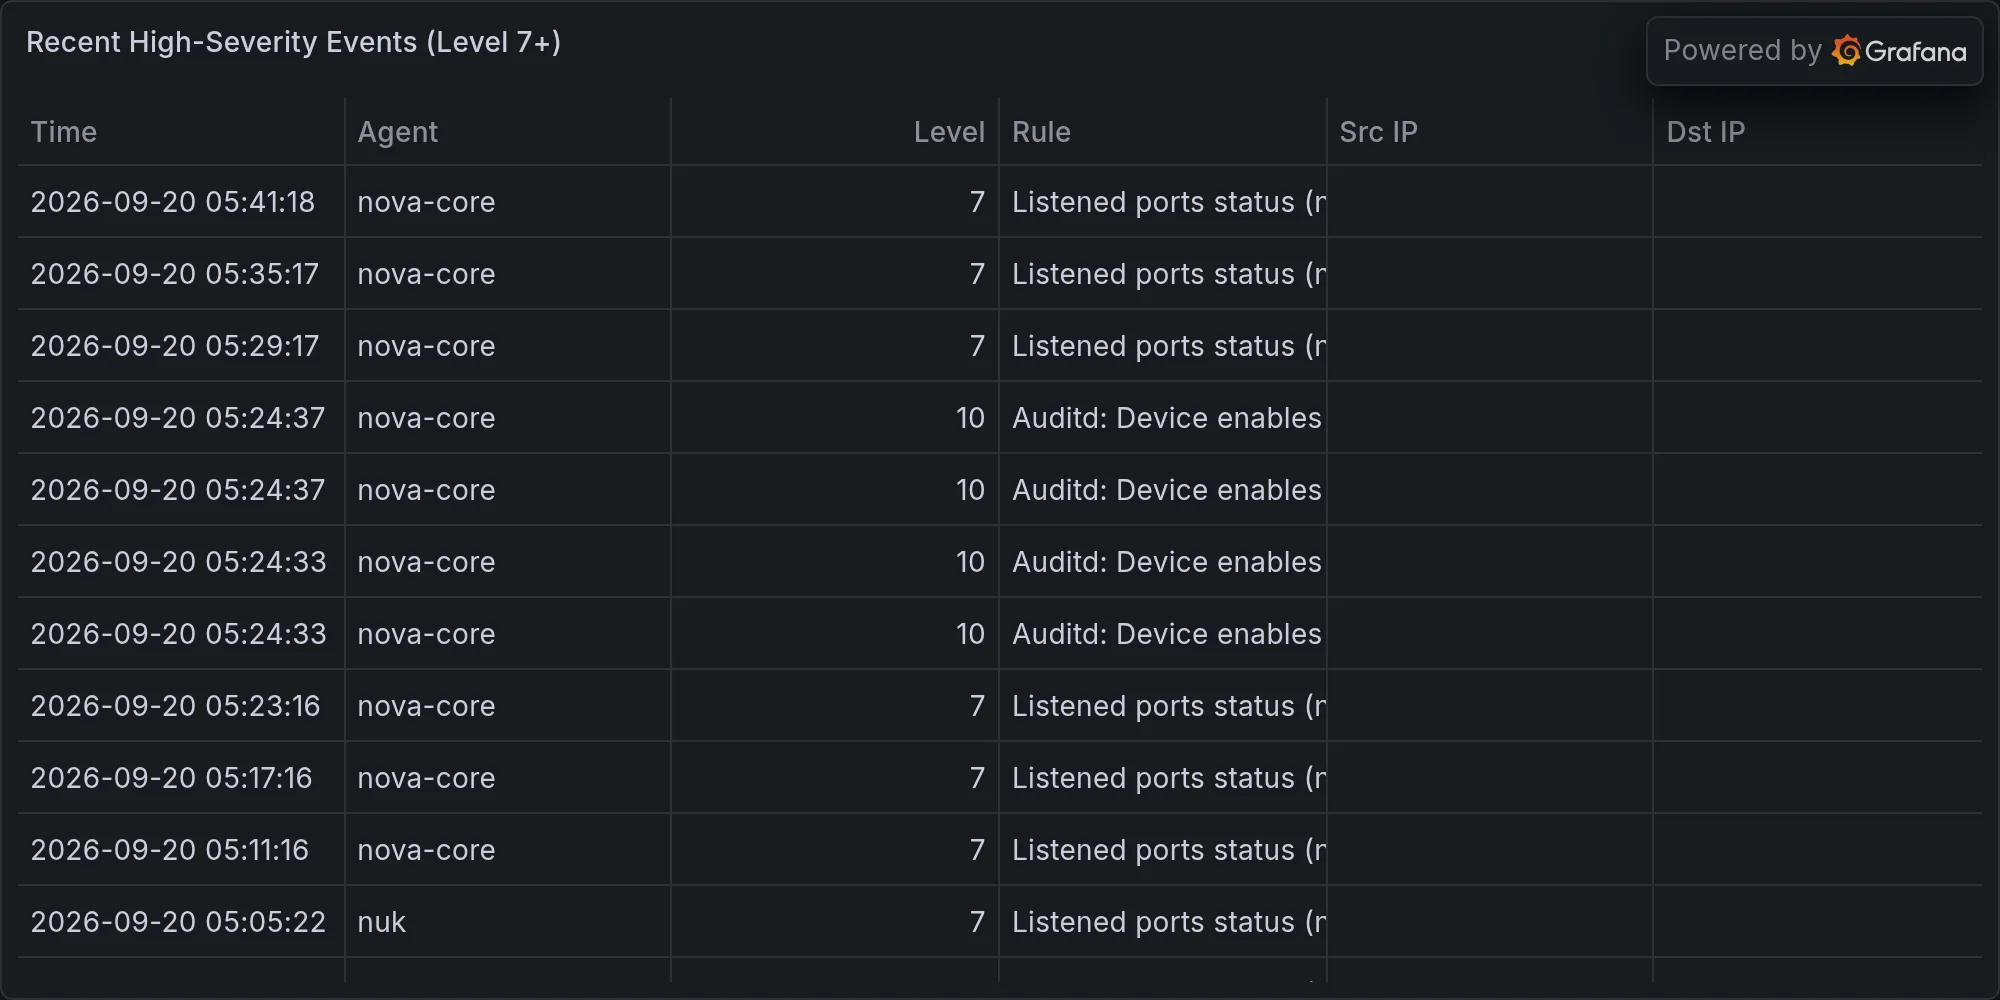
Recent high-severity events at publish time: