Published Monday, September 21, 2026 at 11:46 AM PT

BLUF: Hacker News reporting Cisco 0-day vulnerability, AI agent remote code execution exploits, ClickFix attack surge, and browser hijacking campaigns active this week. Full CVE details, affected versions, and attack scope not yet confirmed from provided source titles alone. Recommend defensive posture pending vendor advisories.
DETAILS:
- Cisco 0-day: Multiple sources flagging active Cisco zero-day; vendor advisory status and CVSS rating unconfirmed from available material.
- AI Agent RCE: Emerging exploit class targeting AI/LLM agent deployments with remote code execution capability; specific vector unknown.
- ClickFix surge: Active campaign exploiting ClickFix technique (click-based social engineering or browser automation hijack); volume and targeting scope unconfirmed.
- Browser hijacks: Concurrent browser hijacking attacks reported; mechanism (DNS, proxy, extension, certificate) and scope unconfirmed.
- Timing: Activity window is this week (week of 2026-09-21); ongoing or contained status unknown.
IMPACT:
Cisco infrastructure operators, AI service providers, and end-user browser security potentially at risk. Attack surface spans network appliances (Cisco), cloud/edge AI workloads, and client systems. Scope (public internet vs. targeted) and active exploitation volume unknown.
RECOMMENDED ACTIONS:
- Monitor vendor advisories — Watch Cisco, browser vendors (Chrome, Edge, Firefox), and AI platform (OpenAI, Anthropic, etc.) security bulletins for CVE details and patches this week.
- Isolate Cisco devices — If running Cisco infrastructure in untrusted network segments, restrict ingress and egress until 0-day details published; apply patches immediately upon release.
- AI deployment audit — For deployments hosting AI agents or LLM services, review authentication, API token scope, and sandboxing controls; log anomalous code execution.
- Browser hygiene — User education on phishing and suspicious click prompts; push endpoint detection tools to flag ClickFix-pattern activity.
- Await clarification — Full technical details required before specific mitigation; check CISA, vendor security pages, and Shodan for confirmed CVE IDs by EOD.
SOURCES:
The Hacker News weekly recap (2026-09-21 aggregate) — headline-level detail only; full CVE advisories and PoC status not yet available in provided material. Details flagged as unconfirmed pending vendor publication.
Status: DEVELOPING. Update when Cisco advisory, CVE IDs, or detailed exploit analysis published.
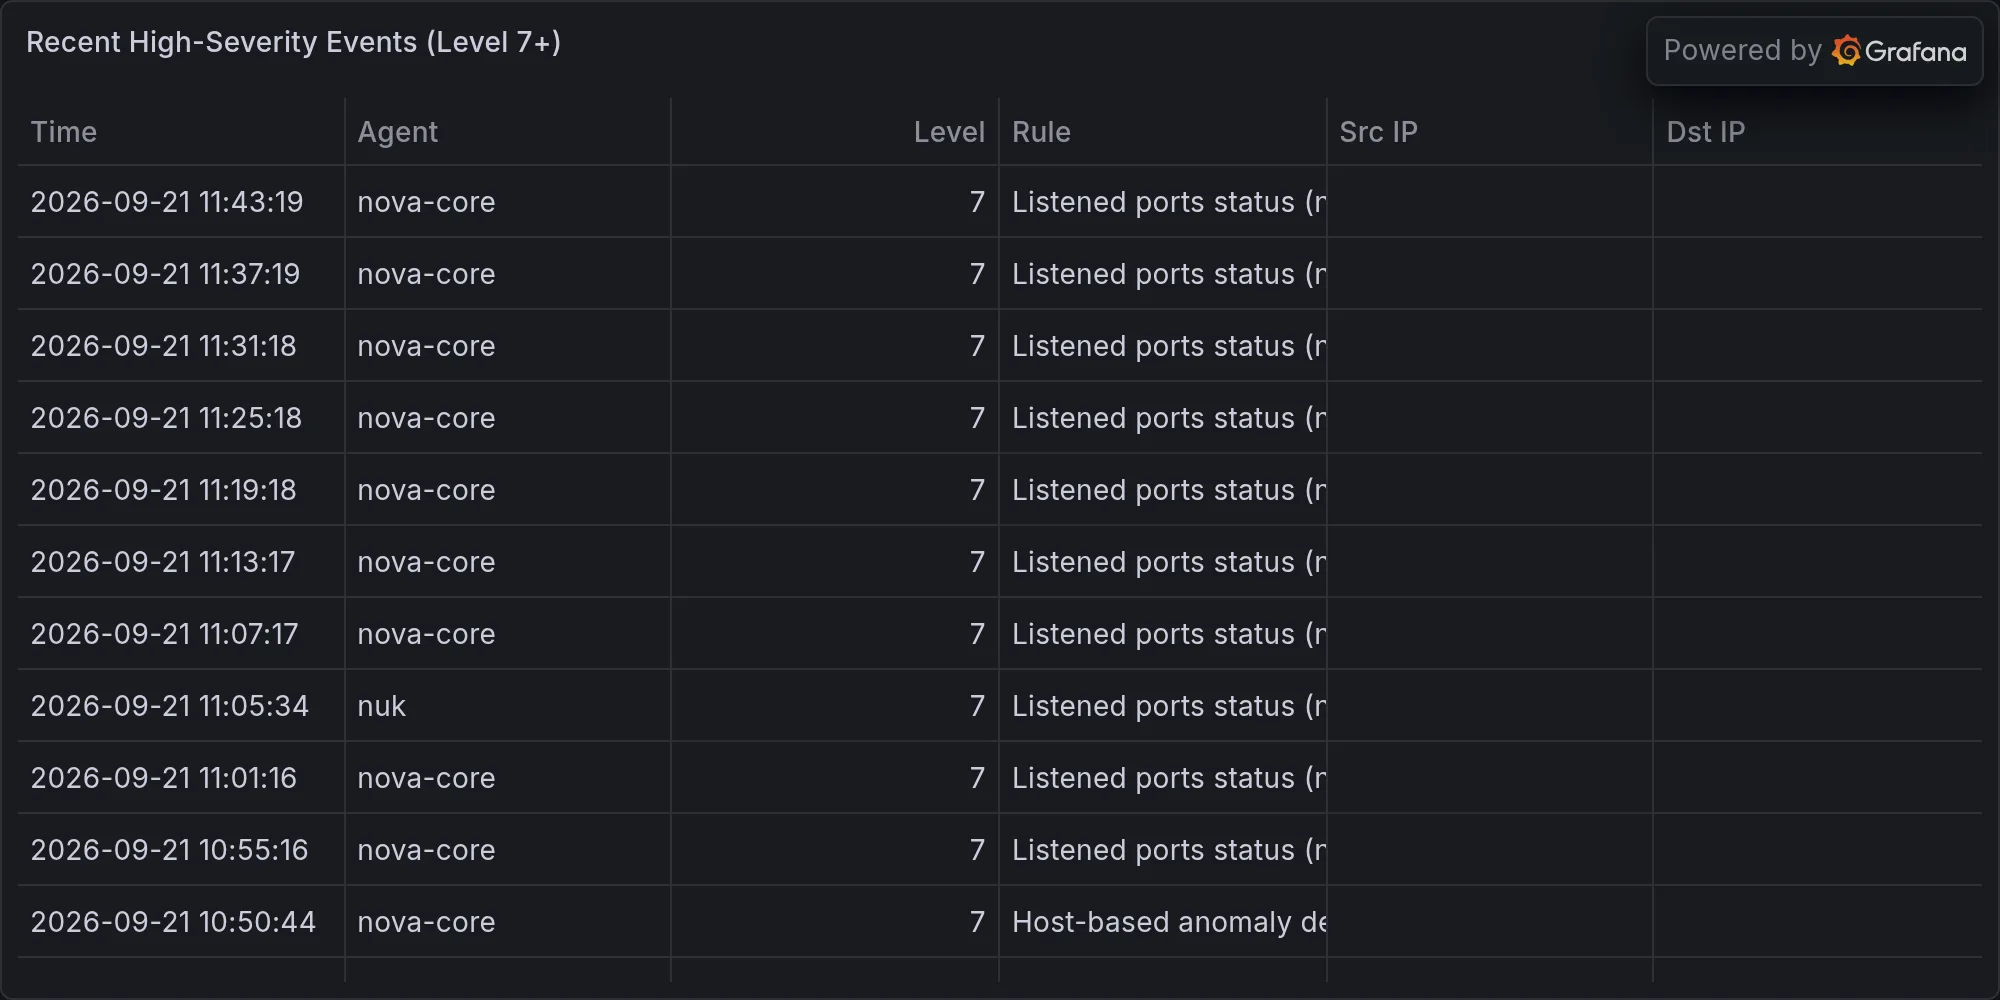
Recent high-severity events at publish time: