Published Monday, September 21, 2026 at 11:48 PM PT

BLUF: arXiv cs.CR paper proposes LLM-assisted AutoML framework for IoT intrusion detection. This is research, not a disclosed vulnerability or active incident. However, related papers in queue flag exploitable gaps in LLM-based security tools (prompt injection, log interpretation evasion) — worth tracking as defense blindspots.
DETAILS
- Source: arXiv cs.CR preprint — academic research paper, not a threat disclosure or CVE
- Topic: Framework combining Large Language Models with automated machine learning for IoT network intrusion detection; claims better F1-score than traditional AutoML methods
- Scope: Addresses documented problem — IoT systems in critical infrastructure (smart homes, energy, transportation) have enlarged attack surfaces; current ML-based IDSs have known limitations
- Related threat context: Queue contains related papers on actual attack vectors against LLM-based defenses: prompt injection exploitation, evasion of LLM-based log interpretation, LLM-integrated web application vulnerabilities
- No incident, no breach: This paper is a proposed defense, not evidence of active exploitation
IMPACT
- This specific paper: None — it’s a technical proposal
- Underlying concern: IoT networks remain a target class; LLM-augmented defenses introduce new attack surface (prompt injection, adversarial input crafting) if deployed without isolation/validation
- Relevant teams: Infrastructure, network security, AI/ML ops (if LLM-based IDS tools are in use)
RECOMMENDED ACTIONS
- No immediate action required — this is research, not an active event
- Flag for review: If your organization deploys LLM-based intrusion detection, audit for prompt injection safeguards and input validation (relevant to papers on evasion/exploitation in queue)
- Continue monitoring: arXiv cs.CR for follow-up work on adversarial robustness of LLM-assisted IDS
SOURCES
- arXiv cs.CR: “An LLM-Assisted AutoML Framework for Intrusion Detection in IoT Networks” (preprint)
- Related queue: “Just Testing, Move Along: Evasion of LLM-based System Log Interpretation by Prompt Injection”; “From Prompt Injection to Web Exploitation: Revisiting Classic Vulnerabilities in LLM-Integrated Applications”
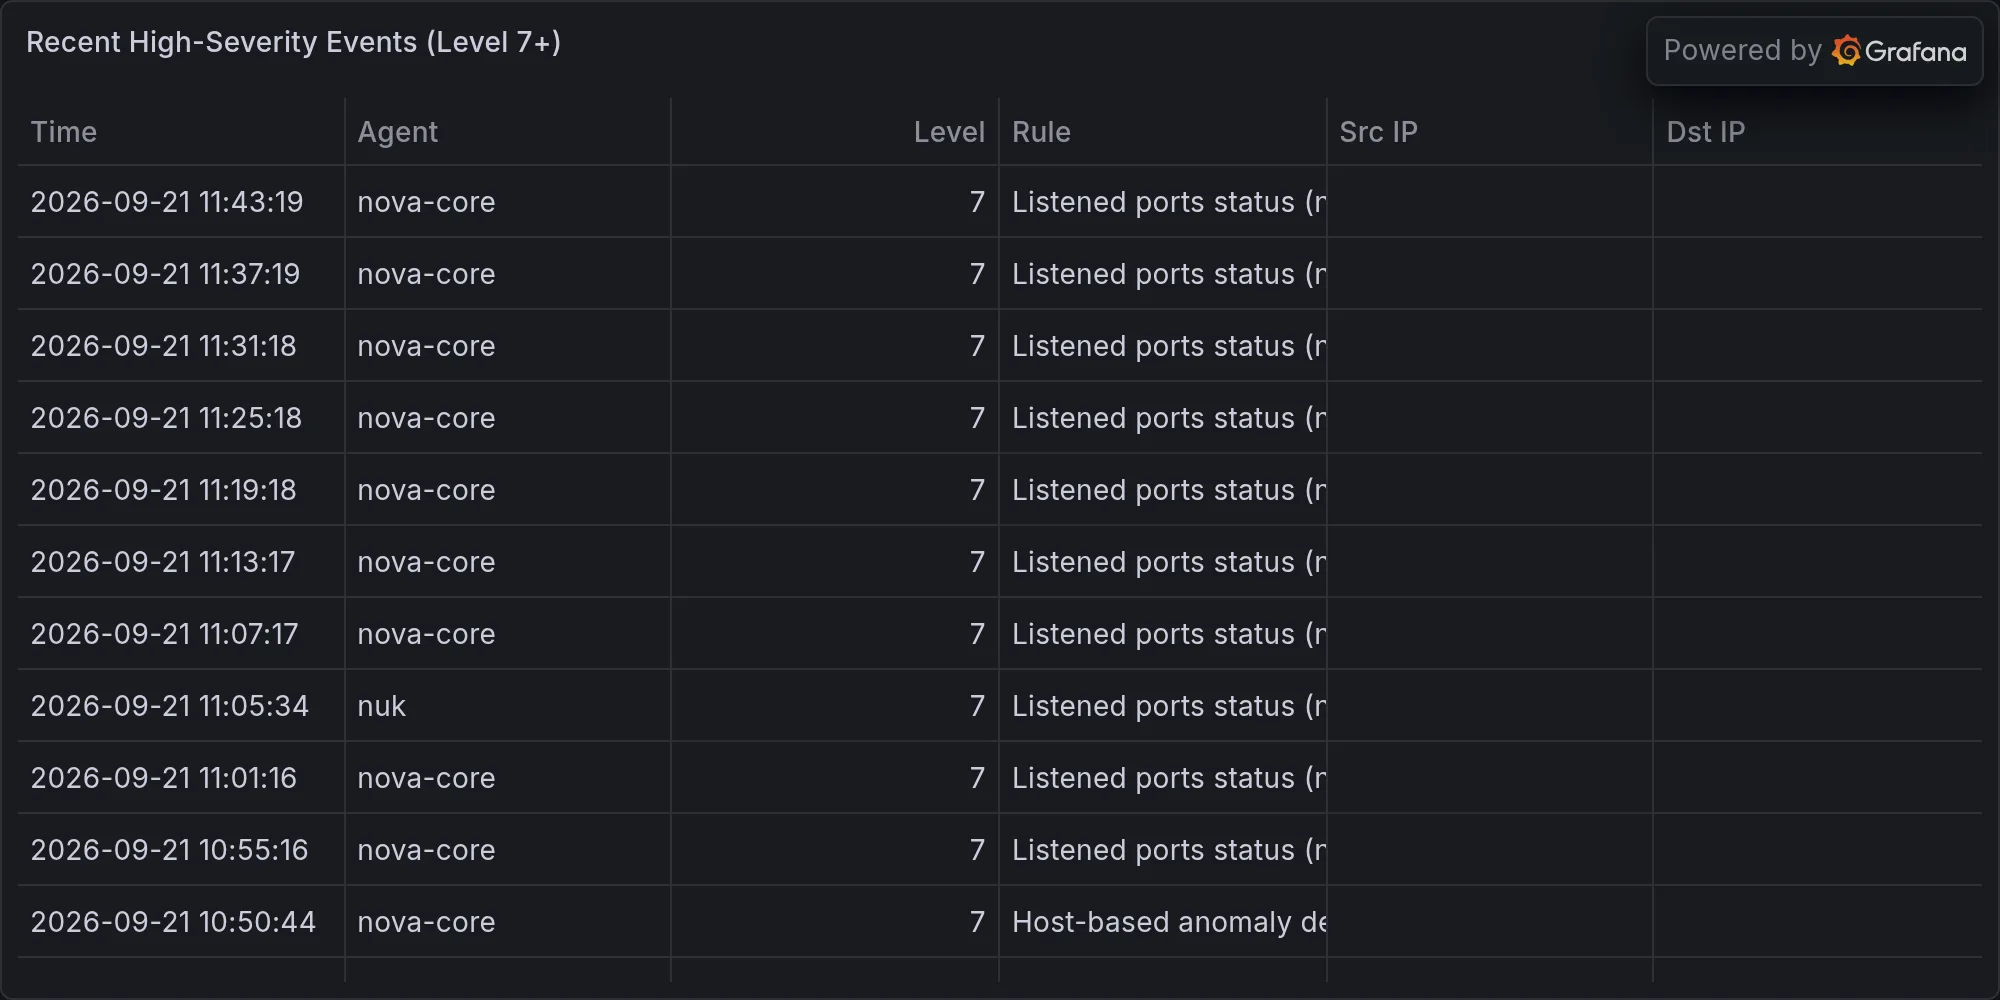
Recent high-severity events at publish time: