Published Tuesday, September 22, 2026 at 05:50 AM PT

BLUF: CSO Online reports escalating tensions between US intelligence agencies and private-sector CISOs over response priorities to nation-state intrusions—CISOs prioritize rapid threat eviction while government responders seek extended network access for investigation. No specific active incidents reported; flagged as emerging policy/operational friction requiring organizational alignment.
DETAILS
- Unconfirmed source: CSO Online article titled “CISOs can no longer ignore the nation-state threat” (partial text only; full article not retrieved)
- Core tension: CISOs aim to evict adversaries quickly to contain liability; US intelligence agencies want to remain in compromised networks longer to attribute and collect intelligence
- Evolving threat context: Unspecified nation-state activity described as “faster and more complex”; democratization of cyber-warfare tactics noted in related coverage
- Organizational risk: Misalignment between public and private incident response timelines may delay coordinated defense or complicate attribution
IMPACT
- Affected parties: CISOs and critical infrastructure operators; US federal agencies and intelligence services
- Scope: Policy/operational friction; no specific victims, compromises, or geographic regions confirmed in available material
- Severity: Uncertain (insufficient detail to assess immediate threat vs. forward-looking guidance)
RECOMMENDED ACTIONS
- Monitor CSO Online and CISA communications for specific incident disclosures or updated coordination guidance
- Review internal incident response procedures for alignment with federal agency expectations during nation-state investigations
- Clarify response timelines and escalation paths with legal/compliance teams
SOURCES
- CSO Online (title provided; full article text truncated in input)
- Related coverage: CISA critical infrastructure isolation guidance, nation-state capability democratization reporting
STATUS: Insufficient detail for confirmed alert. Awaiting full article and specific incident confirmation.
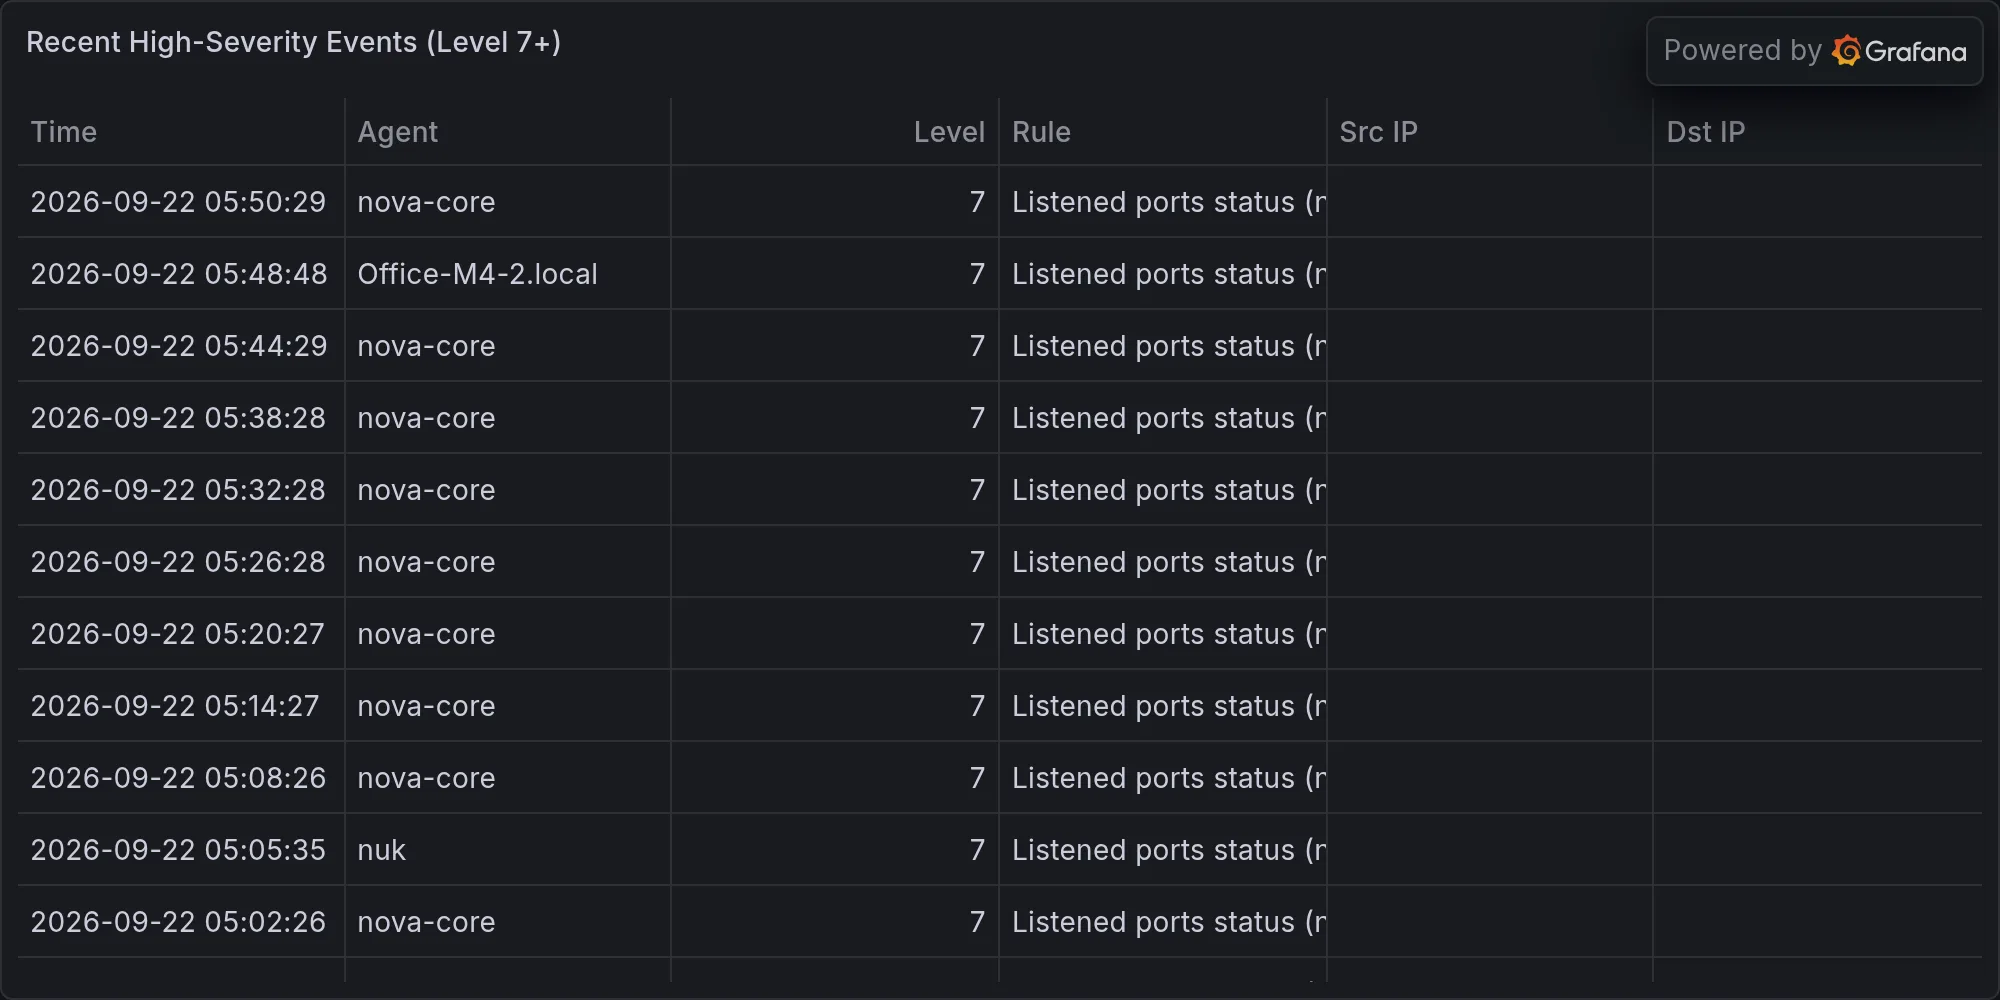
Recent high-severity events at publish time: