Published Tuesday, September 22, 2026 at 11:52 AM PT

BLUF: D-Link has issued a vulnerability warning for maximum-severity zero-day flaw in DIR-822A router models. Technical details remain scarce; no active exploitation yet confirmed. Affected organizations should isolate DIR-822A devices from critical network paths pending patch release and full vulnerability disclosure.
DETAILS:
- Vendor warning confirmed: D-Link disclosed existence of critical zero-day in DIR-822A router line (specific firmware versions unconfirmed from available source)
- Severity rating: Maximum severity assigned; no CVSS or CVE identifier provided in available reporting
- Zero-day status: Unpatched vulnerability; no public exploit code reported to date
- Patch status: UNKNOWN — D-Link advisory does not specify expected patch timeline or interim fixes
- Attack vector: NOT YET SPECIFIED — mechanism of exploitation not disclosed in available source material
IMPACT:
- Scope: D-Link DIR-822A router customers (exact installed base unknown)
- Affected layers: Router administrative access, network perimeter control, or remote access — depends on attack vector (unconfirmed)
- Blast radius: Unquantified; contingent on whether flaw enables unauthenticated RCE, authentication bypass, or other primitives
RECOMMENDED ACTIONS — IMMEDIATE:
- Identify and isolate any DIR-822A routers in your environment from direct internet exposure
- Monitor DIR-822A administrative access logs for anomalies
- Check D-Link’s official security advisory page for CVE identifier and patch ETA (expected within 24–72 hours)
- Prepare network segmentation policy or contingency swap if DIR-822A is primary edge device
SOURCES:
- BleepingComputer (title only; full article unavailable at alert generation)
STATUS: Unconfirmed beyond title and vendor confirmation. Awaiting D-Link CVE/advisory with technical details and patch timeline.
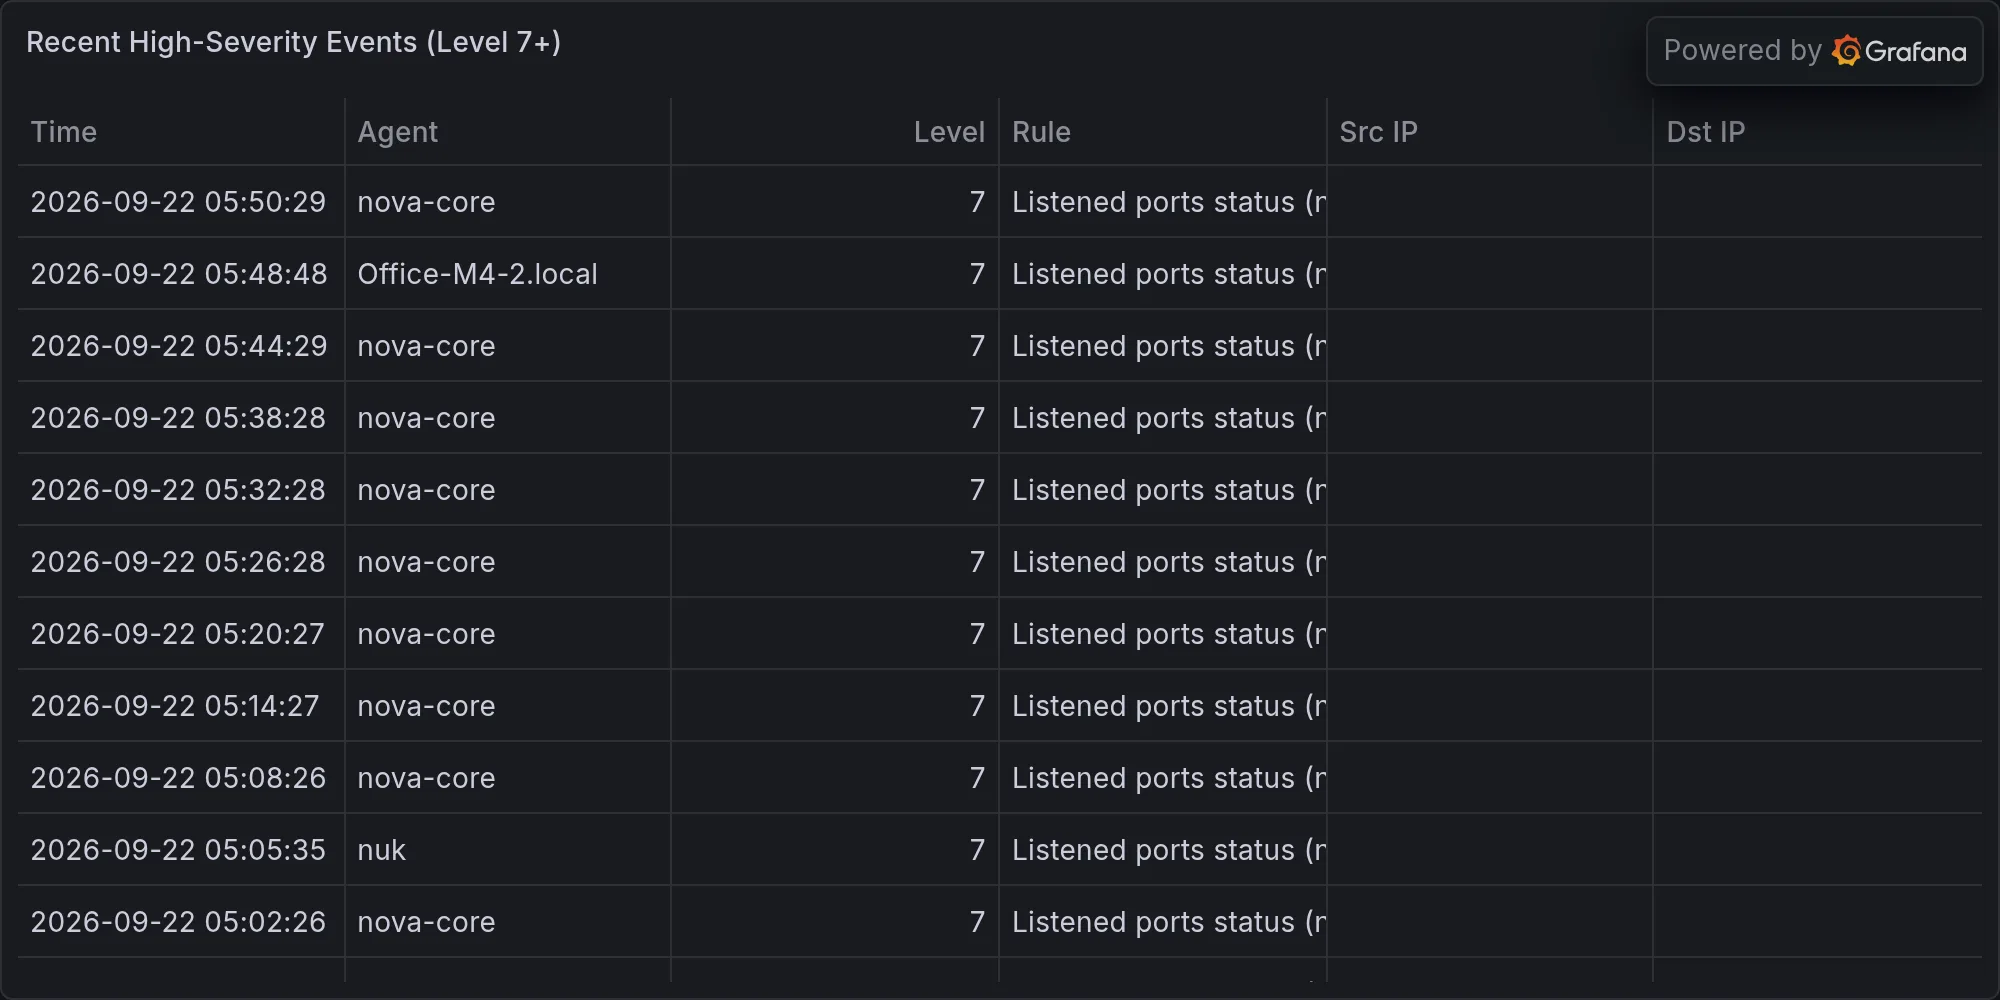
Recent high-severity events at publish time: