Published Tuesday, September 22, 2026 at 05:49 AM PT

BLUF: CSO Online articles flagging accelerating nation-state cyber threats and CISO capability gaps. No specific incident, organization, or attack vector confirmed. Source material is truncated industry analysis, not incident reporting. Status: monitoring for specific breach/attack claims.
DETAILS
- Article series from CSO Online under review; headlines reference “nation-state threat,” CISA guidance on critical infrastructure isolation, and CISO organizational/budget challenges. No confirmed incident attached to these headlines.
- Source material provided consists of article title fragments and incomplete context snippets—insufficient to isolate a specific threat actor, target, methodology, or affected entity.
- Related context references CISA’s work on insider threat programs, critical infrastructure resilience, and deprecation of CISA’s monthly vulnerability bulletin (transition to AI-driven threat dissemination). These are policy/process updates, not incident confirmation.
- No timeline, CVE identifiers, attack names, or compromised infrastructure identified in available material.
IMPACT
Unconfirmed. Cannot assess scope, affected systems, or organizations without concrete incident data. The articles appear to be industry trend analysis and CISO leadership/budget commentary rather than incident reporting.
RECOMMENDED ACTIONS
- Flag for continuous monitoring: if CSO Online publishes specific incident details (breach name, affected org, TTP details, timeline), escalate immediately.
- Do not distribute as a confirmed incident until specific attack/breach is named and sourced.
SOURCES
CSO Online article series (titles only; full articles not provided in alert material). CISA guidance references noted but not confirmed as related to active threat.
Status: If full article text or incident details become available, re-alert with specifics.
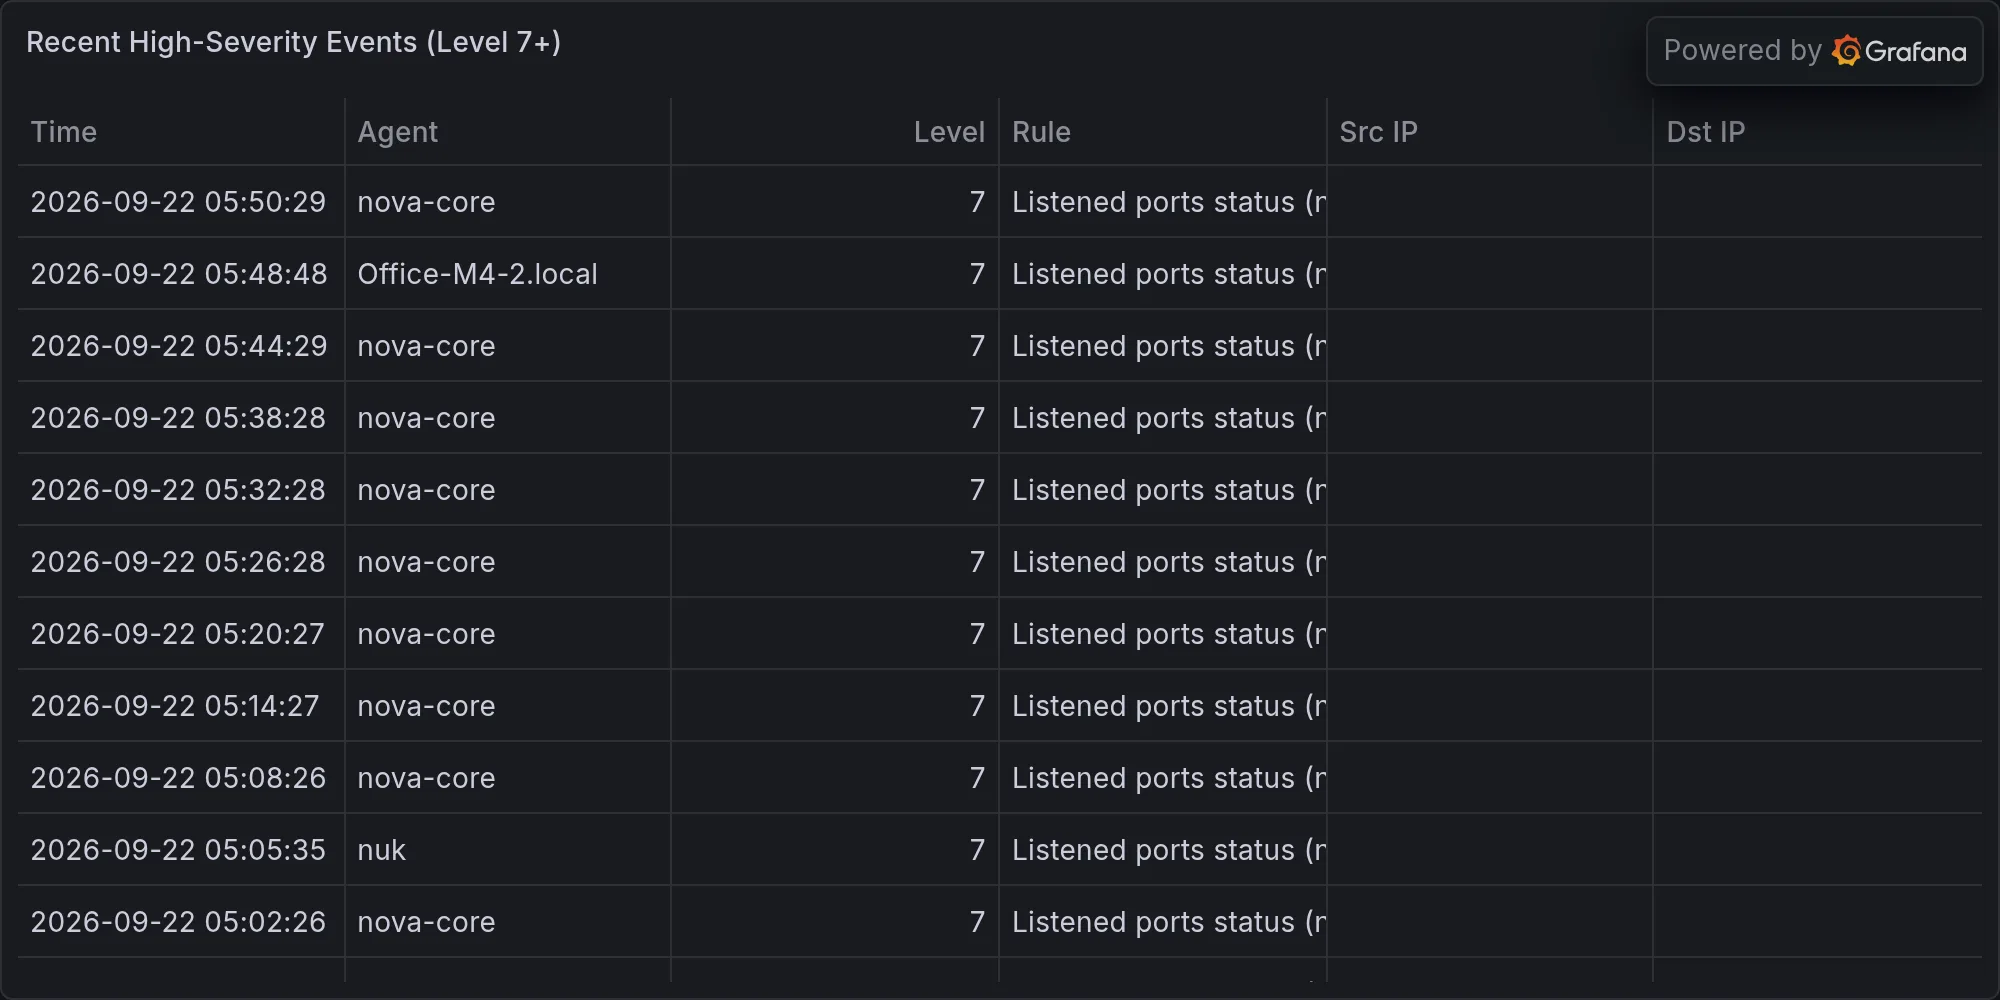
Recent high-severity events at publish time: