Published Wednesday, September 23, 2026 at 11:30 AM PT

BLUF: WordPress has released an emergency patch for CVE-2026-87902, a critical vulnerability in WordPress Core that allows unauthenticated attackers to load arbitrary local PHP files and achieve remote code execution under specific server and theme conditions. Organizations running WordPress must patch immediately.
DETAILS
- Vulnerability: CVE-2026-87902 in WordPress Core permits unauthenticated actors to load arbitrary local PHP files on affected systems.
- Severity: Critical; conditional RCE possible if server and theme configuration match specific criteria (exact conditions not yet fully disclosed).
- Authentication: No authentication required to trigger the vulnerability; exploitation requires no user account.
- Vendor Response: WordPress has released an emergency security update; no timeline for active wild exploitation confirmed at this time.
- Scope: Affects WordPress Core installations; exploitation surface varies by server configuration and active theme.
IMPACT
- Primary Risk: Unauthenticated remote code execution on affected WordPress installations.
- Affected Base: All unpatched WordPress Core installations with server/theme configurations matching exploit conditions.
- Blast Radius: WordPress powers ~43% of all websites globally; broadly deployed across enterprises, SMBs, and public-facing sites.
- Data Exposure: Full server compromise possible, including database access, file system access, and lateral movement into connected infrastructure.
RECOMMENDED ACTIONS
- Immediate: Update all WordPress Core instances to the latest patched version released by WordPress Foundation.
- Inventory: Audit all WordPress deployments across your environment and confirm patch status within 24 hours.
- Detection: Monitor web server logs for suspicious PHP file load attempts and unusual activity on WordPress installations.
- WAF/IDS: Deploy rules to detect and block exploitation attempts of this vulnerability if patching is delayed.
- Credential Rotation: If any WordPress admin account appears compromised or servers show signs of unauthorized access, rotate credentials and review logs.
SOURCES
- SOC Prime threat intelligence feed — CVE-2026-87902 notice
- WordPress Security Advisory (emergency patch release)
STATUS: Confirmed vulnerability with patch available. No confirmed exploitation in the wild at publication. Organizations should treat as urgent.
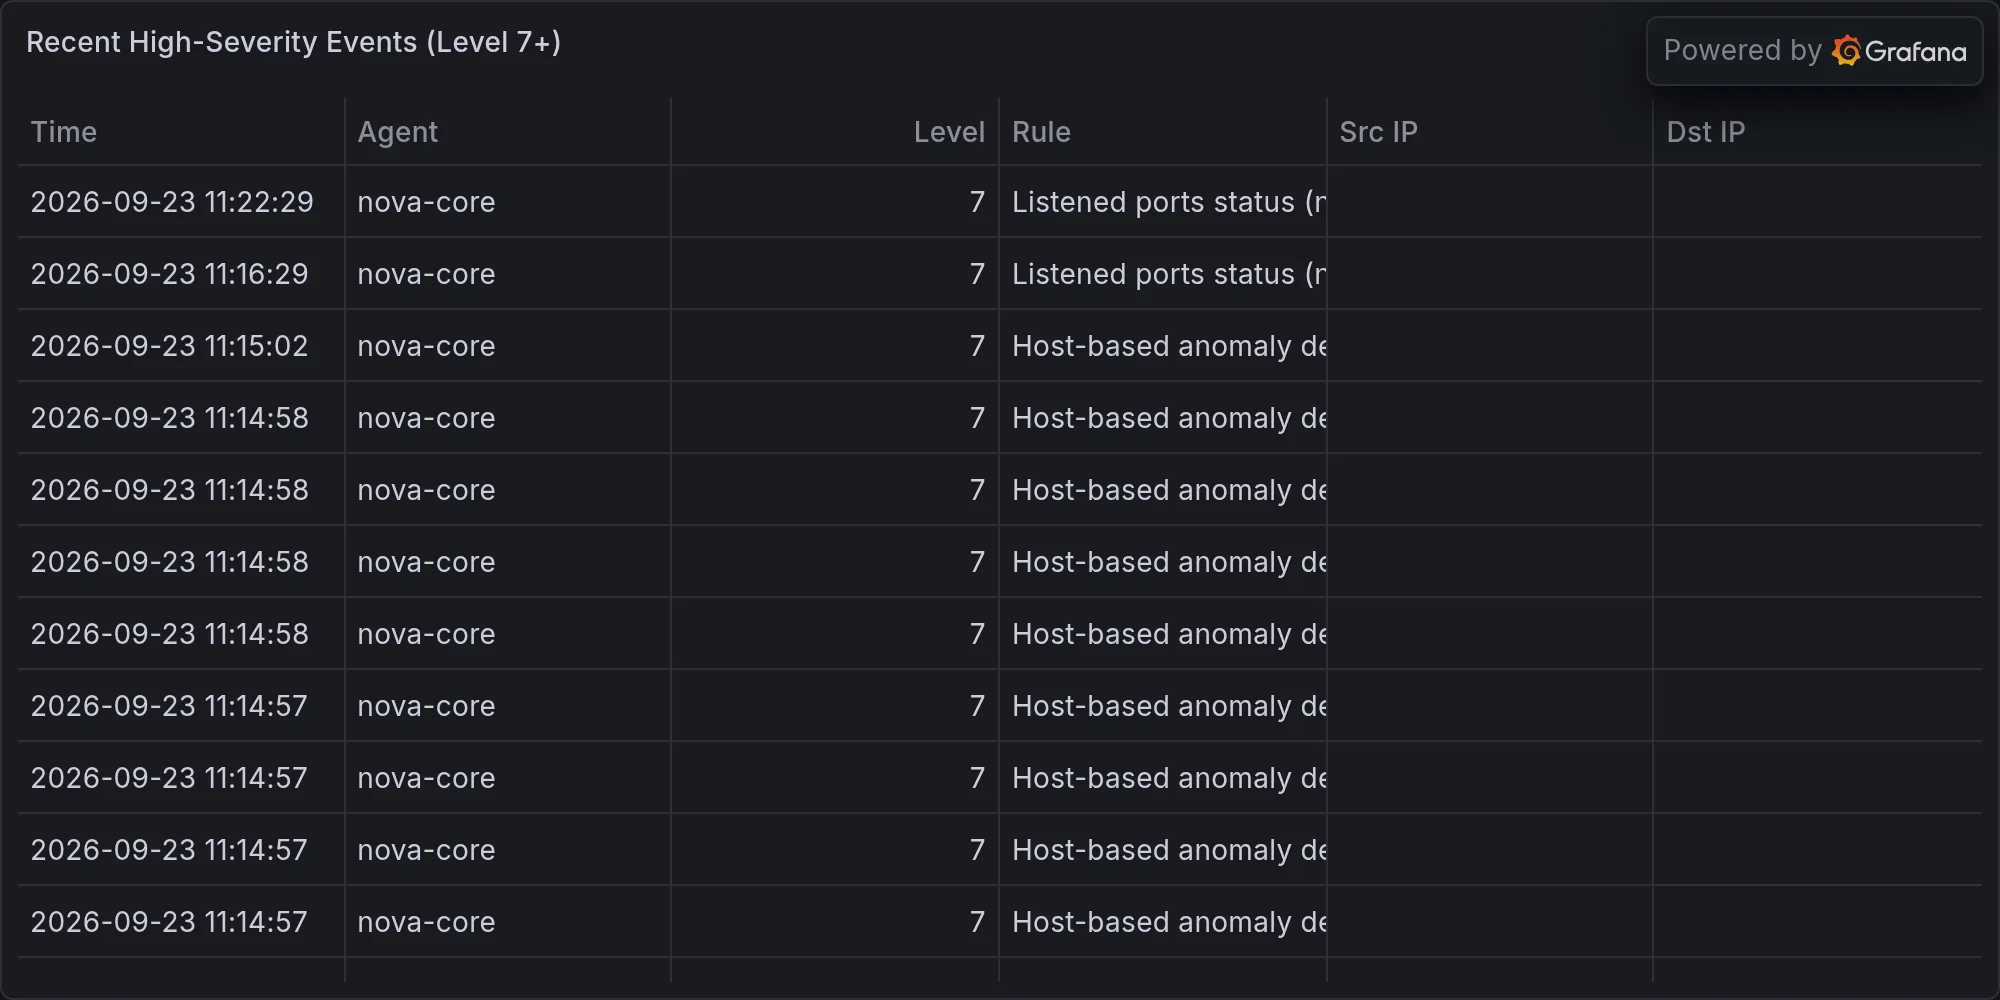
Recent high-severity events at publish time: