Published Wednesday, September 23, 2026 at 05:26 AM PT

BLUF: F5 BIG-IP APM contains an unauthenticated remote code execution vulnerability currently exploited in active attacks. Apply patches to all instances immediately. Target priority: OAuth/authentication-facing deployments.
DETAILS
- Zero-day RCE in BIG-IP APM — Attackers can execute arbitrary code without authentication; F5 has confirmed the flaw and released patches
- Active exploitation confirmed — Multiple threat actors are exploiting this vulnerability in the wild; at least one campaign deployed Linux rootkits following successful compromise
- OAuth servers at elevated risk — The vulnerability is being weaponized specifically against BIG-IP APM systems deployed as OAuth authentication gateways
- Exploit timeline unclear — Sources confirm zero-day exploitation occurred before patches became available; specific disclosure/patch release dates not provided in available reporting
- Patch availability confirmed — F5 has released fixes; specific version numbers and CVE identifier not included in summaries provided
IMPACT
- Scope: Any organization operating vulnerable BIG-IP APM instances, with highest risk for those exposed to untrusted networks or handling OAuth/identity services
- Attack surface: Unauthenticated access means no valid credentials required; internet-facing instances are immediately vulnerable
- Post-exploitation: Confirmed rootkit deployment indicates attackers are establishing persistence and preparing for lateral movement
RECOMMENDED ACTIONS
- Immediate: Patch all BIG-IP APM systems with F5’s released fixes
- Priority-order: Patch systems acting as OAuth gateways or authentication services first
- Forensics: Audit event logs and process lists for signs of exploitation (unusual processes, outbound connections, rootkit signatures)
- Detection: Monitor for F5 security bulletins or CISA alerts for IOCs (indicators of compromise)
SOURCES
- BleepingComputer (primary reporting)
- The Hacker News
- News4Hackers
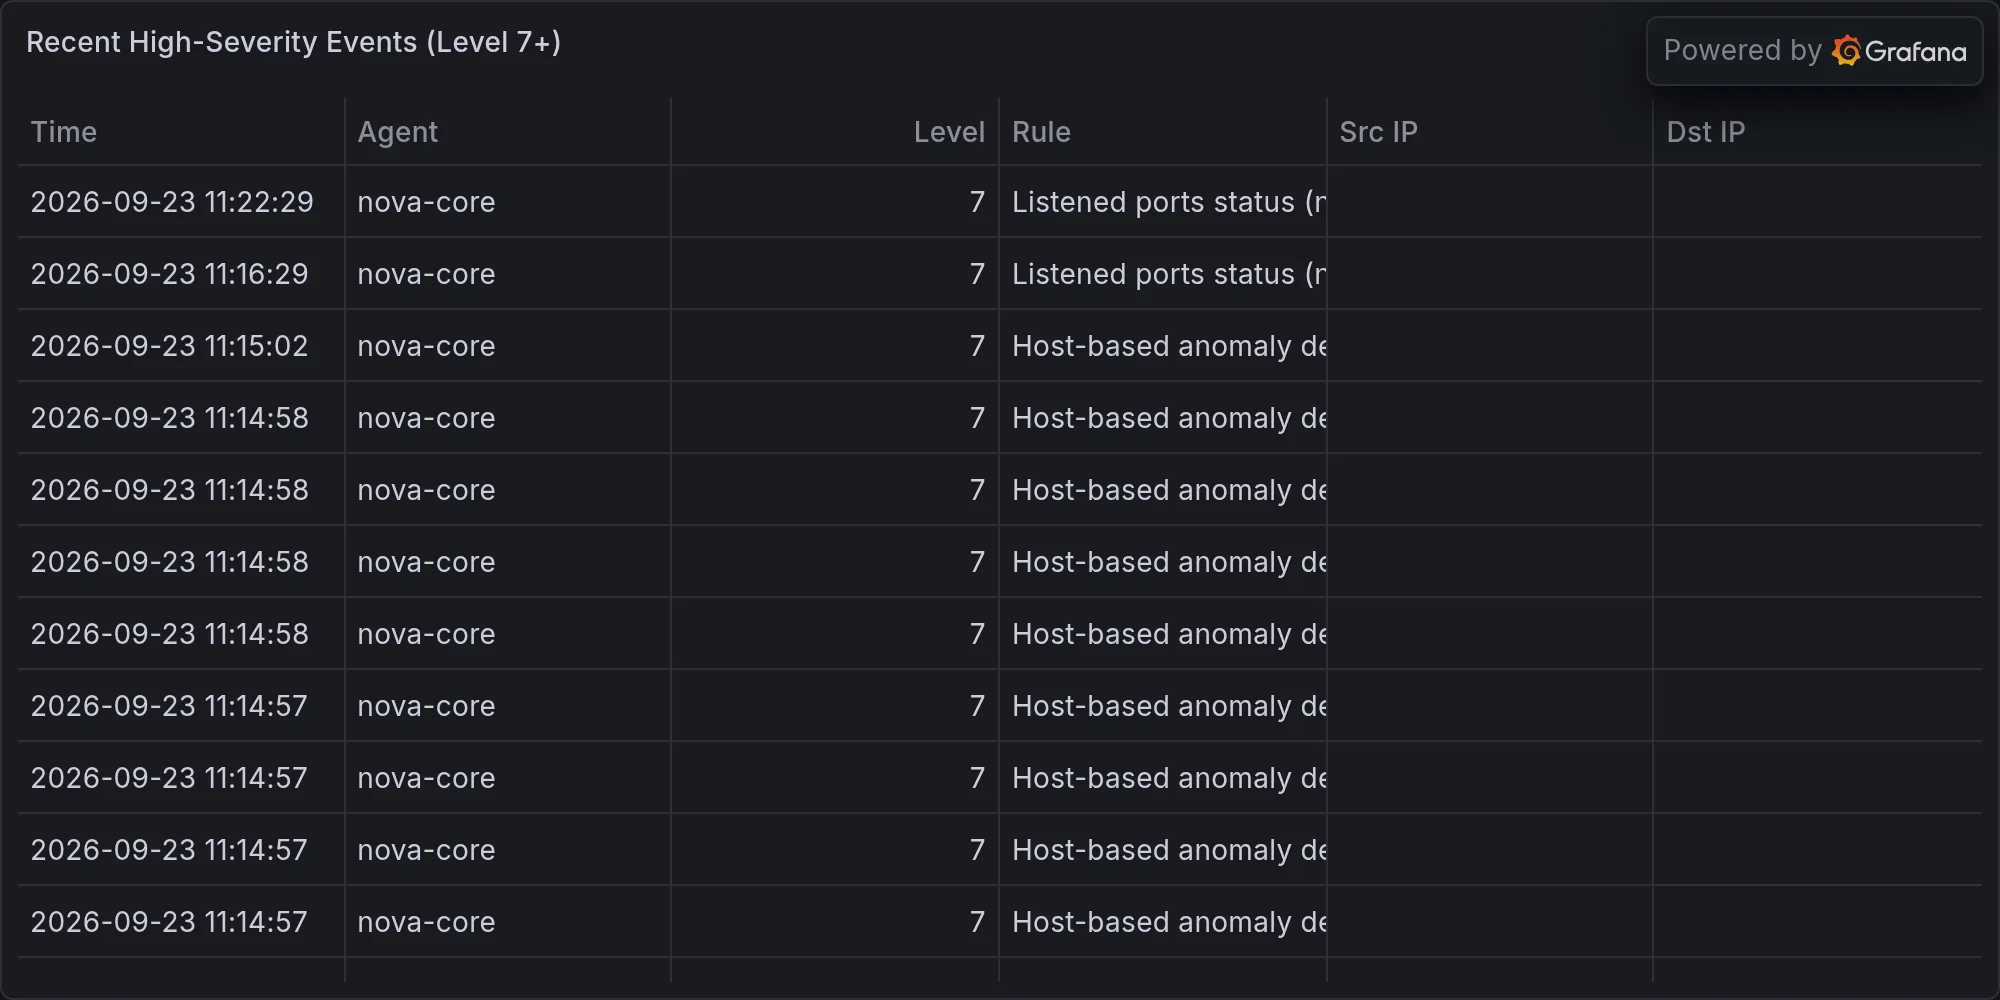
Recent high-severity events at publish time: