Published Wednesday, September 23, 2026 at 11:29 AM PT

BLUF: F5 BIG-IP Access Policy Manager (APM) is vulnerable to a critical, unauthenticated remote code execution zero-day (CVE-2026-94127) that is actively being exploited in the wild. Affected organizations running BIG-IP APM must immediately inventory instances, isolate systems from untrusted networks, and monitor for exploitation attempts. Patch availability status is currently unknown.
DETAILS:
- Vulnerability: Unauthenticated remote code execution in F5 BIG-IP Access Policy Manager (APM)
- Exploitation vector: Specially crafted network traffic; no user interaction required
- Status: Zero-day with confirmed active exploitation in the wild
- Attack surface: Internet-facing BIG-IP APM appliances
- Scope of affected product lines: BIG-IP APM (specific versions not yet detailed in available advisories)
IMPACT:
- Who: Any organization running F5 BIG-IP APM, particularly internet-facing instances
- What: Complete compromise of the APM appliance; potential lateral movement to protected network segments
- Risk tier: CRITICAL — unauthenticated RCE on network access control layer
- Current threat level: ACTIVE — exploitation observed in the wild
RECOMMENDED ACTIONS — IMMEDIATE (Next 4 hours):
- Inventory: Identify all F5 BIG-IP APM instances in your environment; prioritize internet-facing systems
- Isolate: If possible without disrupting critical services, move affected BIG-IP APM systems behind additional network-layer access controls or WAF rules
- Monitor: Enable logging for anomalous traffic patterns to BIG-IP APM; watch for RCE attempt signatures (F5 security bulletin pending)
- Vendor check: Monitor F5 security advisories at f5.com/security for CVSS score, affected versions, and patch availability
- Alert upstream: Notify your security team, network operations, and business stakeholders of the risk
NEXT STEPS — If patches are available:
- Prioritize patching based on exposure (internet-facing > internal-only)
SOURCES:
- SOC Prime CVE Intelligence (CVE-2026-94127 disclosure)
- F5 Security Advisories (pending full details)
NOTE — Information Gaps: This alert is based on preliminary CVE disclosure. Affected BIG-IP versions, CVSS score, and patch availability are not yet available in the material provided. Monitor F5’s official security bulletin for detailed mitigation and version guidance.
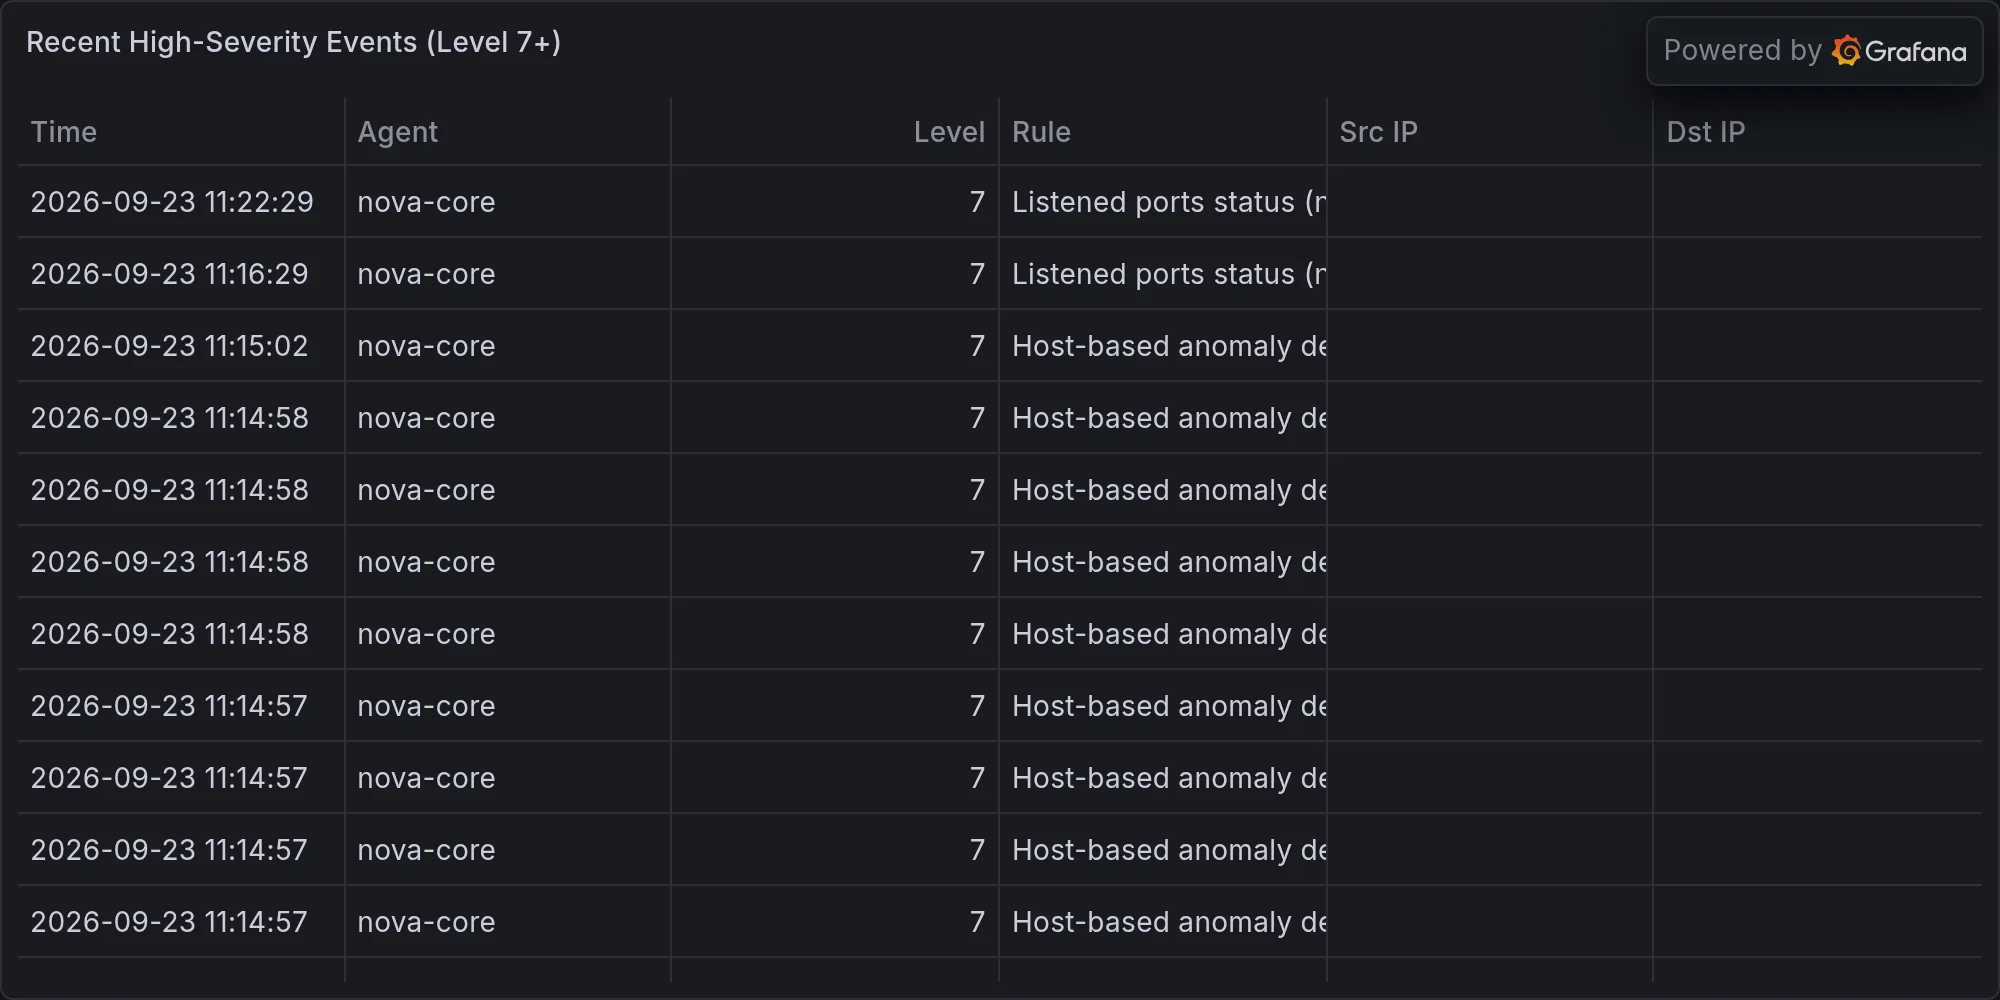
Recent high-severity events at publish time: