Published Thursday, September 24, 2026 at 05:40 PM PT

BLUF: A bipartisan group of House and Senate members has introduced legislation to expand CISA cybersecurity authority over biotechnology, seeking to formally designate biotech as critical infrastructure and establish federal oversight equivalent to other protected sectors. The bill aims to close a regulatory gap that currently leaves the biotech supply chain without dedicated federal cyber defense mandates. Specific bill details, sponsor list, and formal introduction status not confirmed in available reporting.
DETAILS
- Current Regulatory Gap: Biotechnology operates without its own critical infrastructure designation under federal law, leaving it without mandatory CISA oversight and incident reporting requirements despite its role in national health and security supply chains.
- Legislative Objective: Bipartisan lawmakers seek to bring biotech under CISA authority with security and resilience mandates equivalent to designated critical sectors (energy, water, telecommunications, healthcare).
- Provisions and Timeline: Specific bill provisions, threat models justifying escalation, and Congressional timeline not detailed in source material; bill name, number, and formal introduction status require verification.
- Pattern: Follows recent biotech cybersecurity legislative activity (Health Infrastructure Security Act) and broader Congressional trend of sector-specific cyber legislation post-recent attacks (telecom post-Salt Typhoon, water utilities, electric grid quantum threats).
- Source Limitation: CyberScoop reporting confirmed; primary bill text, sponsor names, formal announcement, and CISA response unavailable in provided material.
IMPACT
- Affected Sector: U.S. biotechnology R&D, manufacturing, vaccine production, diagnostic firms, supply chain logistics, and life sciences entities currently undesignated and outside formal CISA critical infrastructure framework.
- Regulatory Consequence: If enacted, would subject biotech to CISA incident reporting timelines, vulnerability disclosure protocols, and mandatory cyber resilience assessments parallel to existing rules for power, water, and telecom.
- Legislation Status: Proposed but unconfirmed as formally introduced—no verification of committee assignment, co-sponsor count, or floor vote timeline available.
RECOMMENDED ACTIONS
- Biotech Organizations: Monitor Congress.gov for formal bill introduction; expect potential future CISA incident reporting and assessment requirements if legislation advances; audit current cyber posture against likely critical-infrastructure-equivalent standards.
- Federal Agencies: Await formal bill text and sponsor list before drafting implementation guidance or issuing CISA directives; coordinate with existing critical infrastructure cybersecurity frameworks to avoid overlap.
- Media/Analysts: Verify bill number, complete sponsor list, formal introduction date, and exact provisions via official Congressional sources.
SOURCES
- CyberScoop: “House and Senate members propose legislation for CISA to step up cyber defenses for biotech” (2026; exact date unconfirmed)
- Unconfirmed / Requires Verification: Bill name, number, full sponsor list, detailed provisions, formal introduction date, CISA statement or response
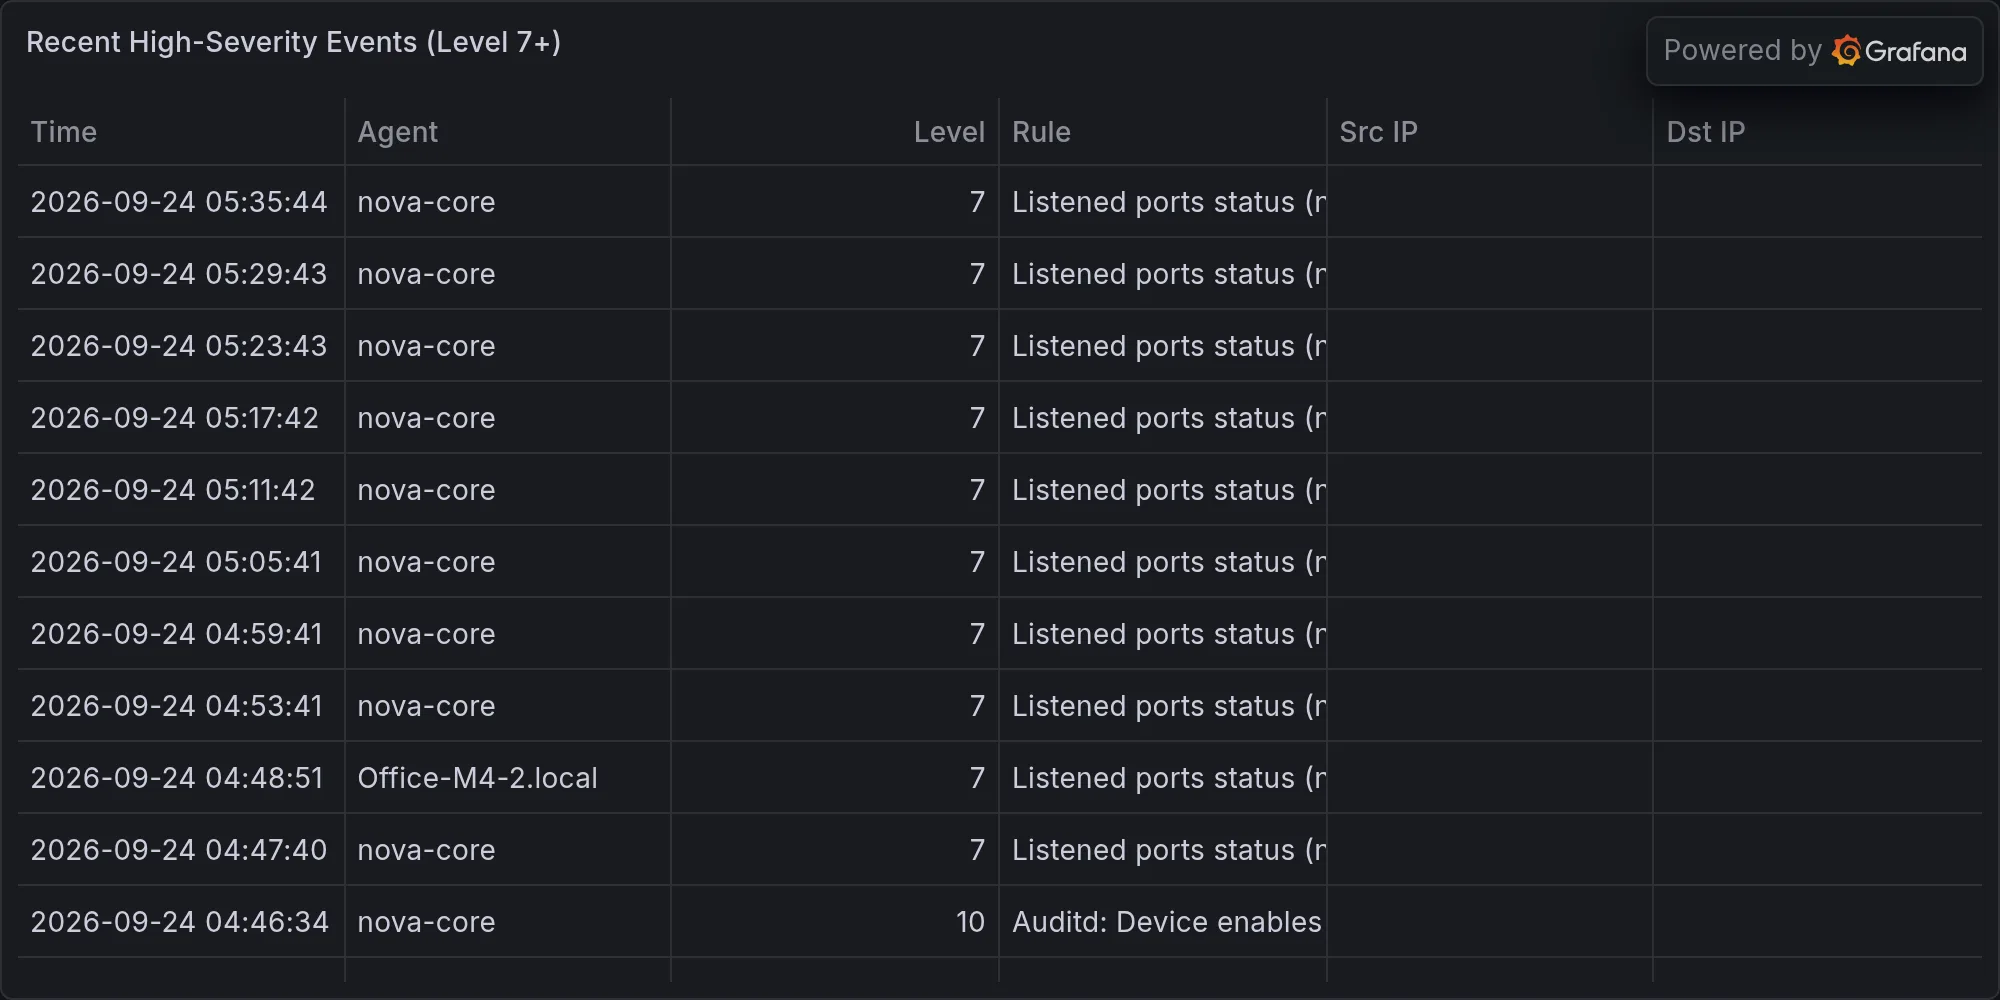
Recent high-severity events at publish time: