Published Thursday, September 24, 2026 at 05:41 PM PT

BLUF: Cryptocurrency exchange Bitget confirmed a $351.6 million unauthorized transfer from its hot wallet infrastructure on September 24, 2026 at 18:31 UTC. The breach accessed Bitget’s internal systems directly; customer private keys and cold wallets remain uncompromised. Bitget CEO suspects North Korea’s Lazarus Group but has published no supporting technical evidence. Withdrawal services suspended; customer funds protected by Bitget’s $464M+ User Protection Fund.
DETAILS:
Incident: Unauthorized transfers from multiple Bitget hot wallets detected 18:31 UTC, September 24, 2026. Total confirmed theft: $351.6 million in cryptocurrency. Entry method remains under investigation.
Scope of compromise: Limited to hot wallet infrastructure and “part of the warm-wallet layer.” Cold wallets unaffected. Customer private keys not obtained. Attackers bypassed wallet authorization without extracting underlying cryptographic material.
Direct system breach confirmed: CEO Gracy Chen stated the incident involved “a direct breach of Bitget’s systems or servers,” not social engineering or customer-side compromise. Attackers transferred stolen funds directly rather than forging withdrawal requests from individual accounts.
Insider speculation unresolved: Chen addressed speculation of an inside job. While she characterized the probability as “quite low” and stated the company does not “currently believe” an employee was involved, investigators have not ruled out insider assistance. Bitget employs ~2,000 people; no evidence of employee involvement has been published.
Attribution uncertain: Bitget suspects the Lazarus Group (North Korean state-backed operation). At time of publication, no technical evidence supporting this attribution has been released or verified by independent analysts.
IMPACT:
- Direct loss: $351.6 million confirmed stolen from exchange infrastructure
- Customer impact: Minimal — Bitget states customer balances are accurate and unaffected. Stolen amount is covered by the exchange’s User Protection Fund (balance: $464+ million at time of incident)
- Service disruption: Withdrawal services suspended pending security review. Deposits and trading remain operational
- Industry signal: Represents one of the larger cryptocurrency exchange breaches in 2026; demonstrates continuing vulnerability of institutional hot-wallet systems
RECOMMENDED ACTIONS:
- Bitget users: No immediate action required for account security (keys uncompromised). Monitor withdrawal service status updates; service restoration timeline not yet announced.
- Cryptocurrency firms: Review hot-wallet authorization protocols, access logging, and system segmentation. Evaluate whether Bitget incident reveals systematic vulnerability in wallet orchestration layers.
- Incident responders: Monitor theft addresses for fund movement and potential mixing. Await Bitget’s publication of technical forensics or incident timeline to confirm or refute Lazarus Group attribution.
SOURCES:
HackRead (Sept 25, 2026); Bitget official statement via CEO Gracy Chen; article reporting current as of publication—technical evidence and insider investigation findings pending.
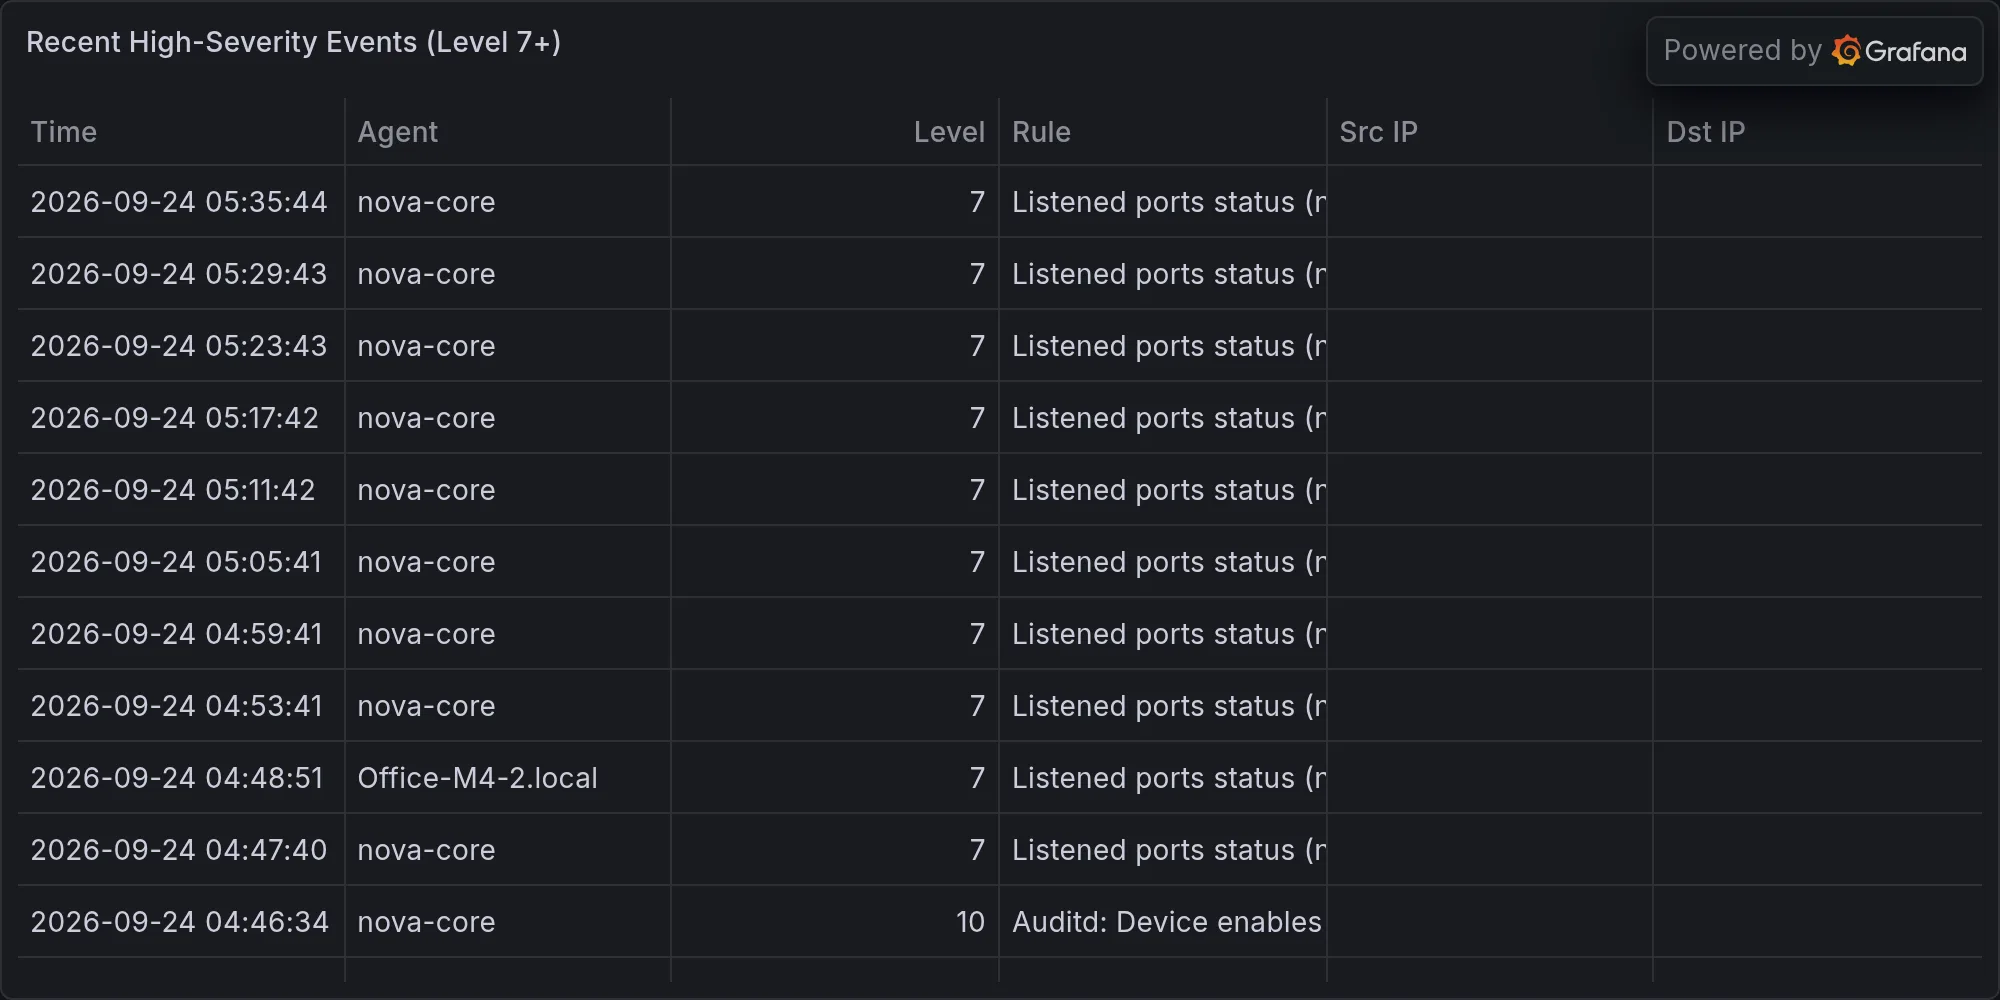
Recent high-severity events at publish time: