Published Thursday, September 24, 2026 at 05:36 AM PT

BLUF: Schneier on Security reports observation of sophisticated malware variant with technical characteristics consistent with nation-state capability; no attribution confirmed. Active CAPTCHA-based social engineering variant in circulation. Tracking — details insufficient for immediate action guidance.
DETAILS
- Malware sophistication assessed as matching nation-state capability level (Schneier direct observation); no direct evidence of attribution available
- CAPTCHA-themed social engineering variant confirmed in circulation — frames malware payload as CAPTCHA challenge to trick users into execution
- No confirmed CVE, target sector, affected systems, or geographic focus provided in available material
- Detection/mitigation techniques not yet documented
- Schneier assessment: insufficient evidence to attribute or identify specific threat actor
IMPACT
- Scope: UNKNOWN — no confirmed target sector, geography, or affected systems identified
- Risk: Moderate to high (if nation-state assessment correct and active exploitation ongoing)
- User population at risk: Organizations with high-value data; standard users via social engineering vector
RECOMMENDED ACTIONS
- Monitor for Schneier on Security follow-up posts with technical indicators or IOCs
- User education: Remind teams that CAPTCHAs will never ask users to download software; legitimate CAPTCHAs run client-side in-browser
- Block: If specific IOCs/hashes/domains surface, add to malware detection and block lists
- Defer specific technical controls until variant identification and technical analysis available
SOURCES
- Schneier on Security (Bruce Schneier blog) — preliminary observation only; formal analysis pending
STATUS: DEVELOPING. This alert reflects fragmentary reporting. Full technical details (malware name, IOCs, affected platforms, confirmed targets) are not yet available. DO NOT treat nation-state assessment as confirmed attribution.
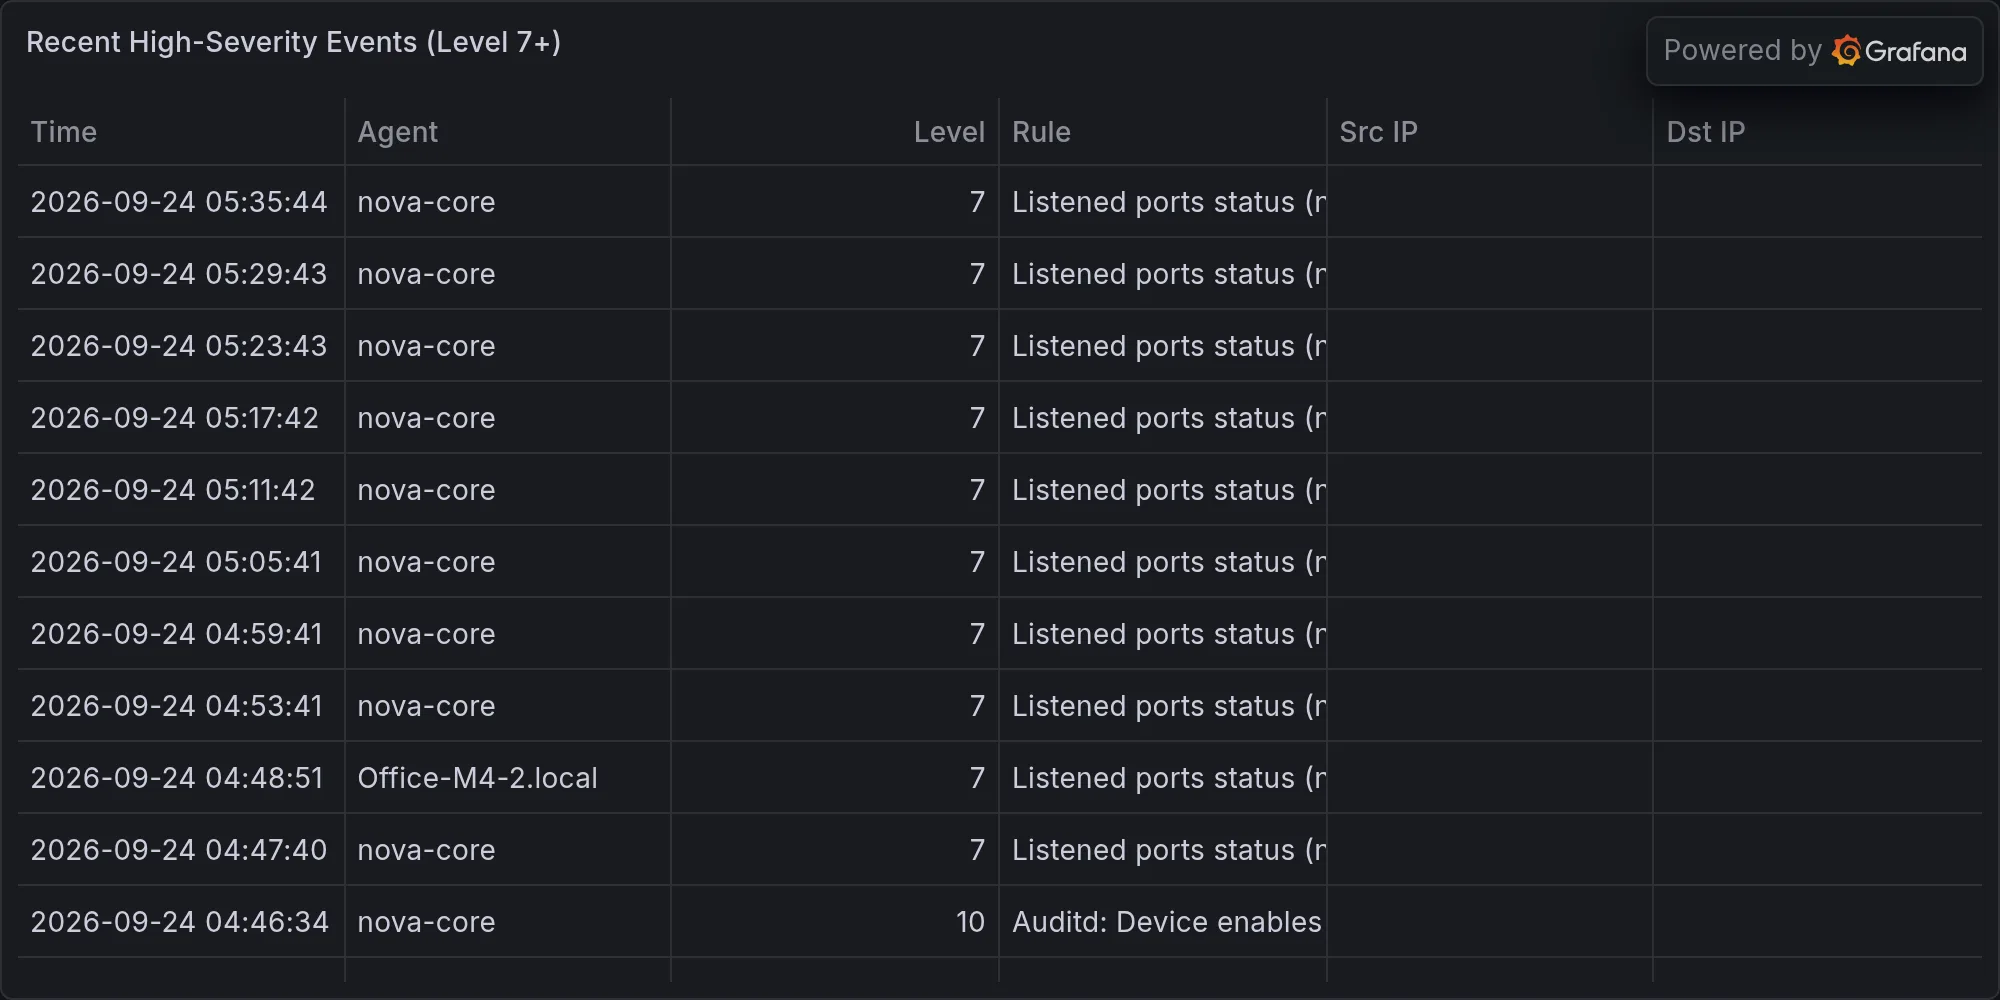
Recent high-severity events at publish time: