Published Friday, September 25, 2026 at 05:45 PM PT

BLUF: ShinyHunters threat group is conducting a mass exploitation campaign against Oracle PeopleSoft installations using a URL encoding bypass technique that circumvents WAF and reverse proxy protections. Organizations running unpatched PeopleSoft deployments are at active risk; threat actor is reaching protected endpoints and extracting data at scale.
DETAILS:
- Attack vector: ShinyHunters encodes forward slashes as
%2Fin URLs (e.g.,%2FPSEMHUB%2Finstead of/PSEMHUB/), bypassing WAF and reverse proxy rules that match against literal path strings. - Detection gap: Most Web Application Firewalls and reverse proxies evaluate rules before URL decoding. The PeopleSoft application server decodes the request and routes it to the vulnerable servlet, allowing the payload to reach endpoints that should be blocked.
- Scale: Campaign has successfully compromised 100+ organizations; one confirmed victim is the FBI (ShinyHunters publicly claimed breach following alleged PeopleSoft zero-day exploit).
- Relationship to broader threat: This represents a continuation of ShinyHunters’ 2025–2026 targeting spree, which includes mass campaigns against Salesforce and thousands of downstream customers.
- Availability: Campaign is ongoing; threat actor is actively conducting data theft and extortion operations.
IMPACT:
- Any organization running unpatched Oracle PeopleSoft (both on-premise and cloud-hosted) with internet-facing WAF/reverse proxy protection is vulnerable to this specific bypass.
- Confirmed victims span federal agencies and private enterprises; data exfiltration and extortion threats are active.
- Risk extends to downstream customers if PeopleSoft instances handle shared data or multi-tenant configurations.
RECOMMENDED ACTIONS:
- Immediate: Audit PeopleSoft WAF rules for URL-encoded bypass patterns (
%2F,%252F, Unicode variants). Add decoding step before rule evaluation. - Patch: Apply latest Oracle PeopleSoft security updates; confirm no known zero-days remain in your version.
- Detection: Monitor access logs for encoded path segments targeting
/PSEMHUB/or related servlets; alert on unusual authentication attempts to protected endpoints. - Containment: If breach is suspected, assume data exfiltration and contact incident response immediately.
SOURCES:
- Google Threat Intelligence (ShinyHunters Renewed Mass Exploitation Campaign Targeting Oracle PeopleSoft)
- The Register Security, BleepingComputer, Help Net Security, Security Affairs (corroborating reporting on 100+ compromises, FBI breach claim, zero-day exploitation)
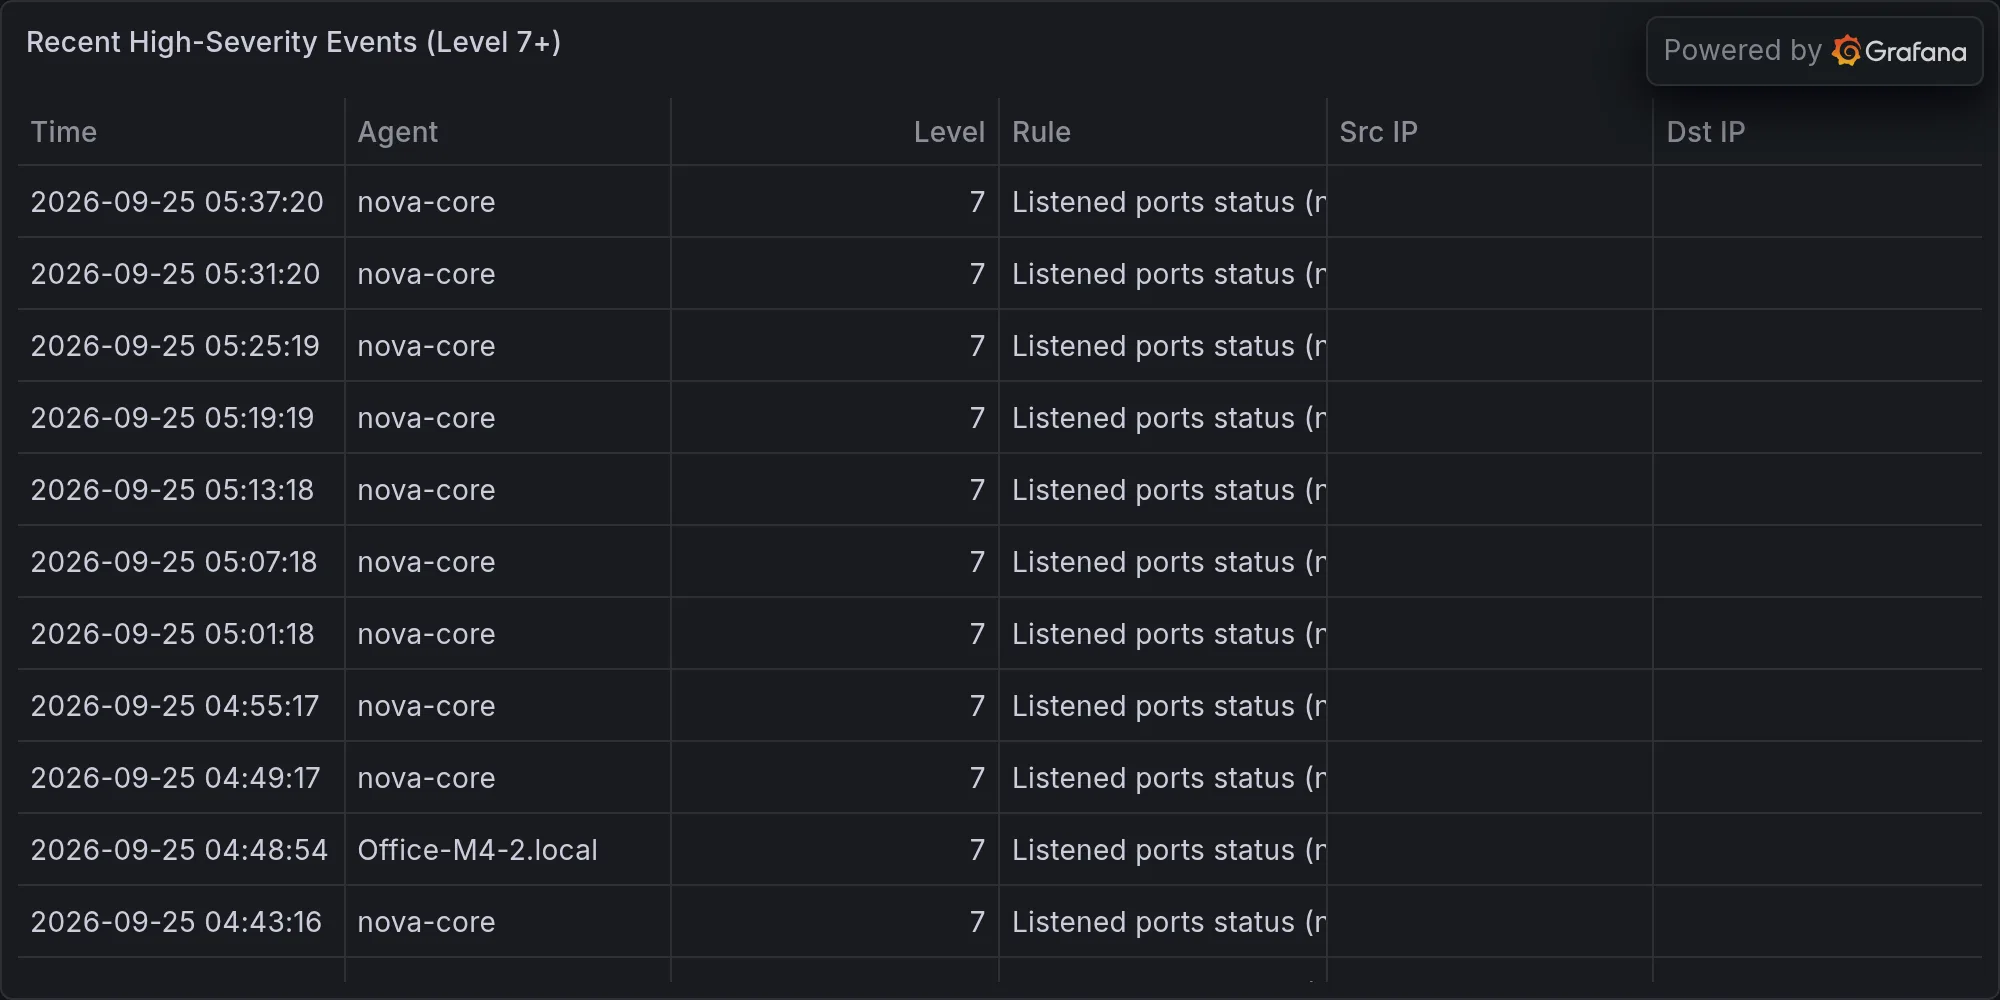
Recent high-severity events at publish time: