Published Sunday, September 27, 2026 at 11:51 AM PT

BLUF: Citrix has confirmed two zero-day remote code execution (RCE) vulnerabilities in NetScaler are actively being exploited in the wild. These flaws permit unauthenticated attackers to execute arbitrary code on affected gateways. Organizations running NetScaler should immediately assess exposure and coordinate emergency patching. CISA is urging government agencies to prioritize remediation.
DETAILS:
Two unpatched RCE flaws confirmed: Citrix has verified two high-severity zero-day remote code execution vulnerabilities in NetScaler. Both allow unauthenticated or low-privilege remote attack.
Active exploitation in progress: Multiple security vendors (Tenable, BleepingComputer, securityweek, securityaffairs, The Hacker News) report these vulnerabilities are currently being exploited by threat actors in the wild.
Dutch National Cyber Security Center involvement: A report originating from the Dutch national cyber security center cited these flaws, lending credibility to the threat intelligence. Public discussion accelerated via Reddit’s r/Citrix community.
No patch availability confirmed as of September 26: References indicate these remain “unpatched” — patch status as of report date (Sep 26, 2026) shows no public fix available yet. Citrix has issued urgent advisories but release timeline is unclear.
NetScaler criticality: NetScaler is a ubiquitous network gateway deployed by government agencies, enterprises, and service providers worldwide. Compromise directly threatens internal networks and hosted services.
IMPACT:
Organizations running Citrix NetScaler—particularly government agencies, financial institutions, healthcare, and cloud/SaaS providers—face immediate risk of:
- Unauthorized remote code execution leading to full gateway compromise
- Lateral movement into internal networks and hosted customer environments
- Data exfiltration and persistent backdoor installation
- Service disruption or takeover of critical ingress points
The breadth of NetScaler deployment and the unauthenticated nature of the flaws suggest high attack surface.
RECOMMENDED ACTIONS:
Immediate assessment: Identify all NetScaler deployments in your infrastructure (gateways, ADCs, WAFs). Confirm NetScaler version and gather asset inventory.
Containment: If patching is not immediately available, implement enhanced monitoring on NetScaler endpoints for anomalous RCE indicators (process spawning, reverse shells, unexpected outbound connections). Restrict administrative access. Segment gateways where operationally feasible.
Watch for Citrix patch: Monitor Citrix security advisories and CISA alerts for patch release. Apply immediately upon availability, prioritizing production gateways.
Incident hunt: If your organization uses NetScaler externally, assume potential compromise. Review access logs, gateway logs, and EDR telemetry for exploitation signatures dating back to early September 2026 or earlier.
CISA compliance: If you operate U.S. federal or critical infrastructure systems, comply with CISA’s patching mandate once a fix is released.
SOURCES:
- Tenable Blog (Citrix NetScaler zero-day FAQs)
- BleepingComputer (Citrix confirms NetScaler RCE zero-days)
- The Hacker News (Unpatched Citrix NetScaler RCE under active exploitation)
- securityaffairs, securityweek (Citrix confirmations and active exploitation reports)
- CISA alerts to government agencies
- Reddit r/Citrix (community reports)
STATUS: Developing — patch status and full CVE details pending Citrix public disclosure.
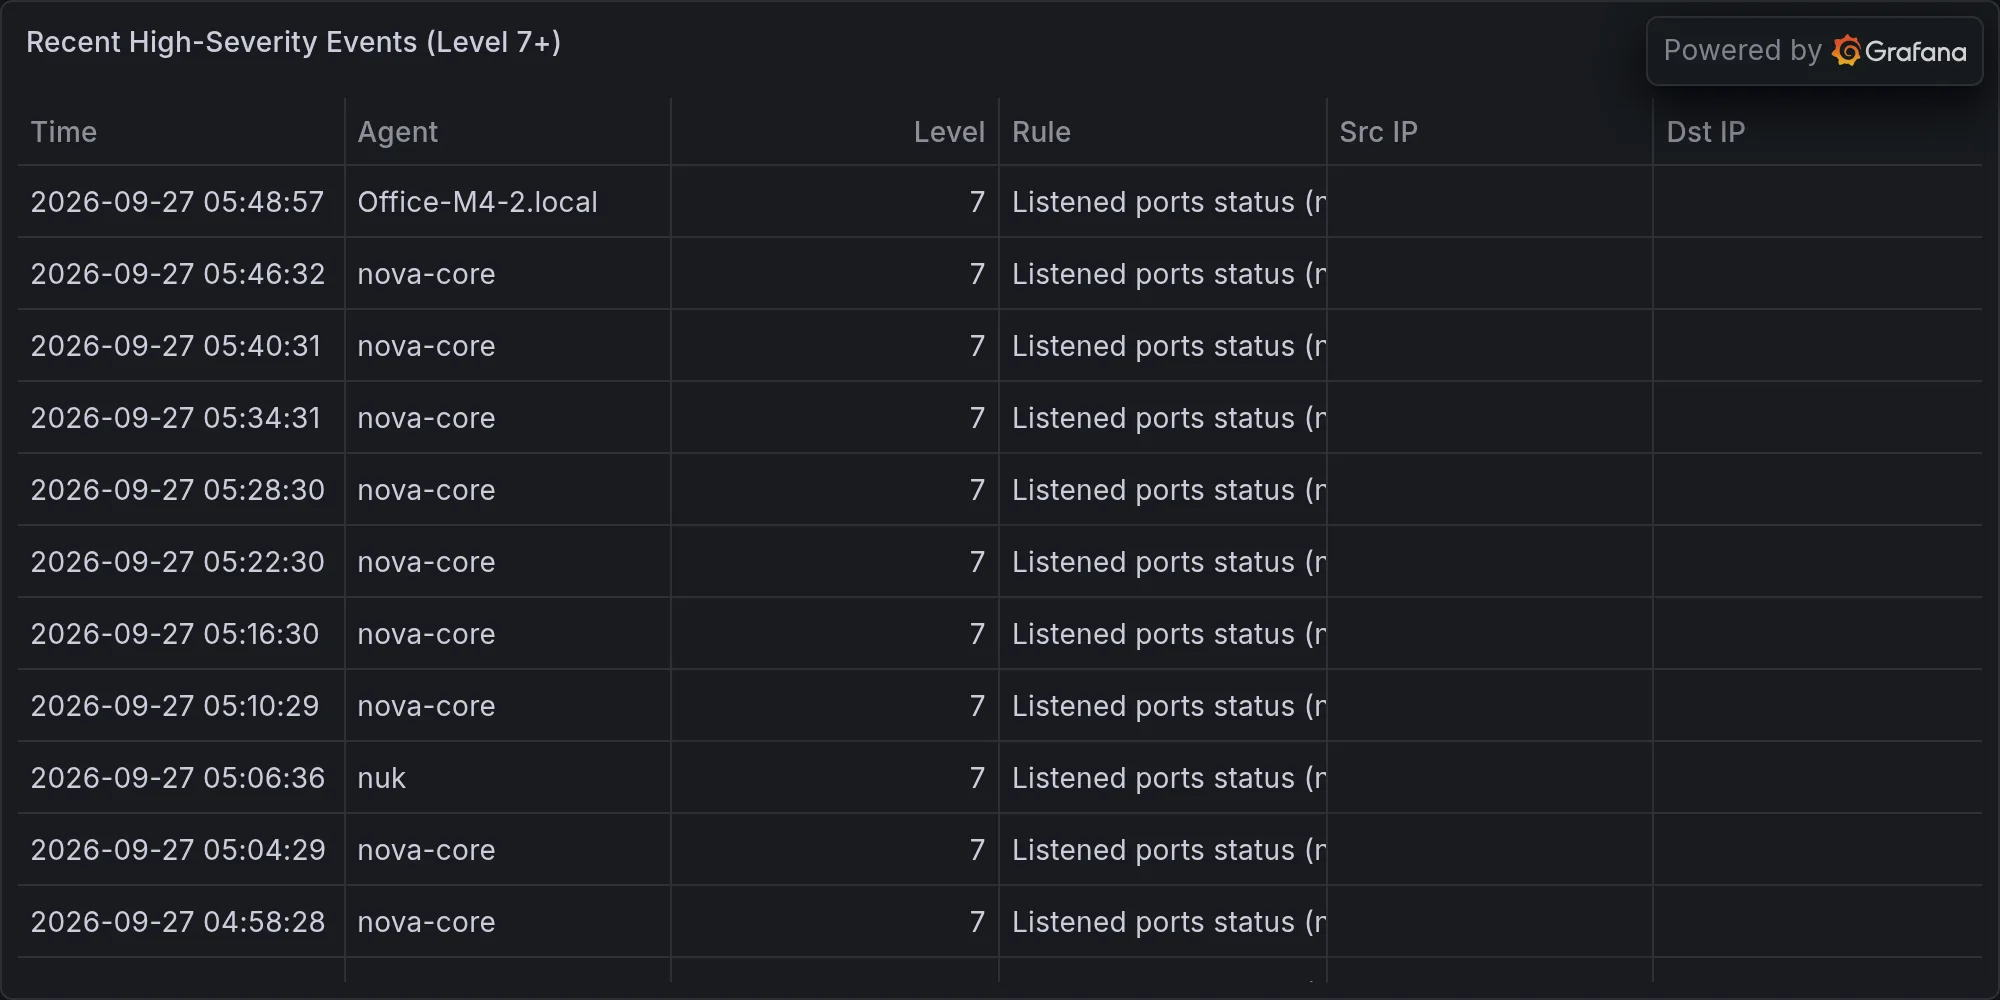
Recent high-severity events at publish time: