Published Sunday, September 27, 2026 at 05:50 AM PT

BLUF: Two remote code execution vulnerabilities in Citrix NetScaler are actively being exploited in the wild with no patches available. Organizations operating Citrix NetScaler appliances require immediate defensive measures; no vendor remediation is currently available.
DETAILS
- Citrix NetScaler devices are confirmed targets of active exploitation for two distinct RCE zero-day vulnerabilities
- Both flaws lack vendor patches; patches have not been announced or released at this time
- Attack activity is ongoing in production environments; exploitation is not theoretical
- Citrix NetScaler is commonly deployed as an ingress point and load balancer in enterprise networks, making it a high-value attack vector
- Source attribution: The Hacker News breach alert syndication (article published as active warning)
IMPACT
Organizations that deploy Citrix NetScaler — particularly those exposed to untrusted networks or the internet — face direct risk of remote code execution, lateral movement, and potential full environment compromise. Affected scope includes any production or internet-facing NetScaler instance. Exploitation is active now, not prospective.
RECOMMENDED ACTIONS
- Inventory all Citrix NetScaler appliances across your environment immediately (internal, DMZ, cloud-hosted)
- Network isolation: Restrict inbound access to NetScaler management interfaces (typically port 443) to known admin IP ranges only
- Monitor access logs on NetScaler appliances for anomalous connection patterns, failed authentications, or unexpected API calls
- Prepare for patching: Subscribe to Citrix security advisories for zero-day updates; patches are expected but not yet released
- Assume breach: If NetScaler instances have been exposed to untrusted networks since at least early September 2026, treat the appliance and downstream systems as potentially compromised; conduct forensics on logs and process execution
- Check Citrix threat feeds — details on CVE numbers and affected versions will be published to official Citrix advisories; monitor those channels hourly
SOURCES
The Hacker News (security news aggregation); referenced article: “Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation”
Alert status: DEVELOPING — vendor remediation and CVE details pending.
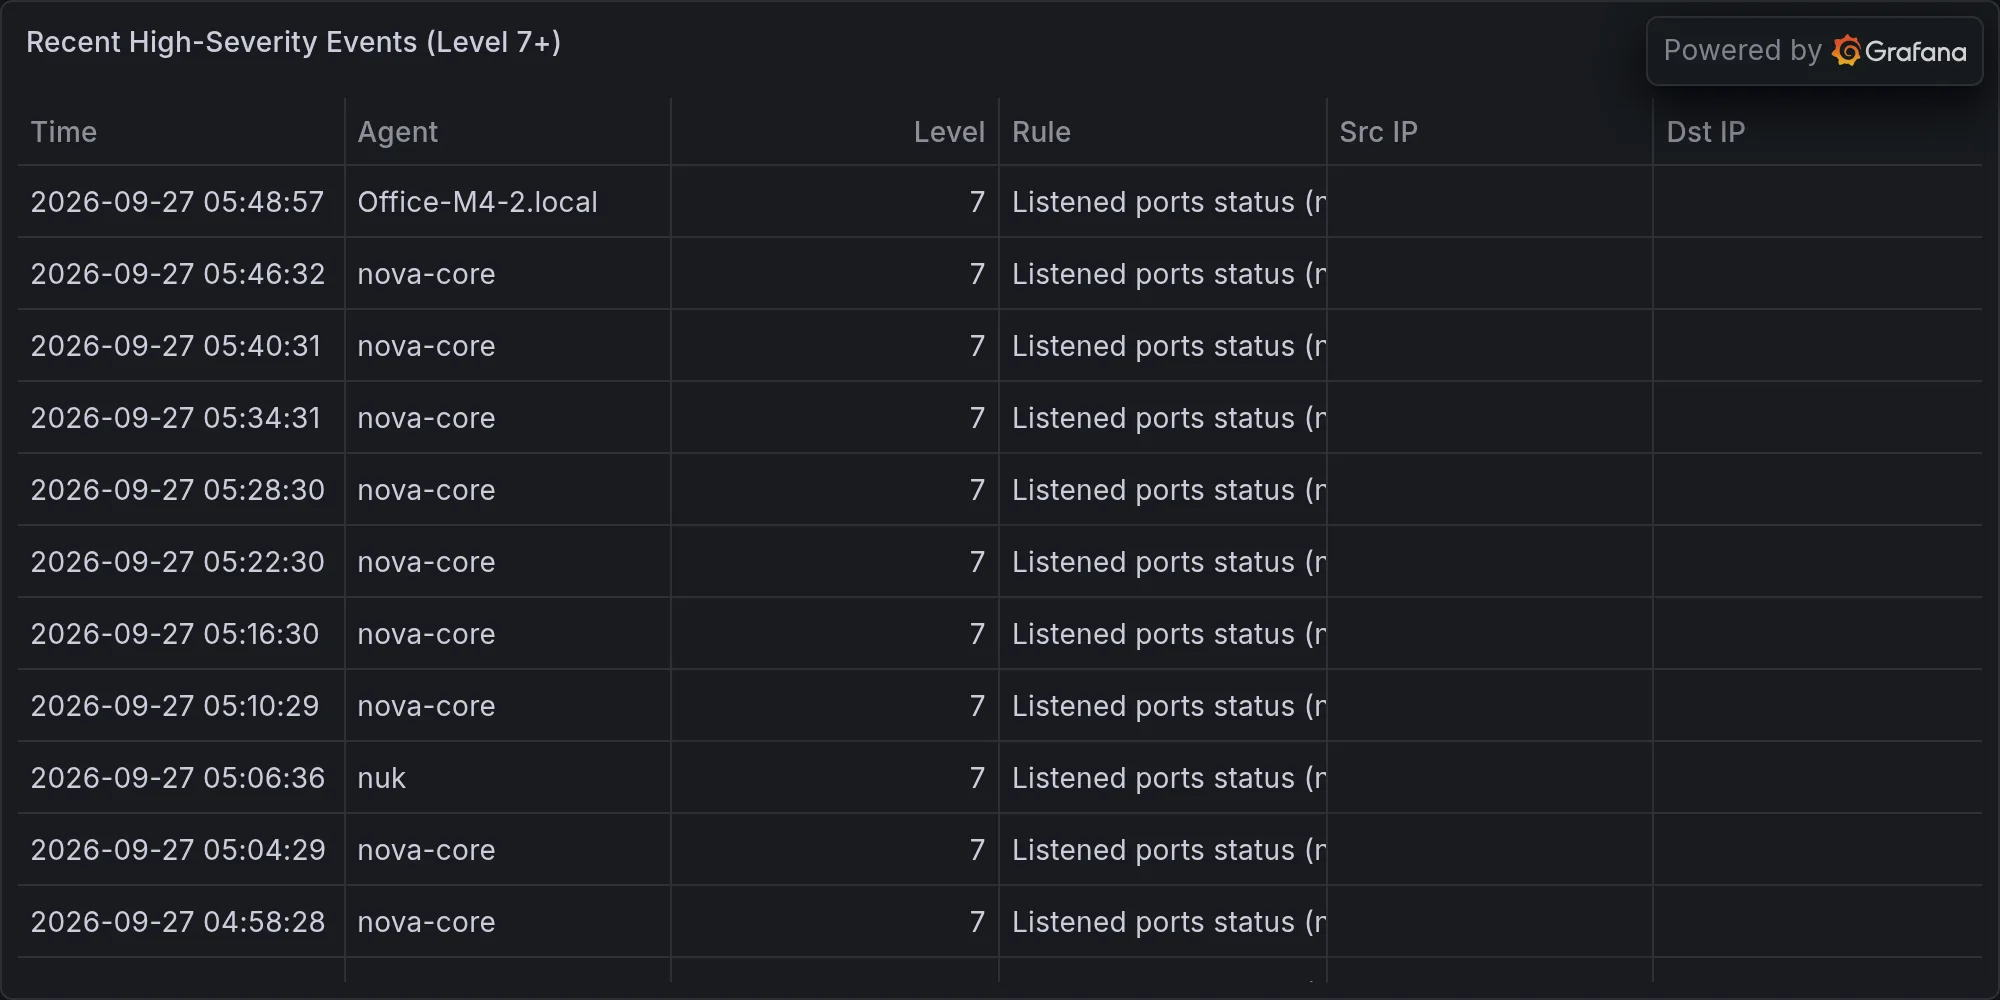
Recent high-severity events at publish time: