Published Sunday, September 27, 2026 at 05:54 PM PT

BLUF: Citrix NetScaler ADC and Gateway appliances are being actively exploited for multiple critical remote code execution (RCE) vulnerabilities. CISA has designated these as Known Exploited Vulnerabilities and is directing government agencies to patch immediately. Organizations running NetScaler in any capacity must assess exposure and apply fixes without delay.
DETAILS
- Active exploitation confirmed: Malicious actors are exploiting at least some of these vulnerabilities in the wild. This is not a theoretical threat.
- Multiple CVEs involved: CISA has incorporated at least six vulnerabilities related to NetScaler into its Known Exploited Vulnerabilities Catalog. CVE-2026-8452 (NetScaler RCE) has been exploited even after patches were released, indicating either incomplete fixes or rapid attacker adaptation.
- Remote code execution: Confirmed high-severity remote vulnerabilities affecting both ADC and Gateway products, enabling unauthenticated or low-privilege attackers to execute arbitrary code.
- Citrix verification: Citrix has confirmed and published advisories for the underlying flaws. Patches exist but urgency is critical given active exploitation.
- Government targeting: CISA specifically mandated federal agencies prioritize patching, suggesting intelligence that government networks are being scanned or targeted.
IMPACT
- Scope: Any organization running Citrix NetScaler ADC or Gateway (common in enterprise perimeter, VPN, and application delivery scenarios) is potentially affected.
- Exploitation risk: High. The combination of zero-day status at disclosure, active exploitation, and RCE capability means compromised NetScaler instances can serve as initial footholds for lateral movement into internal networks.
- Attack surface: NetScaler appliances often sit in DMZ or handle remote access — they are attractive targets for supply-chain and lateral-movement attacks.
RECOMMENDED ACTIONS
- Immediate inventory: Identify all Citrix NetScaler ADC and Gateway instances in your environment (including cloud deployments, remote access, and third-party managed instances).
- Check CISA advisories: Review Citrix’s official security advisories and CISA guidance at cisa.gov for patch availability and mitigation steps.
- Patch or isolate: Apply patches immediately if available. If patches are pending, isolate affected systems or restrict access to trusted networks only.
- Hunt for exploitation: If patching is delayed, search logs (NetScaler access logs, WAF logs, IDS/IPS) for exploitation attempts or suspicious access patterns from the timeframe these vulnerabilities were known.
- Network segmentation: Ensure NetScaler instances do not have unrestricted outbound access; limit lateral movement from compromised appliances.
SOURCES
- CISA Current Activity (ongoing advisories on critical NetScaler zero-days)
- Citrix security advisories (multiple CVEs, ADC and Gateway products)
- CISA Known Exploited Vulnerabilities Catalog (formal inclusion of six NetScaler CVEs)
- SecurityWeek, SecurityAffairs, News4Hackers reporting on in-the-wild exploitation
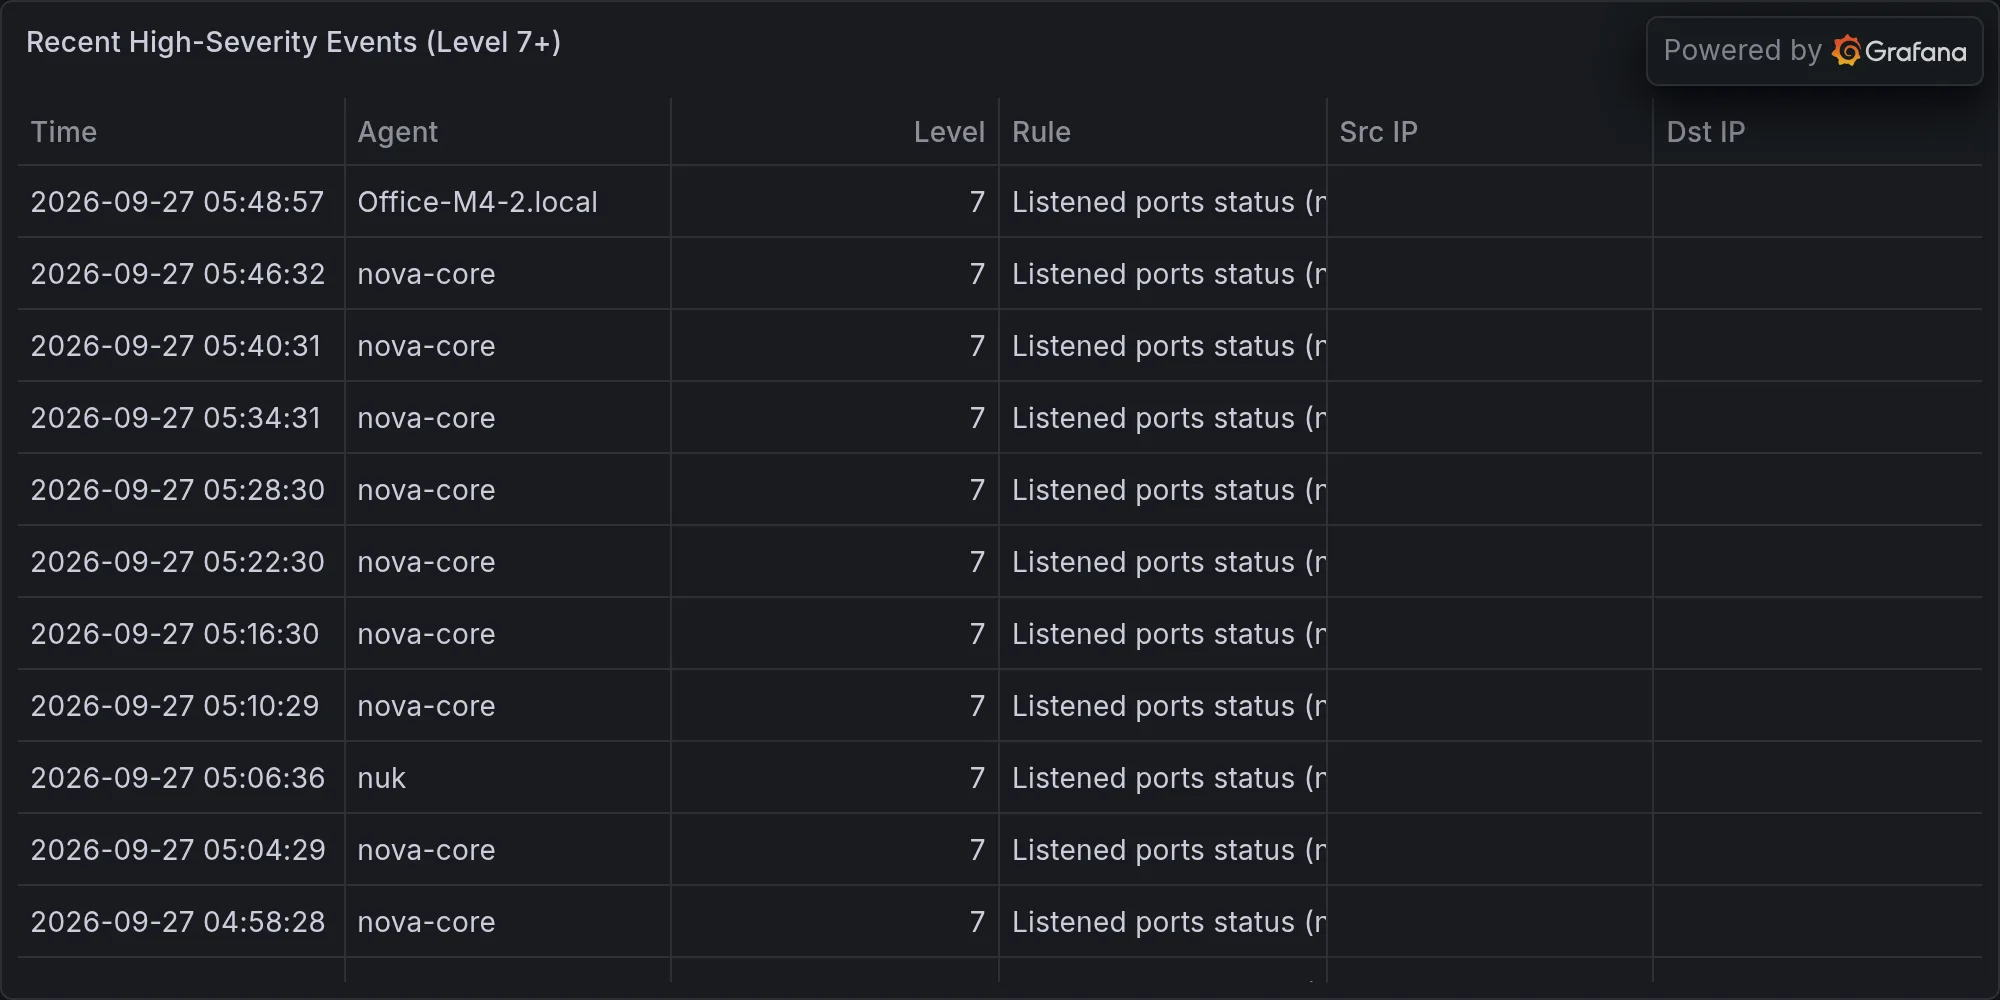
Recent high-severity events at publish time: