Published Monday, September 28, 2026 at 11:58 AM PT

BLUF — Two critical zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway (CVE-2026-88771 and CVE-2026-88772) are being actively exploited in real-world attacks. Citrix has released emergency patches. All organizations running affected NetScaler appliances must apply updates immediately; unpatched systems are under active targeting.
DETAILS
- Vulnerabilities: CVE-2026-88771 and CVE-2026-88772 are zero-day flaws in Citrix NetScaler ADC and NetScaler Gateway. Both carry critical severity ratings.
- Active Exploitation Confirmed: Citrix has confirmed that attackers are exploiting both vulnerabilities in the wild against production systems.
- Remediation Available: Emergency security patches have been released by Citrix; specific version numbers and affected versions not detailed in available source material.
- Attack Surface: NetScaler ADC and Gateway are internet-facing appliances commonly used for VPN, application delivery, and network security; compromise could grant attackers direct access to corporate networks.
- Timeline Uncertainty: Public disclosure date and patch availability timeline are not fully specified in source material; treat as urgent regardless.
IMPACT
- Affected Systems: All Citrix NetScaler ADC and NetScaler Gateway deployments (version ranges unconfirmed in available data).
- Risk Profile: Organizations with internet-exposed NetScaler instances are highest priority; active exploitation suggests attackers are conducting opportunistic scanning.
- Scope: Broad — NetScaler is deployed across financial services, healthcare, government, and enterprise sectors for secure remote access.
RECOMMENDED ACTIONS
- Immediate: Verify which Citrix NetScaler versions are deployed in your environment.
- Priority-1 Patching: Apply Citrix emergency security updates to all NetScaler ADC and Gateway appliances. Test in staging first if possible, but prioritize speed over extended QA given active exploitation.
- Network Monitoring: Enable logging/alerting on NetScaler instances for anomalous authentication, session creation, and administrative access.
- Interim Mitigation: If patching is delayed, consider restricting network access to NetScaler management interfaces and monitor for signs of compromise.
- Check for Breach Indicators: Review NetScaler logs for suspicious activity dating back 30–60 days; active exploitation may have begun before public disclosure.
SOURCES
- SOC Prime — CVE-2026-88771 and CVE-2026-88772 alert feed
- Citrix emergency security advisory (release details incomplete in source material provided)
Note: Full technical details (affected versions, CVSS scores, specific attack vectors) are incomplete in available source material. Treat as confirmed active exploitation requiring immediate action pending full advisory review.
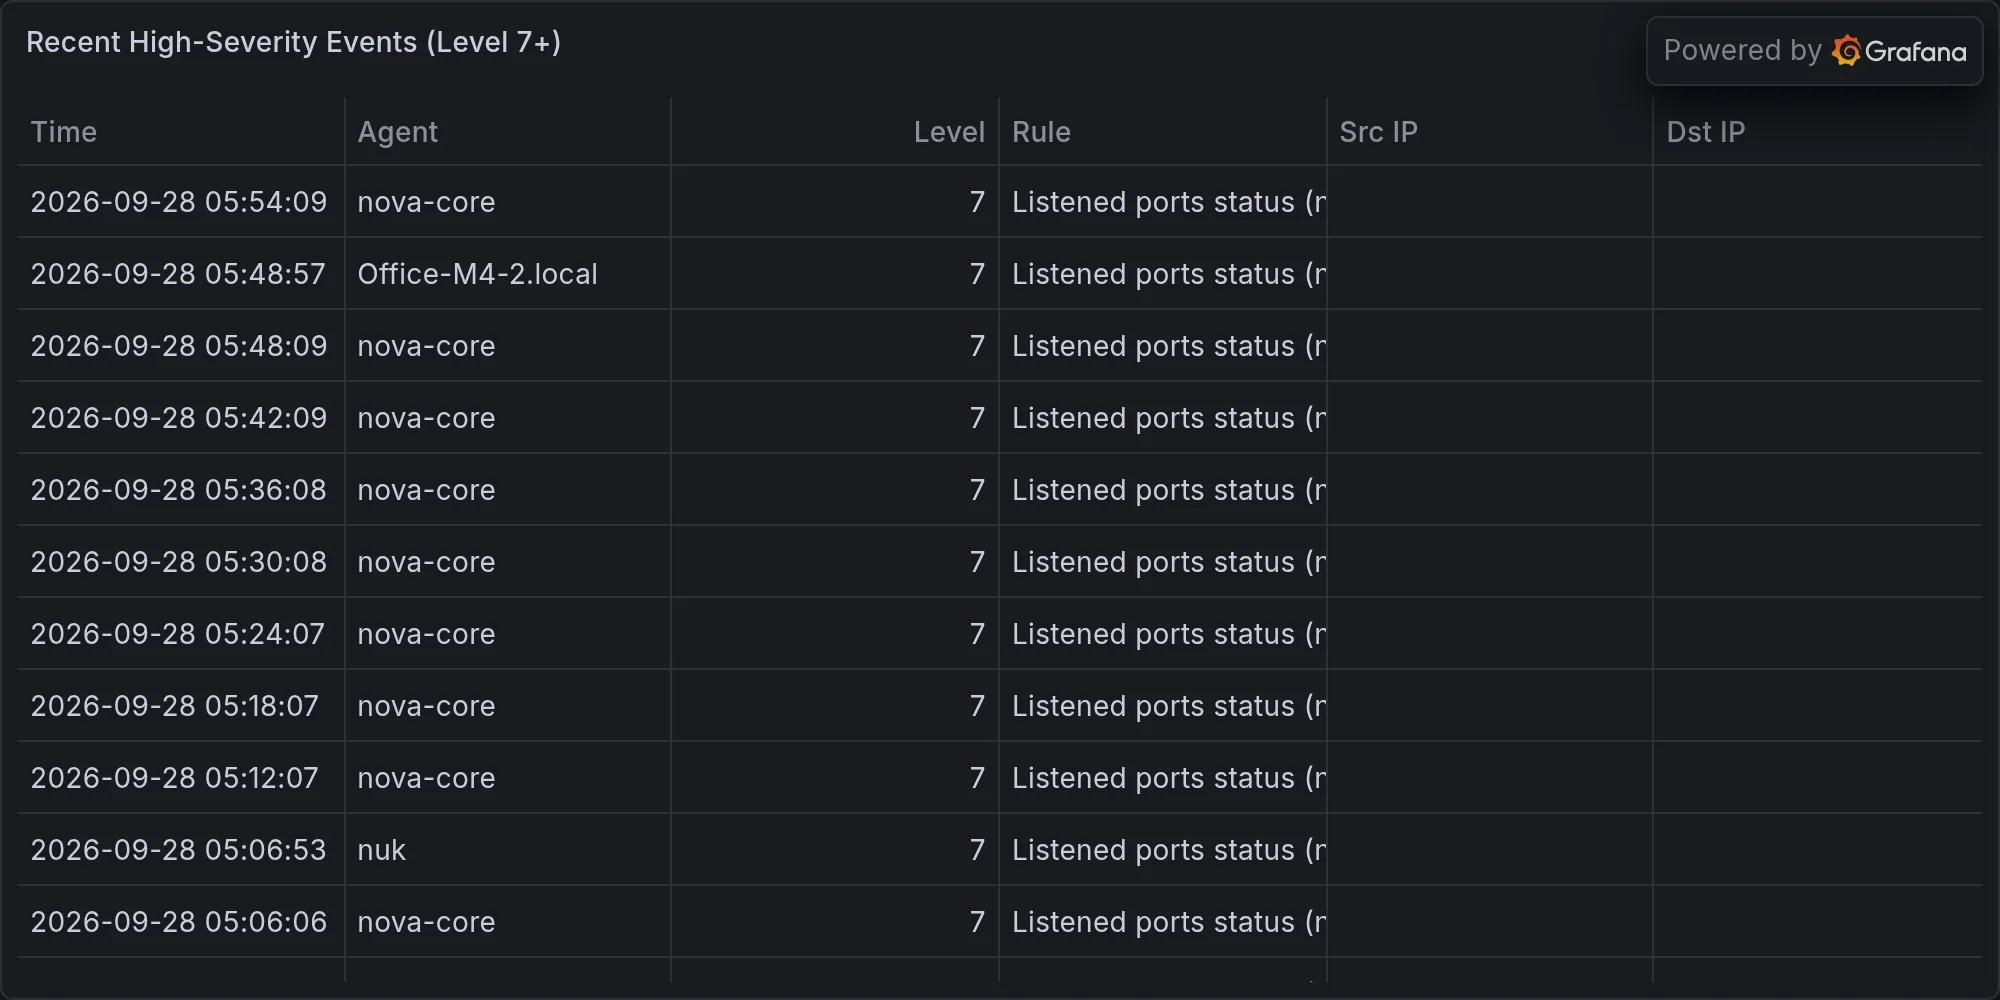
Recent high-severity events at publish time: