Published Monday, September 28, 2026 at 05:56 AM PT

BLUF: Rapid expansion of satellite communications infrastructure (18,000+ active satellites) is creating new attack surface for state-backed threat actors targeting IoT, utilities, and critical infrastructure. Telecom and OT sector already under active campaign pressure. Alert status: UNCONFIRMED EVENT — monitoring pattern. No specific recent incident confirmed; core threat is structural exposure.
DETAILS
- Satellite proliferation confirmed: 18,000+ active satellites now in orbit; expansion ongoing as commercial operators scale.
- Documented targeting landscape: Memory records active state-linked APT campaigns (China, Russia-linked) hitting telecom sector; Patchcord espionage campaign documented targeting telecom and critical infrastructure in South Asia.
- OT/IoT/IoMT exposure: Forescout reports partners facing growing security risks across IoT, operational technology (OT), and medical IoT (IoMT) — satellite-dependent systems increasingly in scope.
- Maritime sector already impacted: Documented cyberattacks on oil tankers putting maritime critical infrastructure at risk; shipping logistics depend heavily on satellite comms.
- State-backed focus on CI: FBI Cyber Strategy identifies state-backed actors explicitly targeting critical infrastructure; CIA Fortify guidance published for OT system protection, indicating defenders see active threat.
IMPACT
- Affected sectors: Utilities (grid, water), telecommunications, maritime, aviation, emergency response, IoT networks tied to critical services.
- Threat actors: State-backed APT groups with documented interest in energy, telecom, and OT infrastructure.
- Scope: Satellite-dependent communications now present in most critical infrastructure; expansion outpacing defensive maturity across SLTT governments and private operators.
RECOMMENDED ACTIONS
- Inventory satellite dependencies in operational technology and IoT networks supporting critical services.
- Harden OT/satellite interfaces: Segment satellite-dependent systems from primary networks; implement additional authentication and integrity checks.
- Monitor for Patchcord indicators: Recent South Asian espionage campaign evidence suggests active reconnaissance; review telecom supply chain logs.
- Engage CIS/OpenAI pilot: Agencies not yet participating in AI cyber defense pilots for critical infrastructure should prioritize enrollment.
- State CIOs: NASCIO alerts note cyber defense responsibility gap — assess satellite comms coverage in state emergency services and utility oversight.
SOURCES
- Industrial Cyber sector reporting (satellite comms exposure)
- CYFIRMA: Telecom sector APT campaign intelligence (China, Russia-linked)
- Acronis: Patchcord espionage campaign documentation
- Maritime incident reporting (satellite-dependent shipping attacks)
- FBI Cyber Strategy (state-backed CI targeting)
- NASCIO Critical Infrastructure Defense Alert
- CIS/OpenAI pilot announcement
STATUS: This is pattern-based alert from multiple confirmed sources. Core trigger data truncated in feed; no single recent incident pinpointed. Treat as heightened baseline — not immediate incident response. Continue monitoring telecom and OT sectors for specific exploitation events.
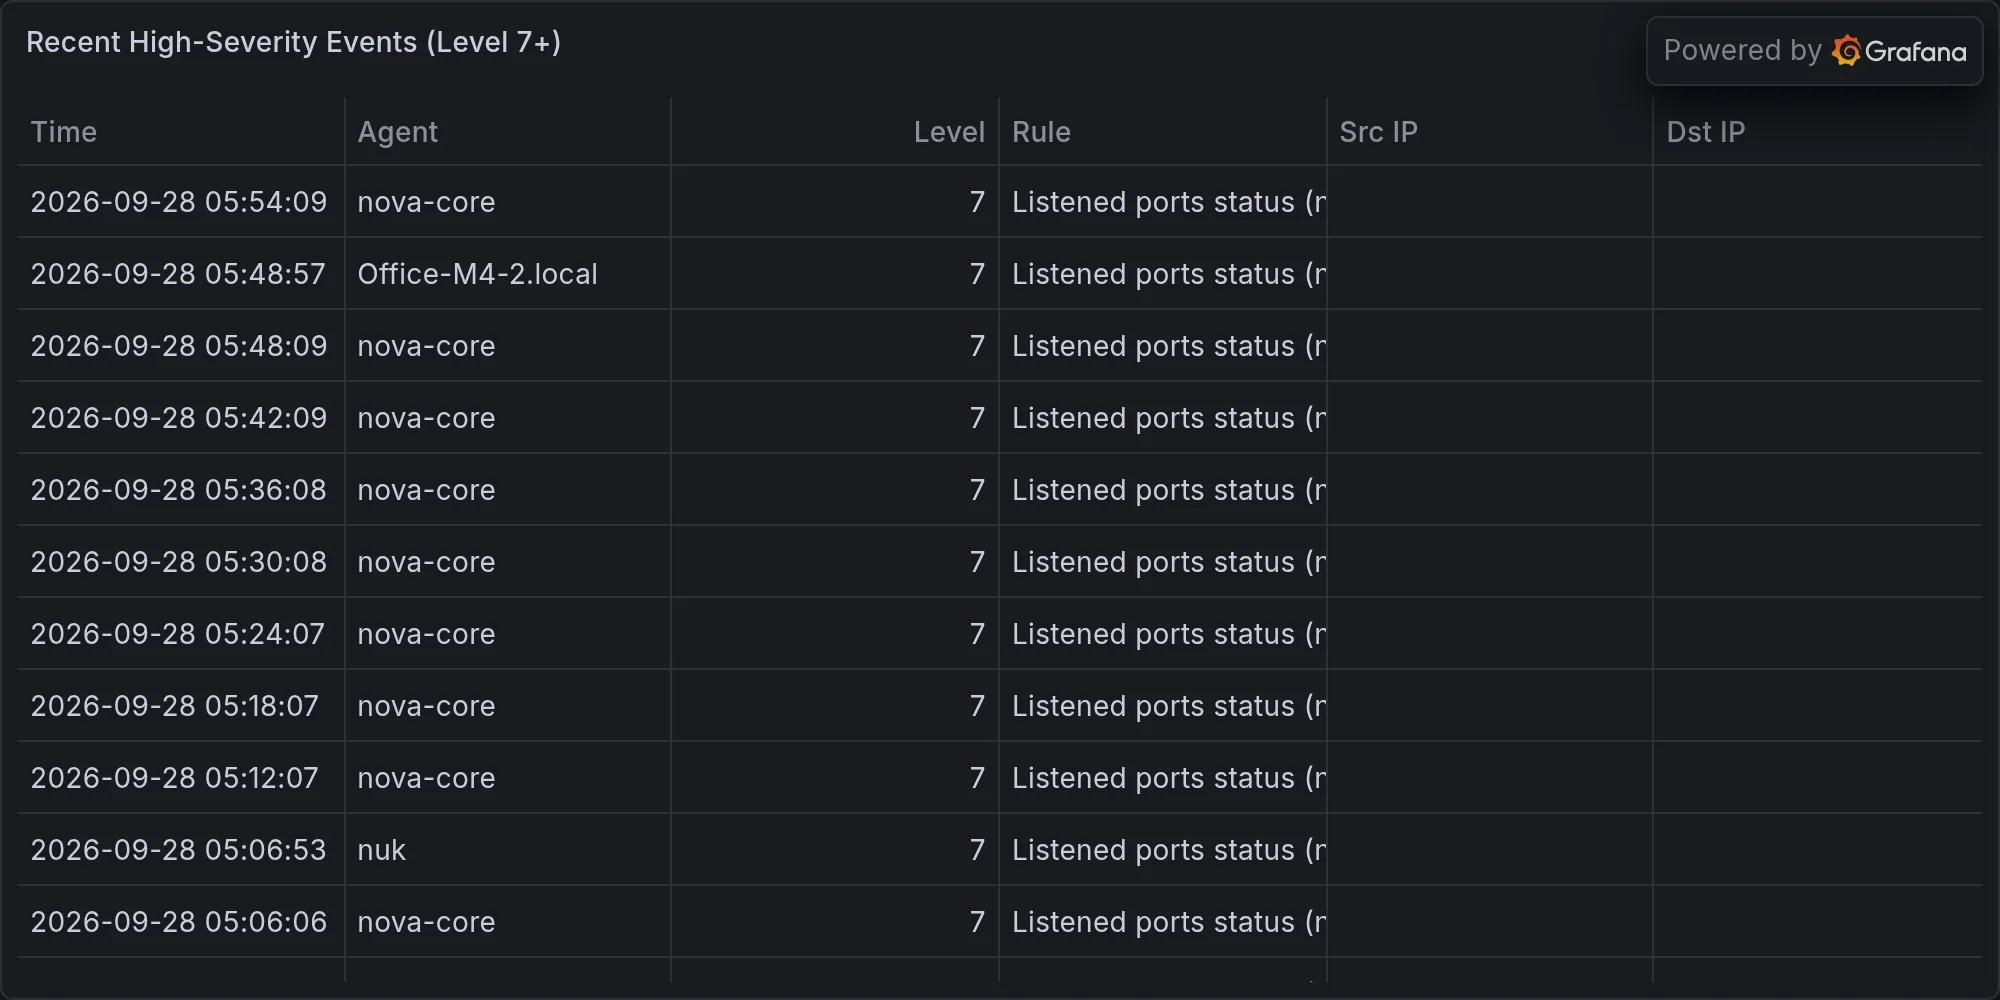
Recent high-severity events at publish time: