Published Tuesday, September 29, 2026 at 06:04 AM PT

BLUF: Apple released patches for CVE-2026-86950, a critical zero-day in Core Graphics that was actively exploited in highly sophisticated targeted attacks. Patch immediately; affected systems at risk for privilege escalation.
DETAILS:
- CVE-2026-86950 — Critical flaw in Apple Core Graphics framework; zero-day confirmed exploited in the wild before disclosure
- Reported by Meta — Attack infrastructure assessed as “extremely sophisticated”; targeting scope and victim count not yet public
- Affected: Core Graphics is foundational to macOS, iOS, iPadOS, watchOS rendering; all recent versions presumed vulnerable pre-patch
- Attack chain: Unknown from available sources; potential for arbitrary code execution within CoreGraphics privilege context
- Patch availability: Apple released fixes; specific build versions/release dates not confirmed from available intelligence
IMPACT: Any unpatched Apple OS (macOS, iOS, iPadOS) running vulnerable CoreGraphics versions remains exploitable. Core Graphics handles all on-screen rendering — successful exploitation likely permits kernel-level code execution. The “extremely sophisticated” assessment indicates advanced attacker group (nation-state or premier private sector APT). Active exploitation window spans at least 2026-09 (patched now, but prior attack window unknown).
RECOMMENDED ACTIONS:
- Prioritize CVE-2026-86950 patches for all macOS and iOS devices in your fleet
- If systems were online during active exploitation window (pre-patch): escalate for forensic review — assume compromise until proven otherwise
- Monitor Core Graphics logs and process anomalies — malware leveraging this vector post-patch will be readily anomalous
SOURCES: news4hackers, BleepingComputer, Help Net Security, SecurityWeek, Zero Day Initiative (September 2026 review)
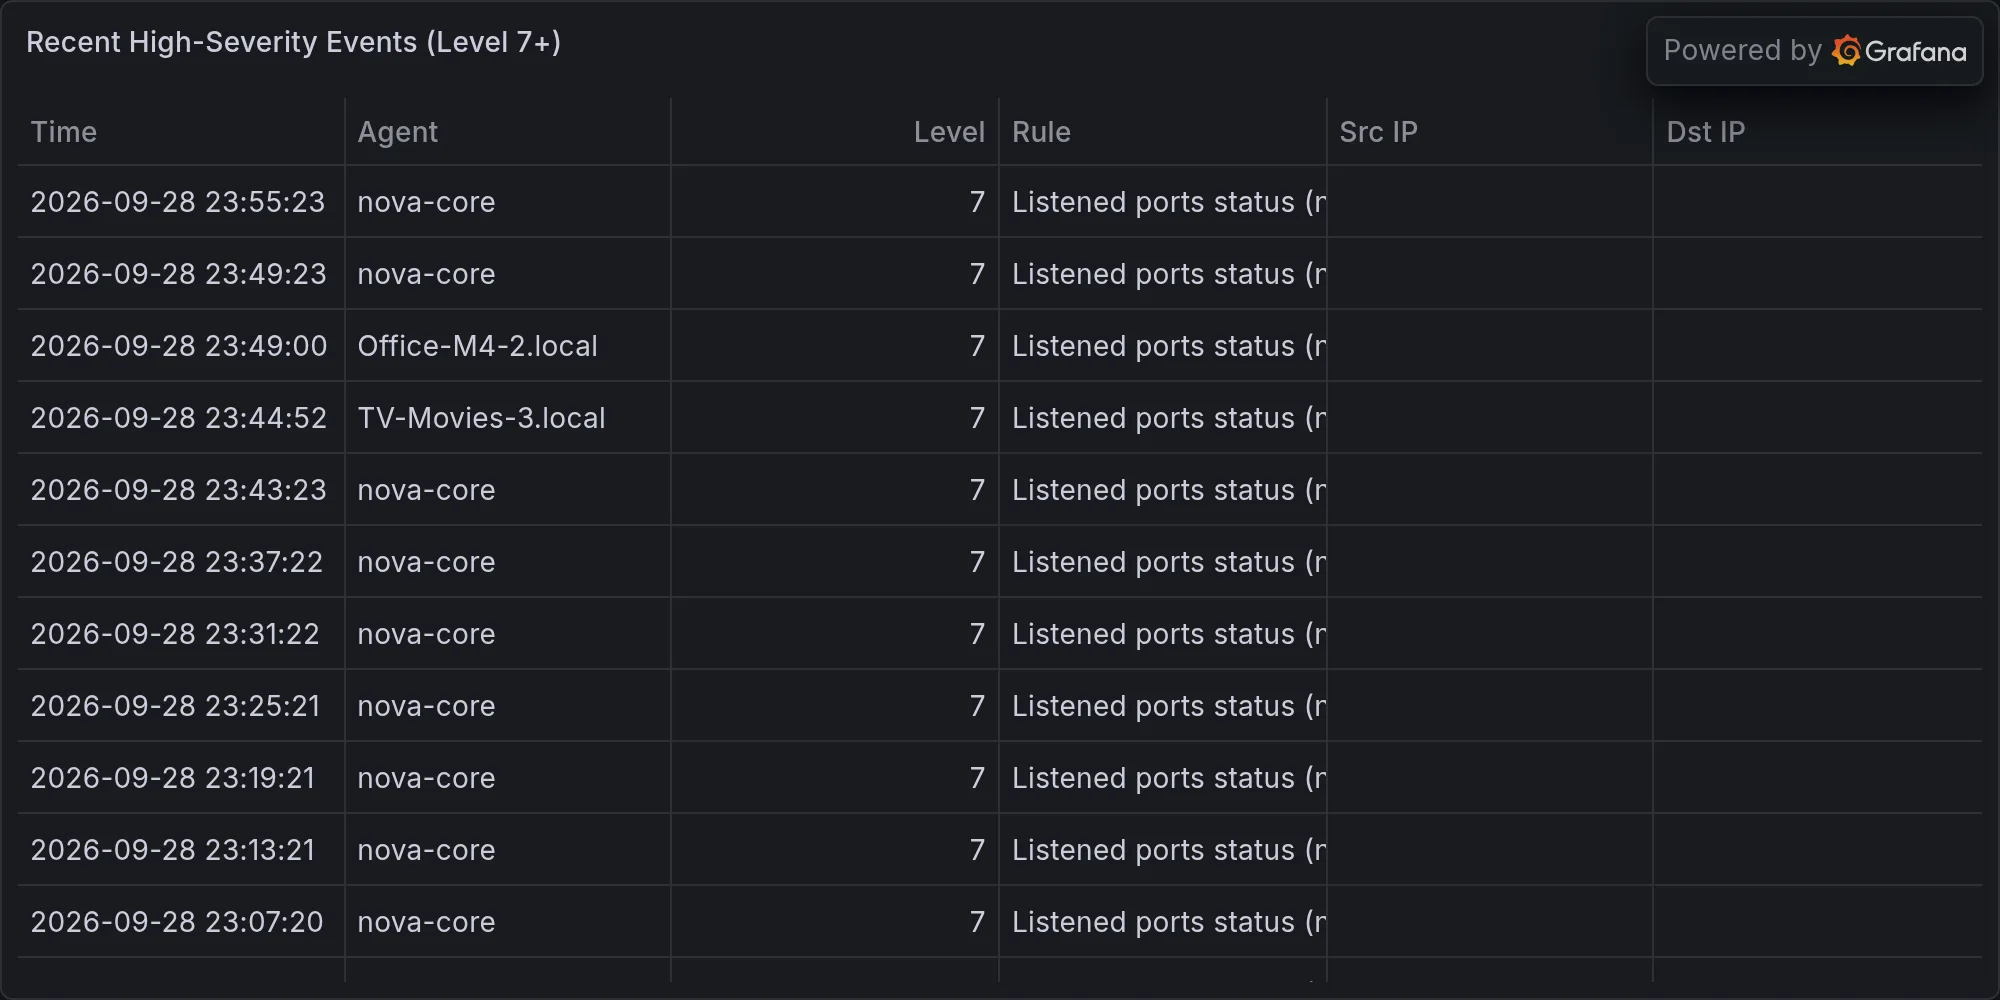
Recent high-severity events at publish time: