Published Tuesday, September 29, 2026 at 05:39 PM PT

BLUF
Attackers are exploiting unpatched remote code execution (RCE) vulnerabilities in Citrix NetScaler (CVE-2026-88771, CVE-2026-88772) to deploy web shells across the internet. Attacks have been active for at least three weeks. Organizations using NetScaler should assume compromise if unpatched and immediately engage incident response.
DETAILS
- Citrix confirmed two high-severity NetScaler RCE zero-days are being exploited in active attacks globally
- Malicious actors deploy web shells post-exploitation, enabling persistent backdoor access and lateral movement
- Exploitation has occurred undetected for at least three weeks, suggesting widespread compromise before public disclosure
- GreyNoise telemetry confirms mass/swarming attack activity (149+ probe attempts from single IP: 149.104.78.141 on 24 September 2026)
- Vulnerabilities remain unpatched as of this alert date; no vendor patch timeline confirmed in provided material
IMPACT Any organization running unpatched Citrix NetScaler appliances (commonly used as gateway/VPN endpoints) is likely compromised. Affected systems provide attackers direct access to internal networks, credential theft opportunities, and lateral movement vectors. Defense contractors have been targeted; global scope confirmed.
RECOMMENDED ACTIONS
- Immediate: Scan NetScaler audit logs for unexpected web shell upload patterns, reverse shells, or administrative account creation (past 3+ weeks)
- Isolate unpatched NetScaler instances from the internet pending patch availability
- Force password reset for all accounts with NetScaler access
- Engage incident response if your organization operates NetScaler in production
SOURCES
BleepingComputer, CyberScoop (Mandiant), Help Net Security, The Hacker News, GreyNoise Intelligence, news4hackers
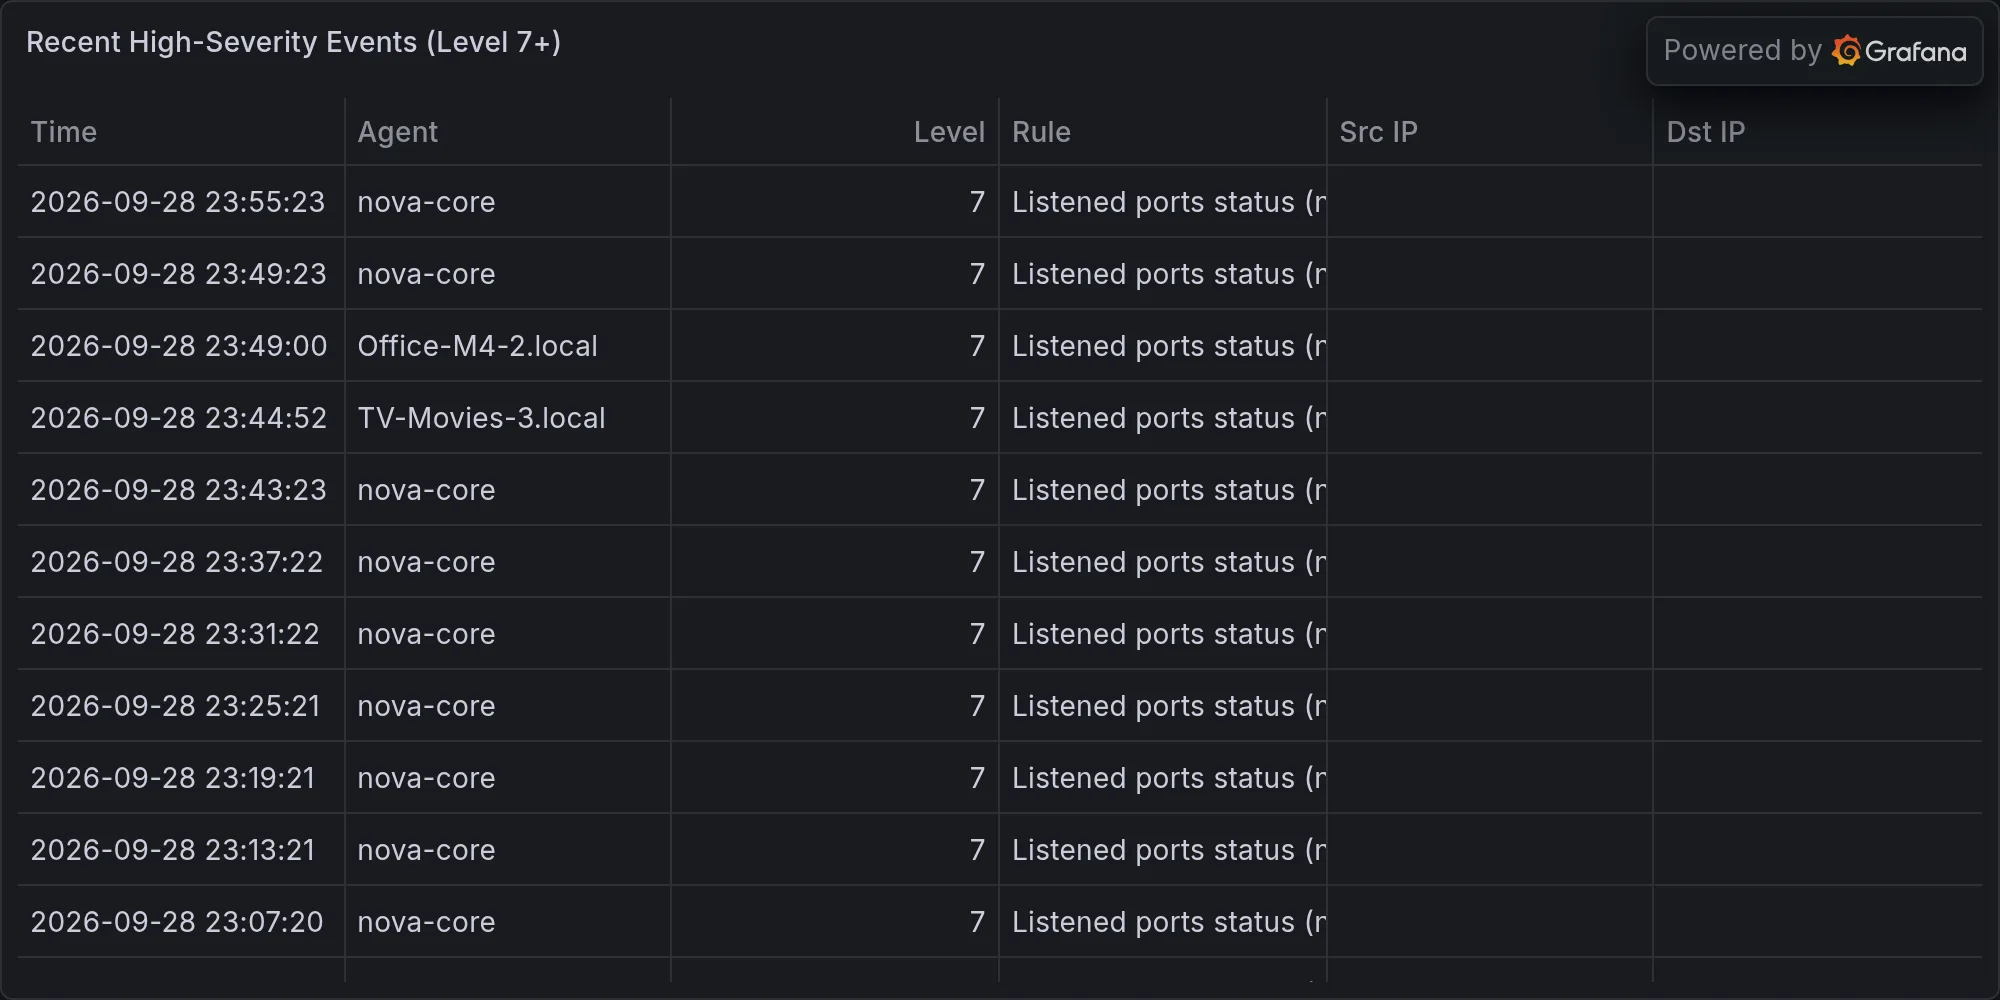
Recent high-severity events at publish time: