Published Tuesday, September 29, 2026 at 12:08 PM PT
BLUF: Apple has released emergency security updates for CoreGraphics vulnerability CVE-2026-86950, an out-of-bounds write flaw enabling arbitrary code execution. Active exploitation reported against specific high-value targets. Patch availability and affected macOS/iOS versions not confirmed in available intel — immediate patch verification required for all Apple devices.
DETAILS:
- Vulnerability: Out-of-bounds write in Apple CoreGraphics library; triggers arbitrary code execution when processing malformed graphical content
- Exploitation status: Highly targeted attacks confirmed; likely in-the-wild use against individuals of interest; not widespread commodity malware
- Remediation: Apple has issued emergency updates; specific version/platform scope UNCONFIRMED in provided intel
- Attack vector: Malformed graphical input (likely via web content, documents, or media); details on delivery method not available
- Severity implication: CVSS and full technical details truncated in source material — treat as critical pending official CVE scoring
IMPACT:
- Who: Apple device users globally; highest risk to individuals in known targeting categories (journalists, activists, government officials, executives)
- What: Complete device compromise possible; remote code execution as userland or system context (sandbox bypass not yet confirmed)
- Scope: Affects macOS and iOS versions running vulnerable CoreGraphics library; exact version range not specified in available material
RECOMMENDED ACTIONS:
- Immediate: Check Apple Security Updates for CVE-2026-86950 release details (version numbers, affected products) — enforce full patch deployment across all endpoints
- Device inventory: Identify high-value / high-risk users (those matching known APT targeting profiles); prioritize their patching
- Detection: Monitor for suspicious CoreGraphics crashes, memory access violations, or unexpected process spawning from Adobe/image viewers and browsers
- Threat hunt: If targeting threat actor is identified, check logs for GraphQL/image parsing anomalies in the past 90 days
- Comms: Notify users this is targeted, not mass-exploitation — reduces false-alarm alert fatigue but ensures compliance teams patch
UNCONFIRMED — FLAGGED GAPS:
- Affected OS versions, build numbers, and patch availability details not in source material
- Whether iOS/iPadOS/watchOS affected alongside macOS
- Known exploitation timeline (how long exploited before discovery)
- Threat actor attribution
- Full CVE write-up and PoC availability
SOURCES:
- SOC Prime threat intelligence feed
Alert timestamp: 2026-09-29
Status: DEVELOPING — awaiting full CVE NVD record and Apple Security Advisories for patch scope/versions
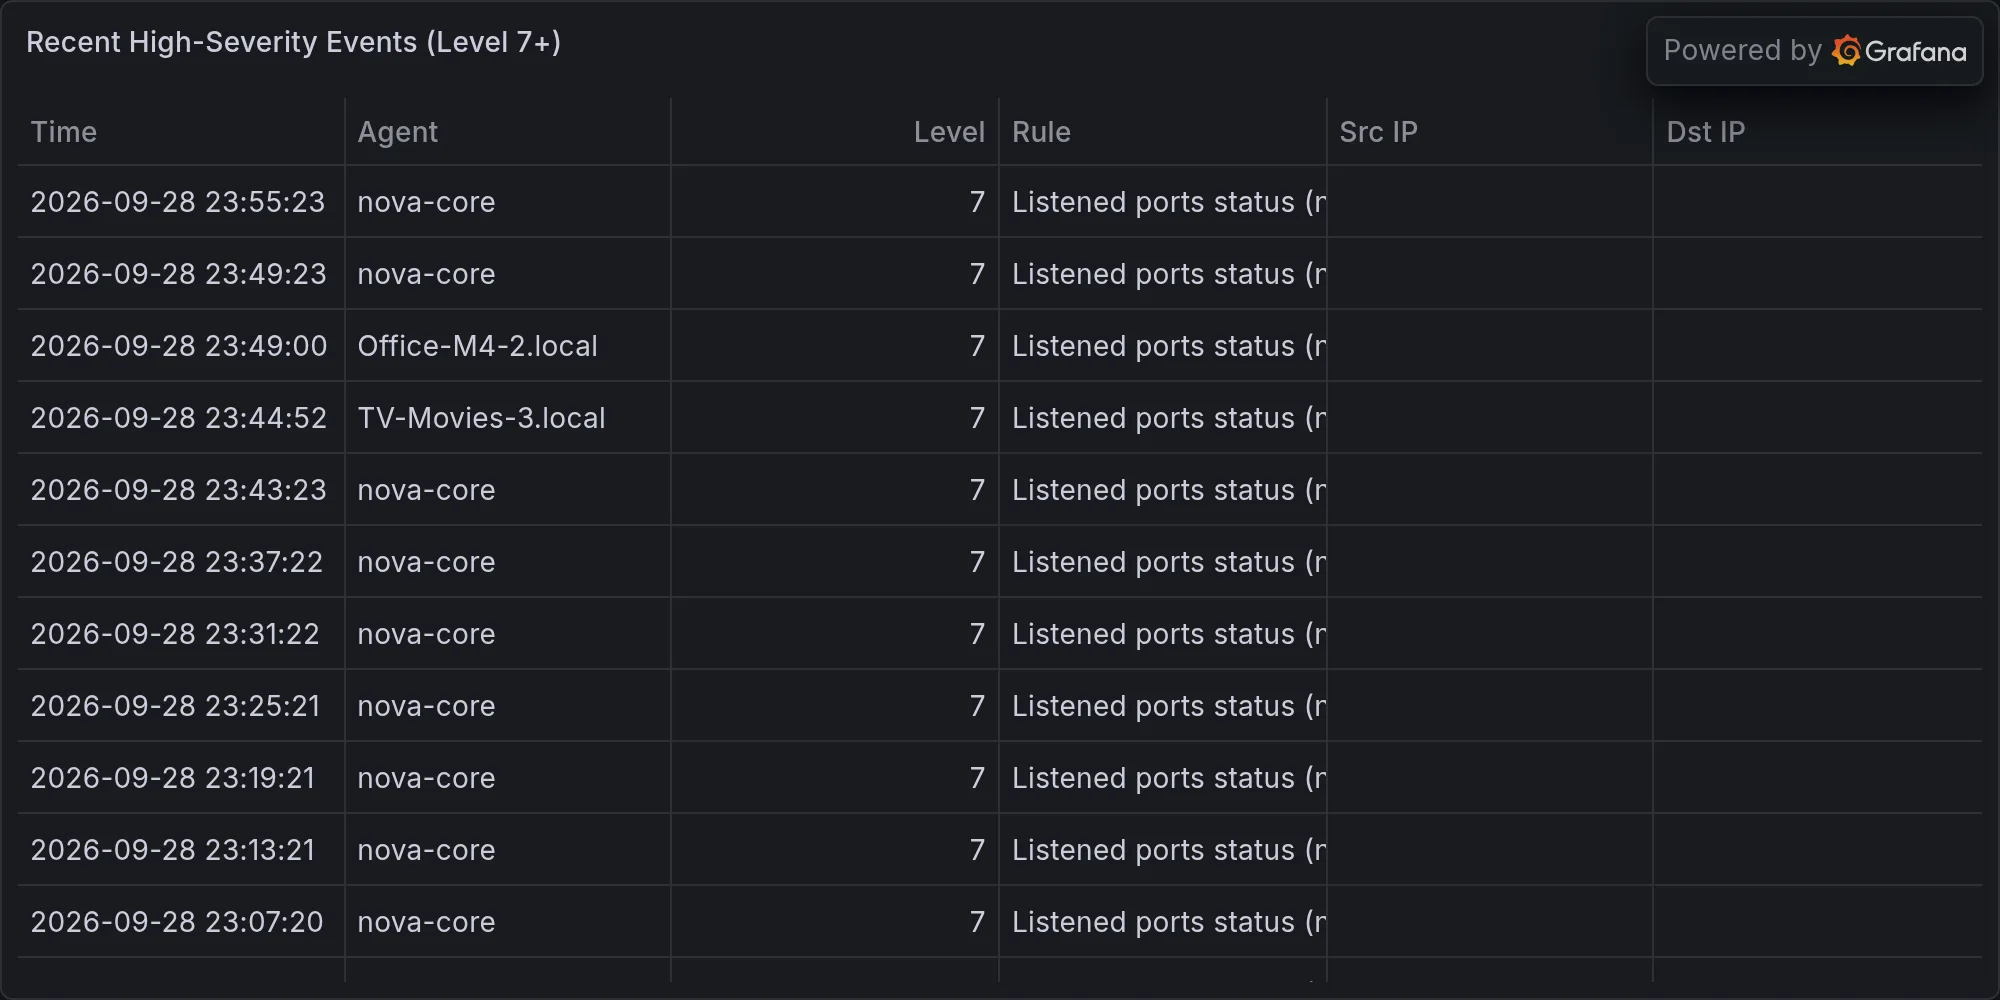
Recent high-severity events at publish time: