Published Tuesday, September 29, 2026 at 05:38 PM PT

BLUF: Two critical remote-code-execution zero-days in Citrix NetScaler ADC and Gateway have been exploited in the wild for at least three weeks by advanced, suspected state-sponsored threat actors. Mandiant confirms dozens of organizations compromised. Patch immediately and assume breach until verified otherwise.
DETAILS:
- Two CVEs active: CVE-2026-88771 and CVE-2026-88772 (both RCE, high severity). Citrix released patches after the exploitation window was already public; patches are now available.
- Duration: Minimum three weeks of undetected exploitation. Attack start date prior to 2026-09-24 (GreyNoise sighting of malicious actor IP 149.104.78.141 on that date).
- Scale & sophistication: Dozens of organizations across global scope. Mandiant and Blue team (GreyNoise) confirm advanced tactics and state-sponsored attribution.
- Affected products: NetScaler ADC and NetScaler Gateway — widely deployed as perimeter security / VPN gateways in enterprise environments.
- Attack capability: Unauthenticated remote code execution → full system compromise, lateral movement, data exfiltration.
IMPACT:
- Any organization running unpatched Citrix NetScaler ADC or Gateway is potentially compromised.
- RCE severity means attackers can install persistent backdoors, steal credentials, move laterally to internal systems.
- Three-week blind spot means compromise detection requires forensic log analysis (if logs were retained); many organizations may not discover intrusion for months.
- Threat actor profile (state-sponsored) suggests this was targeted espionage, not mass-scan exploitation.
RECOMMENDED ACTIONS:
- Patch immediately — Apply Citrix security updates for CVE-2026-88771 and CVE-2026-88772 to all NetScaler ADC and Gateway instances today. Do not wait for change windows.
- Assume breach — Treat all unpatched NetScaler systems as compromised until forensic review confirms otherwise. Pull NetScaler log data (authentication, command execution, network traffic) for the three-week window and later if available.
- Review indicators — Hunt for 149.104.78.141 and related IOCs in firewall/proxy logs; correlate with NetScaler access logs for the exploitation window (early September onwards).
- Credential rotation — Rotate all credentials cached by, or harvested through, compromised NetScaler instances (VPN user accounts, admin accounts, API tokens).
- Monitor for persistence — Watch for unexpected outbound connections, scheduled tasks, or persistent processes on internal systems post-compromise.
SOURCES:
Mandiant (via CyberScoop), Citrix official advisory, BleepingComputer, Help Net Security, GreyNoise Blue Team, The Hacker News, SOC Prime, CyberScoop follow-up.
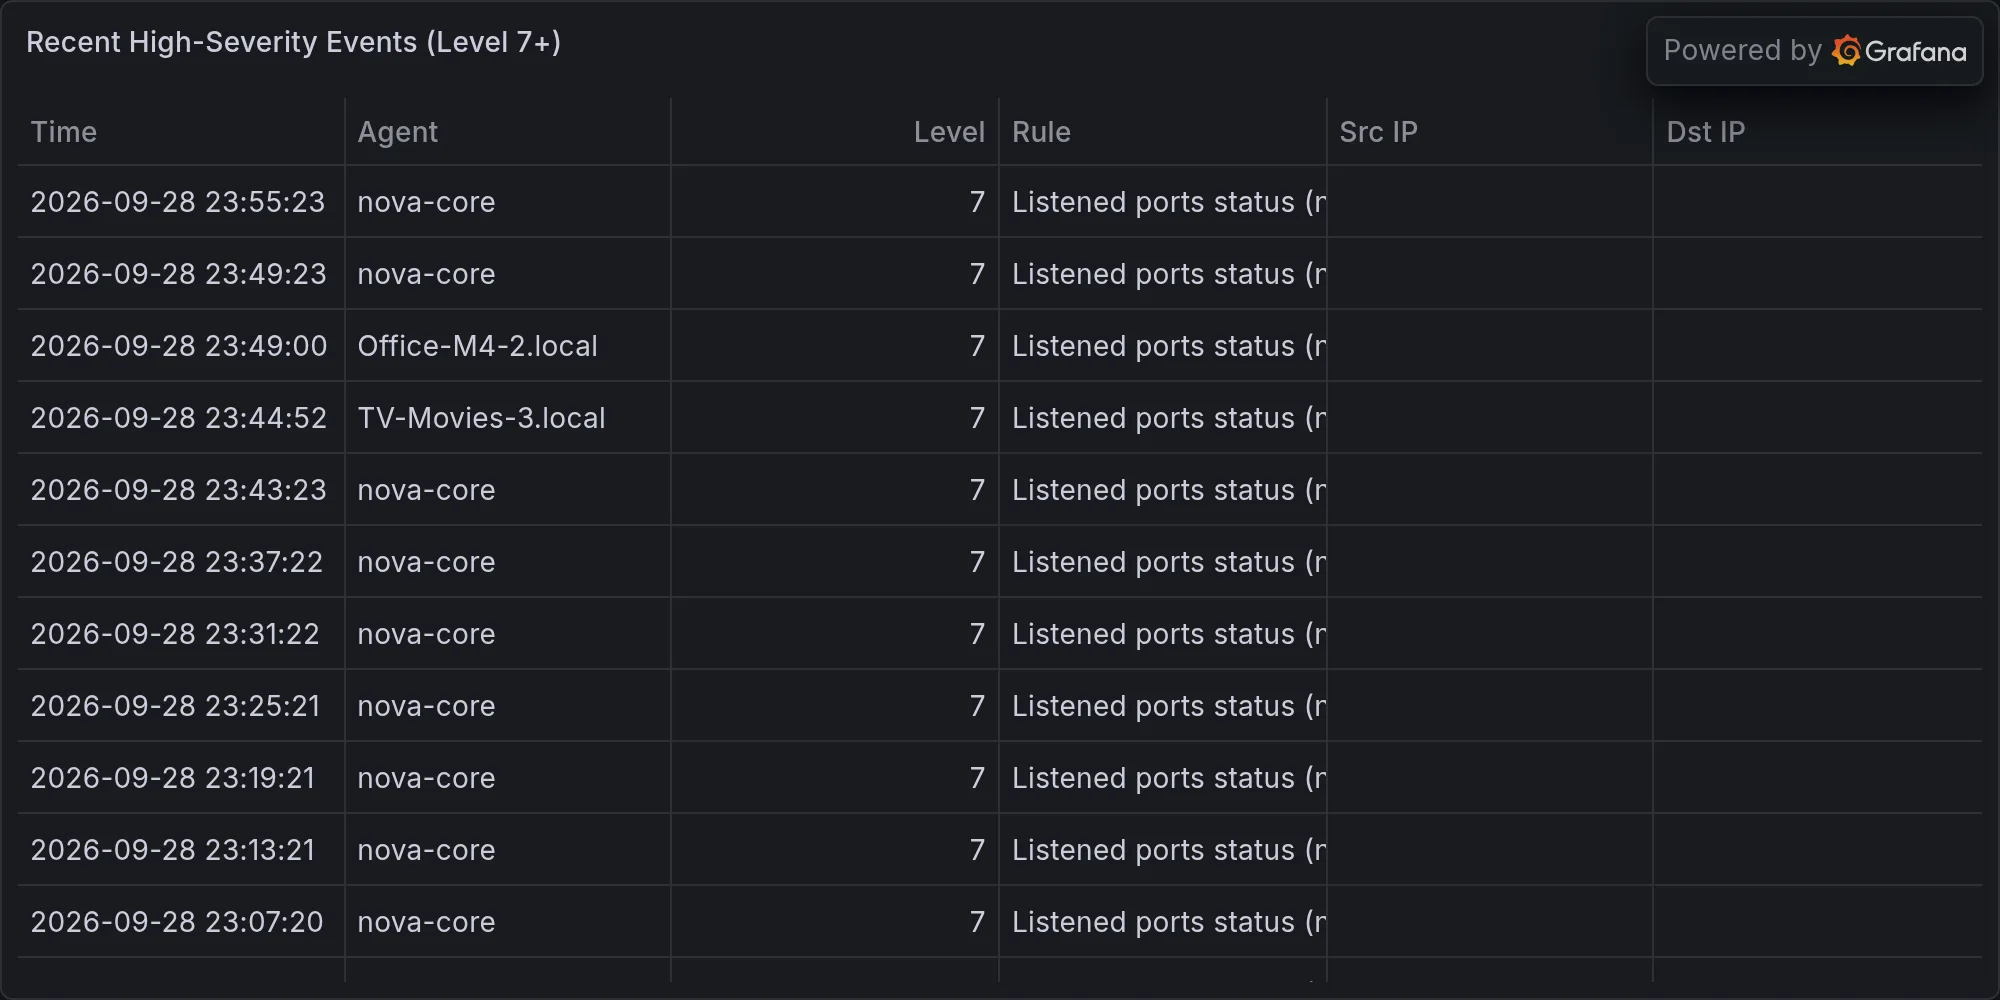
Recent high-severity events at publish time: