Published Tuesday, September 29, 2026 at 06:03 AM PT

BLUF: Apple has released security patches addressing a zero-day vulnerability in CoreGraphics that is actively being exploited in targeted attacks. Scope, affected versions, and attack surface not yet specified; immediate advisories issued but detailed CVE data still emerging.
DETAILS:
- Apple shipped patches for a zero-day flaw in CoreGraphics in response to active exploitation in the wild
- Attack context indicates targeted activity, not mass exploitation
- CVE-2026-86950 is associated with the patch release (per news4hackers context) — formal NVD / Apple advisory details not yet populated in provided material
- Exploitation vector and affected product versions are unconfirmed from available sources
IMPACT:
- macOS, iOS, and/or iPadOS systems running vulnerable CoreGraphics versions are likely at risk
- Targeted users/organizations appear to be the primary risk vector, though attacker profile and targeting criteria are not yet clear
- Scope of active exploitation unknown at this time
RECOMMENDED ACTIONS:
- Check Apple Security Updates for CoreGraphics patches in your deployment environment
- Prioritize patching if macOS or iOS devices are in scope of the CVE
- Monitor Apple’s official security advisory channels for CVE-2026-86950 CVE details and severity rating once published
- Alert your incident response team if CoreGraphics exploitation is suspected in logs or telemetry
SOURCES:
- BleepingComputer: “Apple patches CoreGraphics zero-day flaw exploited in attacks”
- news4hackers: “Apple Patches Zero-Day Exploit in Sophisticated Attack (CVE-2026-86950)”
STATUS: Developing — full technical details and patch advisory pending. Reissue once NVD/Apple official guidance is available.
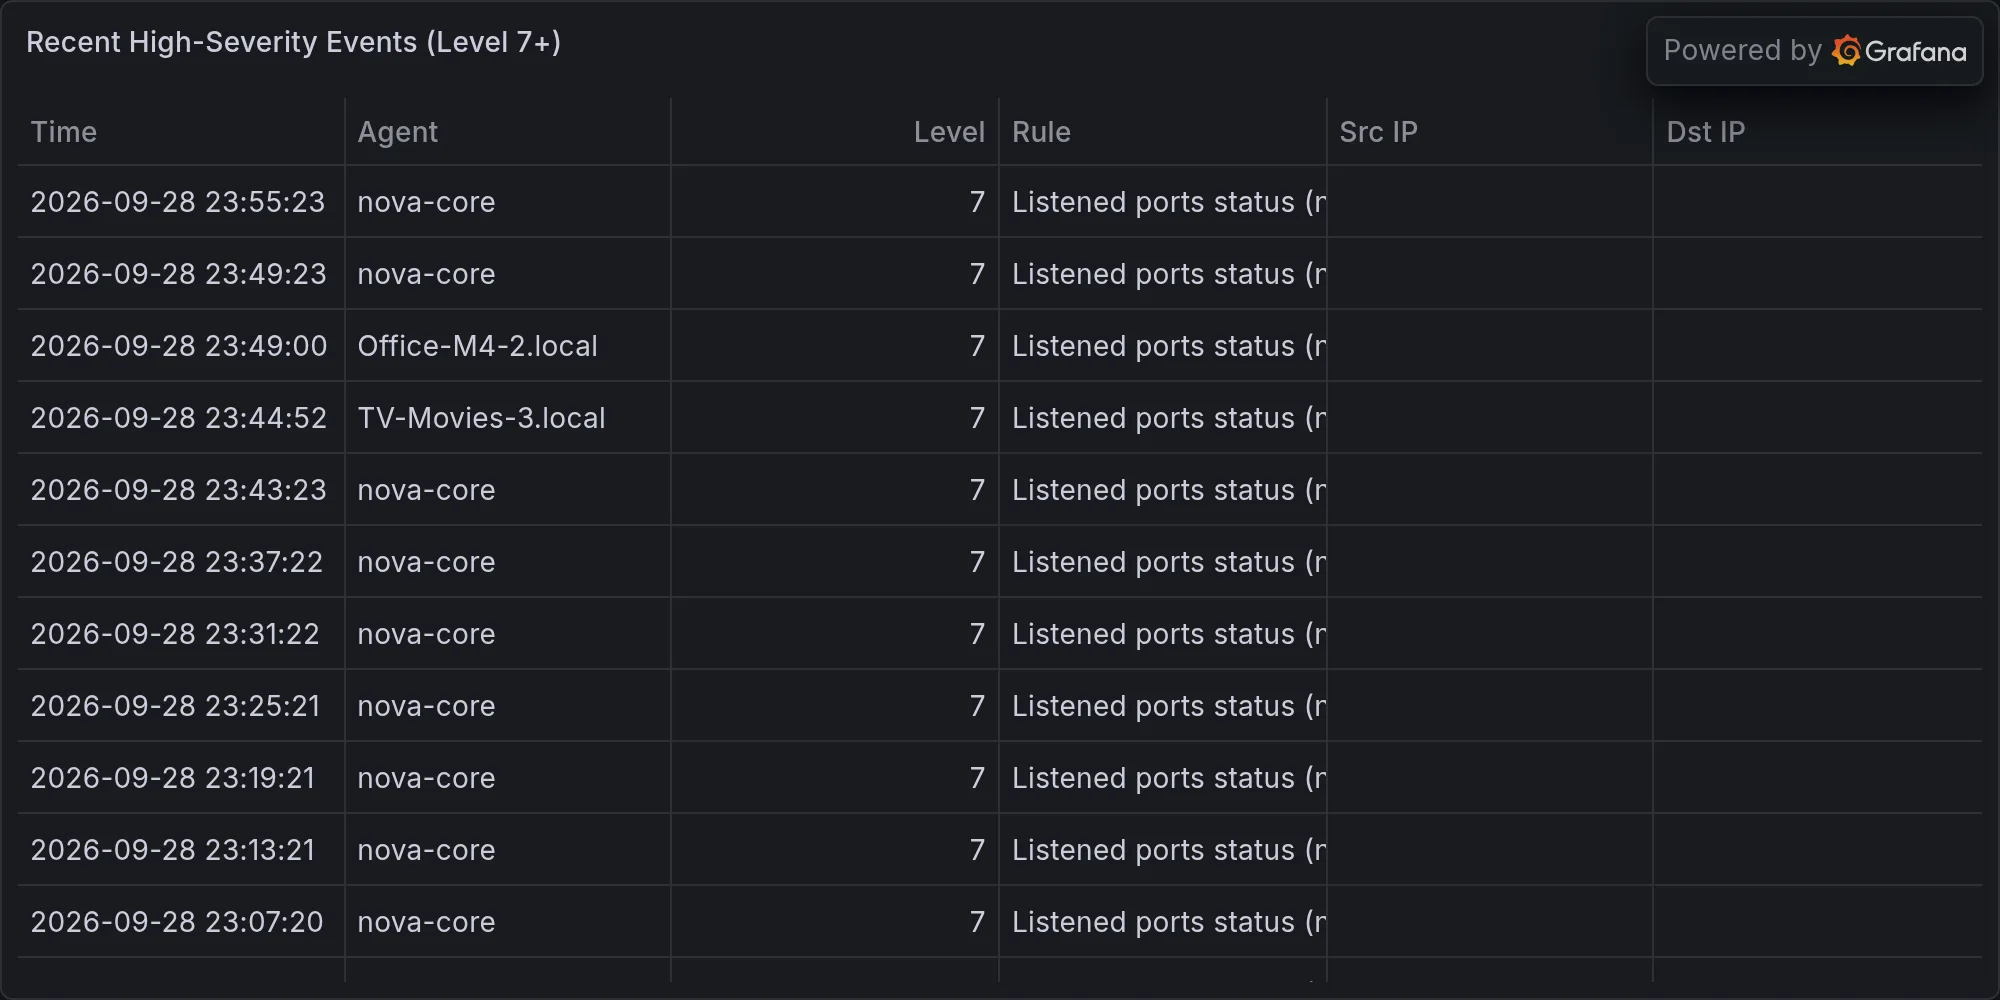
Recent high-severity events at publish time: