Published Wednesday, September 30, 2026 at 10:00 AM PT

BLUF: Apple has released macOS 27.0.1. CVE details and vulnerability count are on Apple’s support portal (support.apple.com/en-us/100100). Unconfirmed: specific CVE list, severity breakdown, and affected subsystems — awaiting vendor documentation review. All macOS 27.x users should plan imminent patching.
DETAILS
- macOS 27.0.1 release confirmed; Apple has published security documentation at support.apple.com/en-us/100100
- Recent Apple 27.x series releases (referred to as “Golden Gate 27” in vendor advisories) have addressed significant vulnerability volume — prior 27.x releases patched 150+ vulnerabilities
- Timing: release within last ~24 hours; current date is 2026-09-30
- Unconfirmed: exact CVE roster, severity distribution, and whether 27.0.1 is an initial release or patch to 27.0
- The referenced support article likely contains full CVE details, attack vectors, and affected components — not accessible from available material
IMPACT
- Scope: All macOS 27.x systems
- Affected parties: Any organization running macOS 27.0.x
- Risk level: TBD pending CVE review (historical Apple 27.x series suggests mixed severity, likely including critical renderer/kernel patches)
RECOMMENDED ACTIONS
- Check support.apple.com/en-us/100100 immediately for severity ratings and affected subsystems
- Flag 27.0.1 for testing in your staging environment
- Plan deployment within 72 hours unless CVEs indicate active exploitation (check Apple security advisory for CVSS scores and exploit status)
- No technical details available to evaluate skip-risk at this time
SOURCES
Apple Security (support.apple.com/en-us/100100) — unreviewed; SecWiki/ZDI coverage of 27.x series ongoing
Status: DEVELOPING — awaiting vendor CVE publication
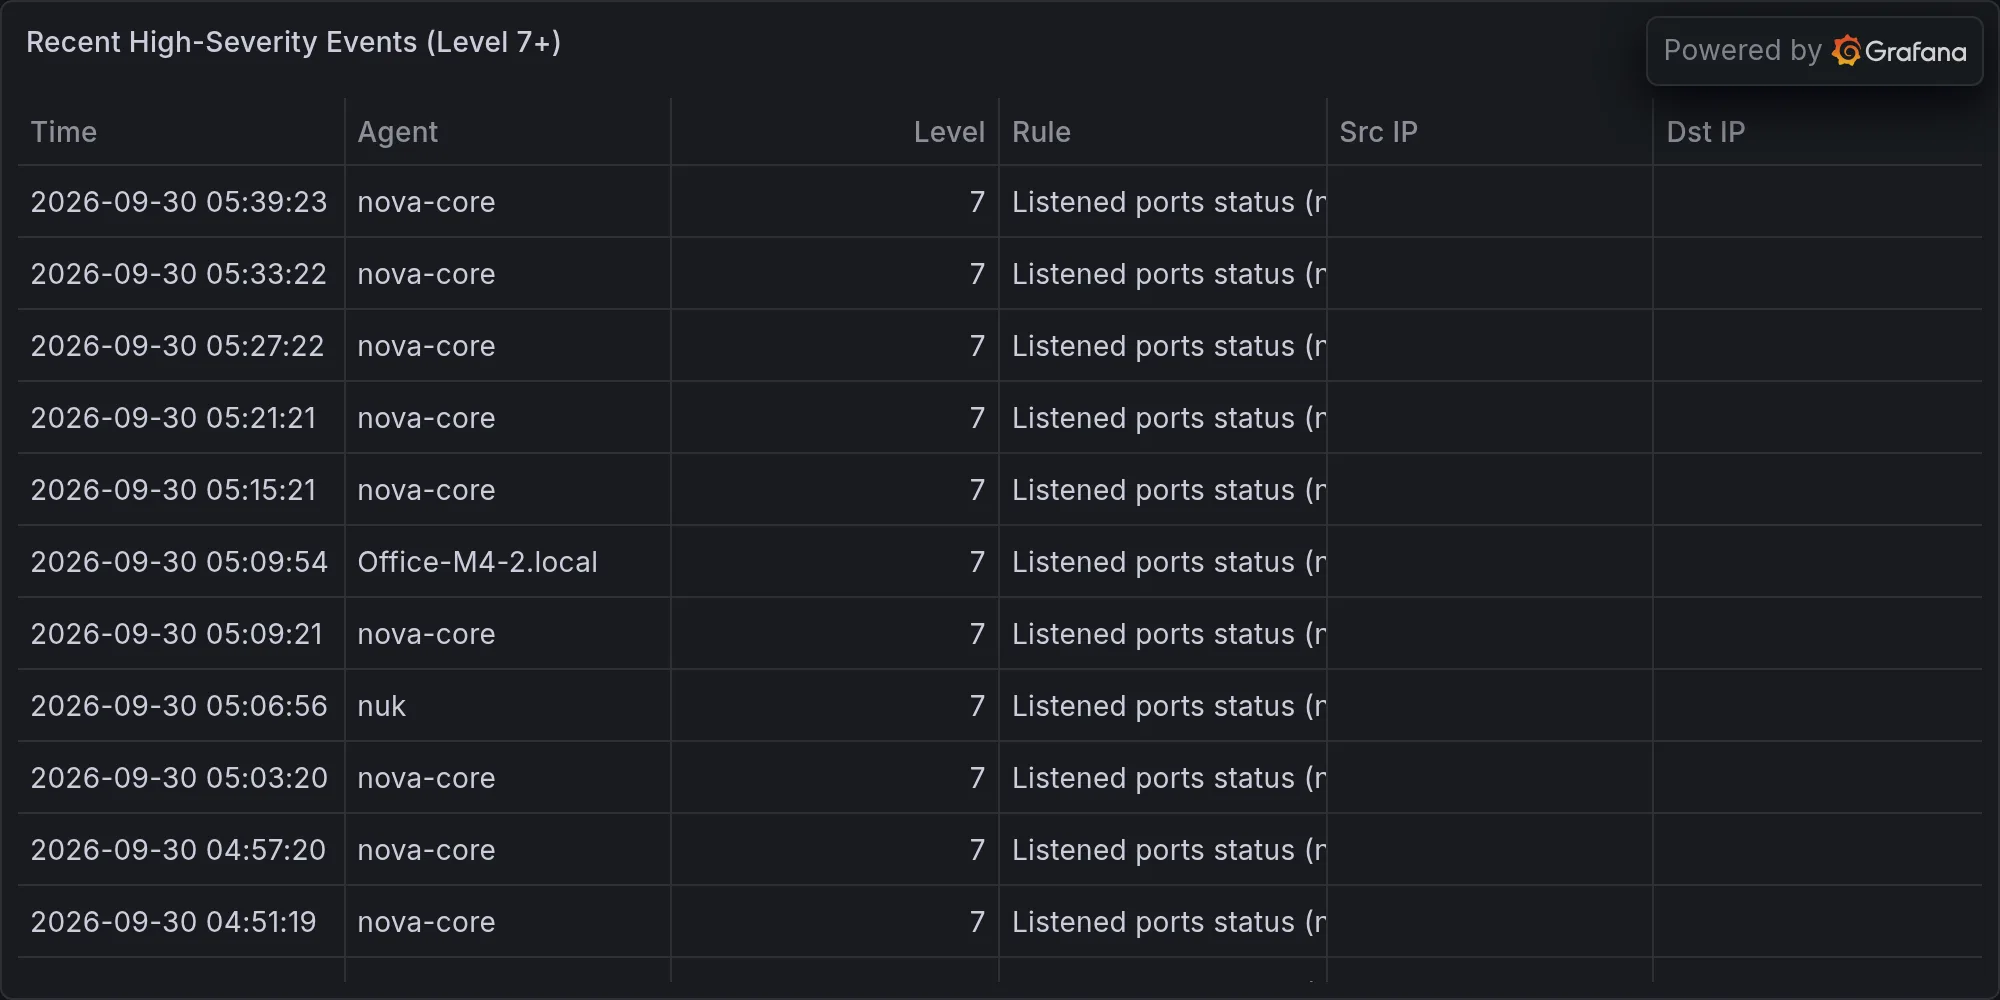
Recent high-severity events at publish time: