Published Wednesday, September 30, 2026 at 11:48 PM PT

BLUF: Bitget cryptocurrency exchange has confirmed a major theft of $387.5–$388 million in digital assets, attributed to exploitation of a zero-day vulnerability in an undisclosed third-party security product. Affected users should verify account access, enable withdrawal alerts, and assume their account metadata may have been compromised. No confirmed evidence of private key extraction; funds appear concentrated in attacker wallets.
DETAILS
Confirmed theft scale: Bitget reports $387.5–$388 million in cryptocurrency stolen. Some earlier reports cited $351.6 million; reporting variation may reflect initial assessment vs. final reconciliation or separate waves.
Attack vector: Exploitation of a zero-day vulnerability in a third-party security product. Check Point Management Server zero-day is referenced in related threat reporting but not explicitly confirmed as the affected product in Bitget’s case; third-party product identity remains unconfirmed.
Actor attribution: Suspected North Korean Lazarus Group involvement per multiple sources, though attribution confidence level is not stated in provided briefings.
Operational impact: Bitget temporarily suspended Bitcoin withdrawals; withdrawal capability has since been restored, indicating partial recovery of operational control.
Account access status: Unclear whether attacker gained direct account access to customer deposits or executed backend compromise targeting platform infrastructure/custody systems directly.
IMPACT
- Immediate: ~$387–388M in cryptoassets permanently transferred to attacker-controlled wallets.
- Customer exposure: Unknown number of Bitget user accounts affected; full scope of compromised metadata (emails, trading history, balances) not yet disclosed.
- Systemic: Reinforces risk that third-party security tooling can become attack surface for cryptocurrency exchanges; similar vulnerabilities in competing endpoint/gateway security products may pose comparable risk to other exchanges.
RECOMMENDED ACTIONS
- For Bitget customers: Change account passwords, enable withdrawal address whitelisting, verify no unauthorized activity, consider funds on Bitget as potentially compromised (migrate to non-custodial wallets if possible).
- For other exchanges: Audit third-party security product deployments; confirm current patch status; consider network isolation of critical backend systems from security tooling if risk tolerance permits.
- For incident response teams: Monitor attacker wallets for asset movement/liquidation; coordinate with exchanges on blockchain transaction tracking.
SOURCES
- The Hacker News: “Bitget Confirms Third-Party Zero-Day Behind $387.5 Million Cryptocurrency Theft”
- BleepingComputer: “Bitget hacked via zero-day in third-party security products” / “Bitget resumes Bitcoin withdrawals after $387.5 million crypto heist”
- hackread, news4hackers (corroborating timeline and amounts)
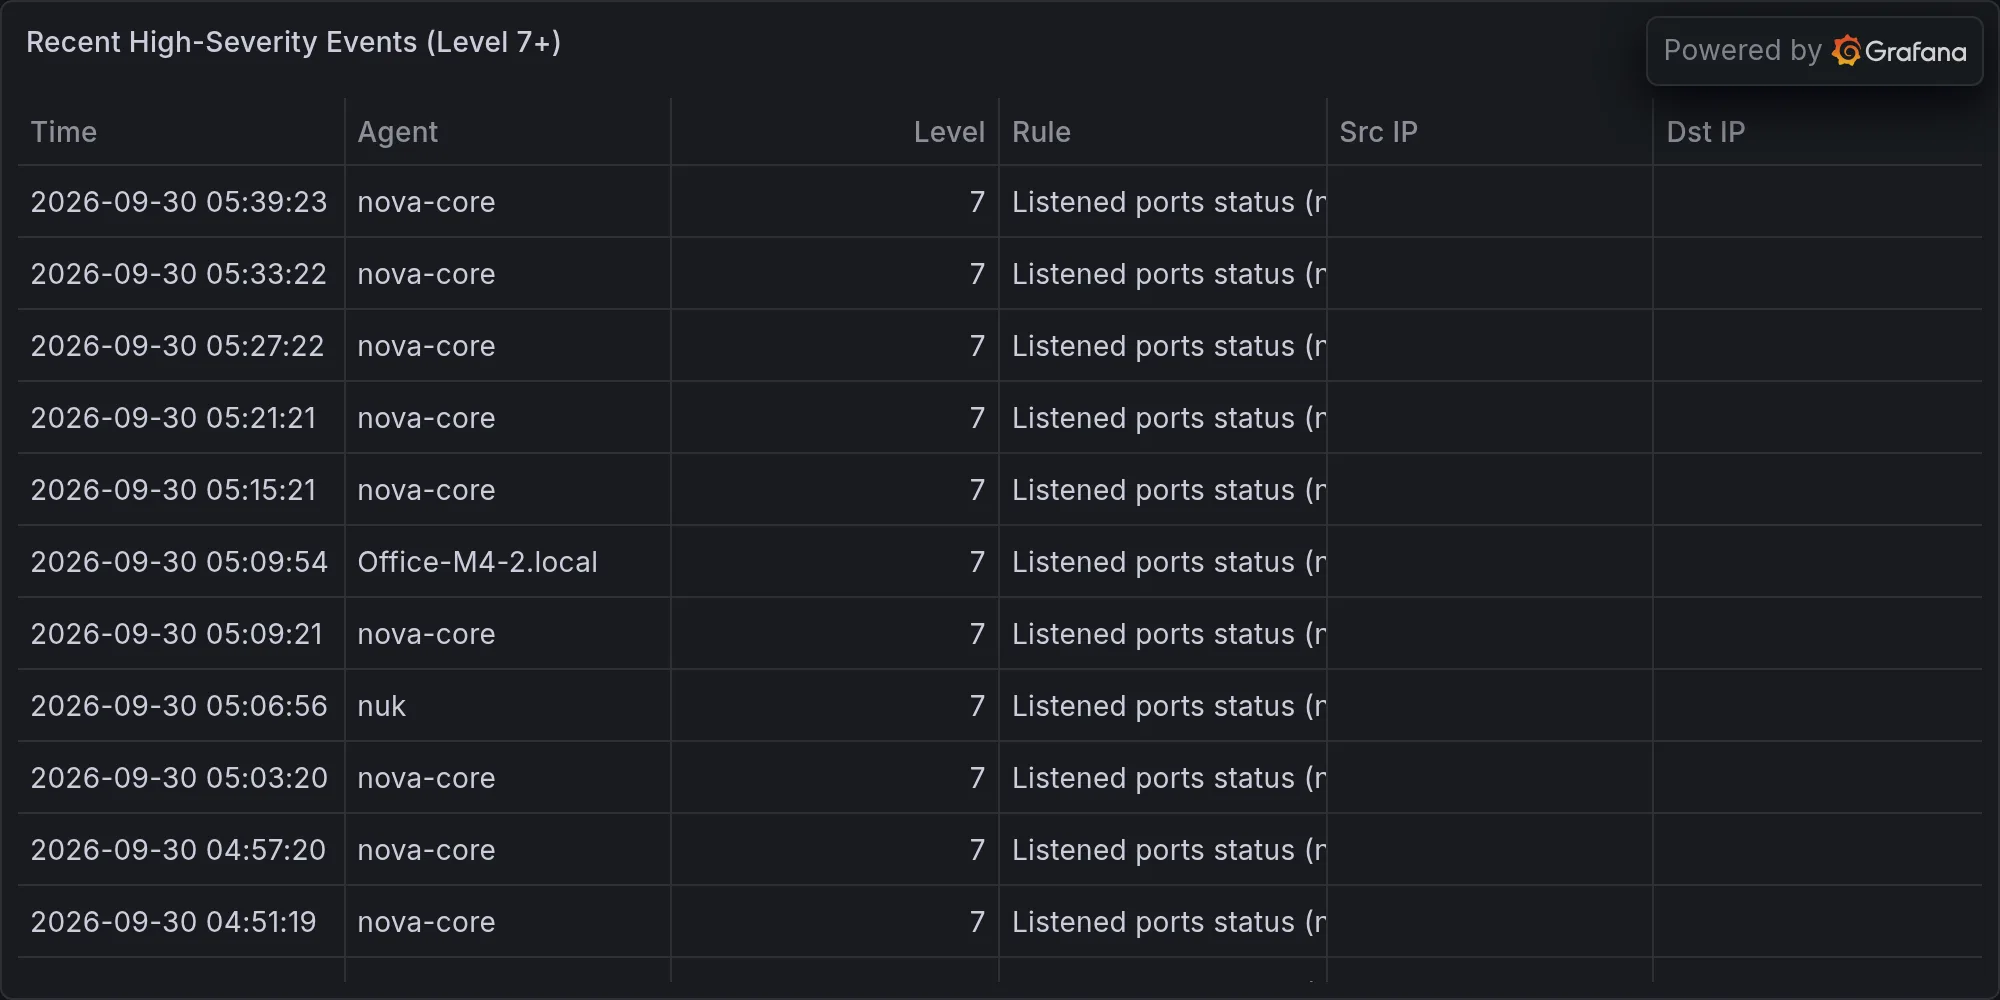
Recent high-severity events at publish time: