Published Wednesday, September 30, 2026 at 05:45 PM PT

BLUF: DIVD (Dutch Institute for Vulnerability Disclosure) has disclosed unpatched zero-days in Zammad helpdesk software that were actively exploited to conduct AI-driven network attacks. Organizations running Zammad should inventory instances immediately and monitor for unauthorized access. Details remain sparse; coordinated disclosure underway.
DETAILS
- DIVD identified zero-day vulnerabilities in Zammad (helpdesk/ticketing platform) actively exploited in network breaches.
- Attack vector involved automated AI agent(s) coordinating initial access and reconnaissance—same methodology used in parallel breach of DIVD’s own infrastructure.
- Exploitation enabled network-level compromise; AI automation suggests broad targeting potential.
- Patch/advisory status unknown; vendors/disclosure timeline not yet public in available material.
- Related threat activity: concurrent AI-augmented attack frameworks observed across financial and security sectors (credential theft, lateral movement).
IMPACT
- Directly affected: Organizations operating Zammad for helpdesk/ticketing—potentially hundreds to thousands globally.
- Indirect risk: Supply chain; DIVD’s own compromise may have exposed vulnerability details or victim data, widening exposure window.
- Threat model: Zero-day + AI agent = low detection friction; remediation complexity depends on dwell time pre-discovery.
RECOMMENDED ACTIONS
- Immediate: Audit firewall/proxy logs for Zammad instances; isolate from untrusted networks if zero-day severity warrants.
- Within 24h: Subscribe to DIVD’s disclosure timeline and Zammad’s official security channels; prepare patch procedure.
- Ongoing: Enable enhanced logging on Zammad authentication and API; search historical logs for anomalous bot/API activity (agent footprint).
- If exposed: Assume credential compromise; rotate API keys, service account passwords, and Zammad admin tokens.
SOURCES
- BleepingComputer: “DIVD says Zammad zero-days enabled AI-driven network breach” (headline; full advisory pending).
- BleepingComputer: “Automated AI agent used to breach cybersecurity nonprofit DIVD” (parallel attack pattern).
- Status: Unconfirmed—details sparse. Awaiting DIVD/Zammad official CVE and remediation guidance.
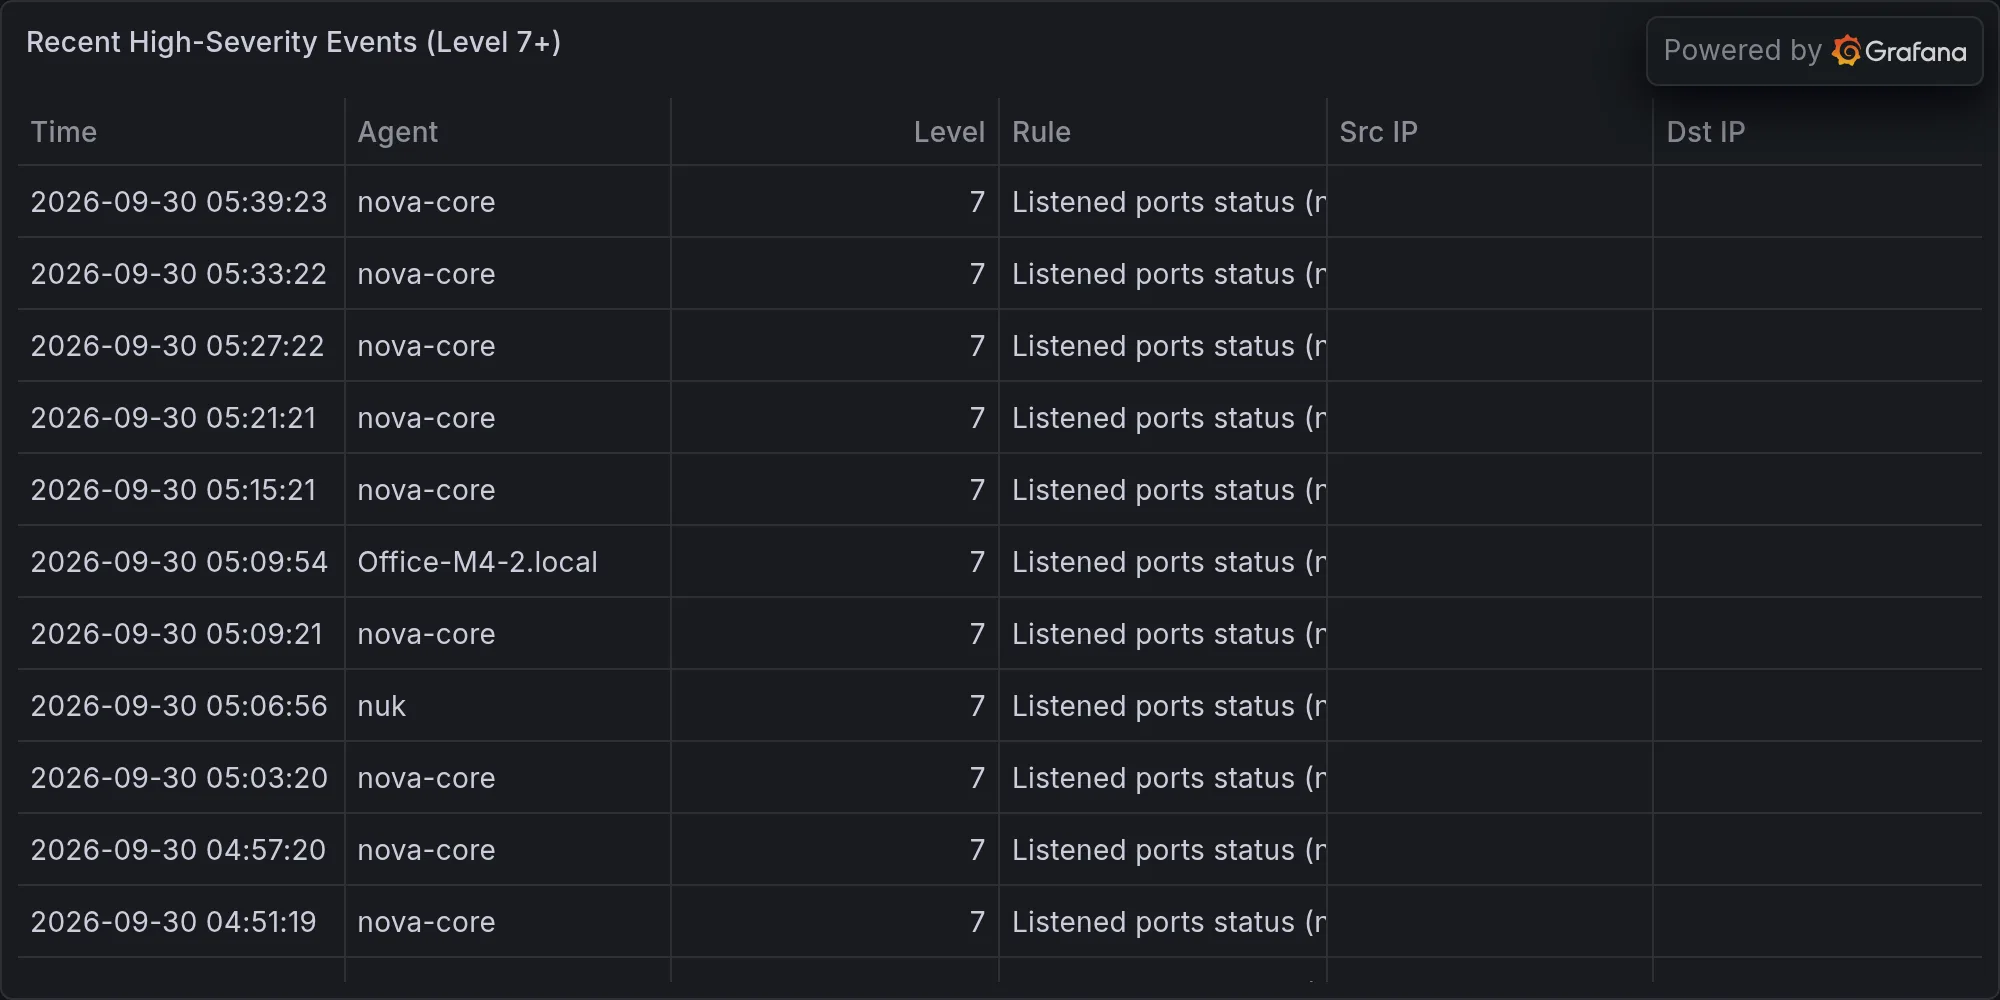
Recent high-severity events at publish time: