Published Wednesday, September 30, 2026 at 05:46 PM PT

BLUF: Windows systems running Node.js applications are at risk from a local privilege escalation vulnerability in npm CLI’s module resolution system. Discord desktop app confirmed affected (CVE-2026-0776). No patch available. Immediate action: audit Windows systems for Node.js installations; restrict local user access on sensitive machines; prepare to isolate and update Discord and other Node.js applications pending vendor fixes.
DETAILS
• Vulnerability submitted to Zero Day Initiative in September 2024; reveals fundamental design flaw in Node.js module resolution affecting Windows systems only.
• Attackers with local system access can exploit module resolution to execute arbitrary code with elevated privileges (local privilege escalation / LPE).
• Discord desktop application confirmed vulnerable (CVE-2026-0776 designated as 0-Day). Patch status unknown from available information; alert text indicates vulnerability remains unresolved.
• Attack surface includes any npm-based application on Windows; npm CLI itself is affected, making the vulnerability endemic to the Node.js ecosystem on this platform.
• No vendor patch timeline disclosed. Vulnerability has been known to ZDI since September 2024 (12+ months).
IMPACT
• Scope: Windows-only; all systems running Node.js applications (developers, CI/CD agents, desktop applications, servers).
• Severity: High — unprivileged local attacker (standard user) can escalate to admin/system privileges.
• Known affected: Discord desktop application. Likely broader exposure in Electron apps and Node.js-based tooling on Windows.
RECOMMENDED ACTIONS
Immediate: Identify all Windows systems running Node.js, npm, and Node-based desktop applications (Discord, VSCode, Slack, others).
Access control: Restrict local user account creation; isolate development and high-value Windows machines from untrusted local access.
Monitoring: Check Zero Day Initiative and Node.js Foundation security advisories for patch announcements daily.
Discord users: Subscribe to Discord security notices; prepare to update immediately upon patch release.
Vendors: Press Node.js Foundation and npm for fix timeline and interim mitigations.
SOURCES
Zero Day Initiative vulnerability database; Discord CVE-2026-0776; internal security tracking. Note: Source material truncated; full ZDI blog and affected version details unavailable from provided feed.
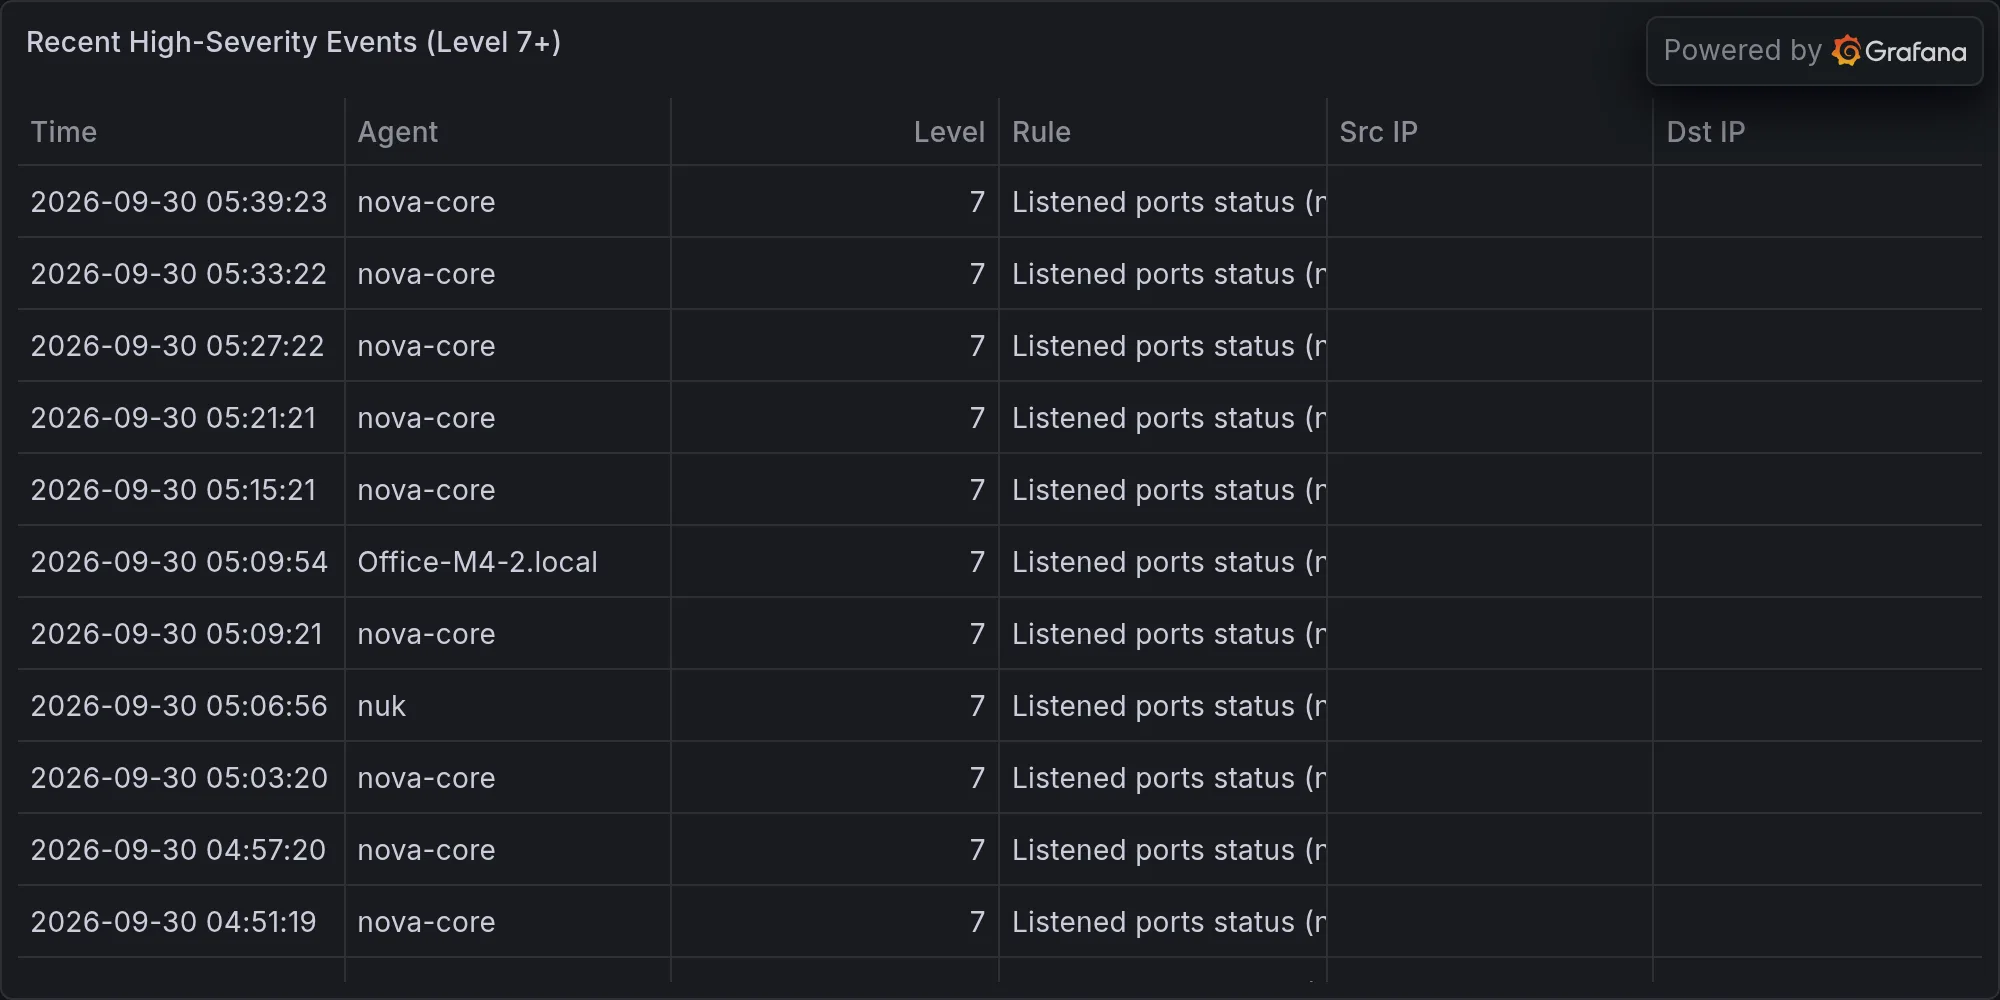
Recent high-severity events at publish time: