Published Thursday, October 01, 2026 at 11:52 AM PT

BLUF: Cisco has disclosed CVE-2026-76504, a critical authentication bypass in Catalyst SD-WAN Manager allowing unauthenticated remote attackers to gain full administrative access to affected systems. The vulnerability is actively exploited in the wild. Organizations running Catalyst SD-WAN Manager must immediately: (1) inventory affected deployments, (2) check for indicators of compromise, and (3) monitor for official patches and interim mitigations from Cisco.
DETAILS
- Vulnerability: CVE-2026-76504 — authentication bypass in Cisco Catalyst SD-WAN Manager
- Attack Vector: Remote, unauthenticated; no special prerequisites required
- Impact: Complete compromise — attackers gain administrative access to affected SD-WAN infrastructure
- Status: Zero-day; Cisco has confirmed active exploitation in the wild
- Disclosure Source: Cisco official disclosure relayed via SOC Prime threat intelligence
IMPACT
Catalyst SD-WAN Manager is a central management and control plane for Cisco’s SD-WAN fabric. Compromise of this system allows attackers to:
- Inject malicious configurations across all connected SD-WAN edge devices
- Intercept and redirect traffic on the SD-WAN overlay
- Pivot into downstream enterprise networks via compromised branch connectivity
- Establish persistent backdoors across distributed WAN infrastructure
Affected Scope: Any organization running Cisco Catalyst SD-WAN Manager in active management of SD-WAN deployments. Severity is highest for environments managing critical or sensitive traffic (finance, healthcare, government, telecommunications).
RECOMMENDED ACTIONS
- Immediate (Now): Isolate Catalyst SD-WAN Manager instances from untrusted networks pending patch availability; implement network segmentation restricting management console access to trusted administrative subnets only.
- Within 24 hours: Audit access logs and configuration change history for unauthorized administrative activity; cross-reference with exploit detection signatures from Cisco and your SOC.
- Ongoing: Monitor Cisco’s security advisory channels for patch release and interim guidance; apply patches immediately upon availability.
- Detection: Enable verbose logging on all SD-WAN Manager instances; alert on unauthenticated authentication bypass attempts and administrative account creation/privilege escalation events.
SOURCES
- Cisco official disclosure (via SOC Prime threat intelligence feed)
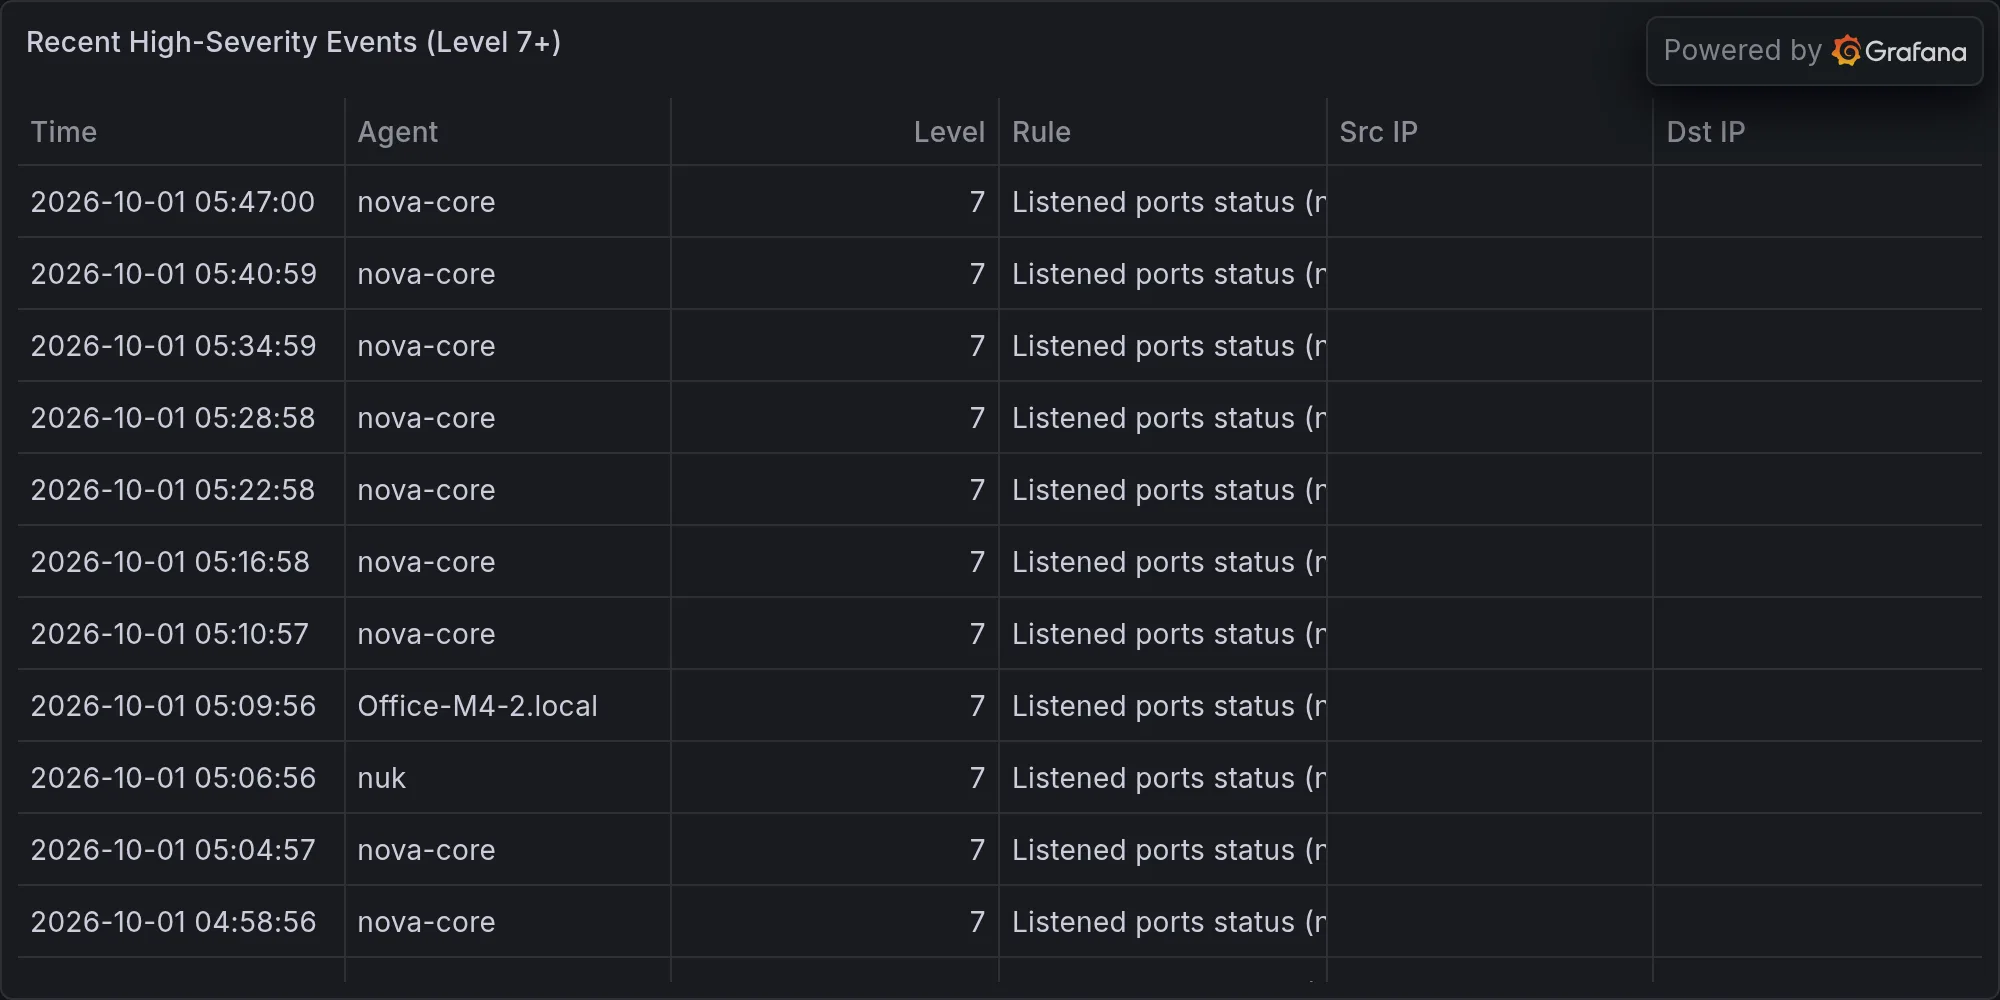
Recent high-severity events at publish time: