Published Friday, October 02, 2026 at 12:03 PM PT

BLUF: GitLab has issued a critical RCE vulnerability warning for its AI Gateway service (CVSS 9.9). Self-hosted GitLab instances are affected. Active exploitation reported by CISA. Patch immediately; affected organizations should assume compromise and review audit logs.
DETAILS
- Vulnerability: Remote code execution in GitLab AI Gateway service; allows unauthenticated command execution on self-hosted servers.
- Severity: CVSS 9.9 (critical).
- Scope: Self-hosted GitLab instances running AI Gateway; SaaS GitLab.com status not specified in available reports.
- Exploitation: CISA has confirmed active, post-disclosure exploitation in the wild.
- Disclosure: Public; vulnerability disclosed and attackers are actively targeting unpatched instances.
IMPACT
- Who is affected: Any organization operating self-hosted GitLab with AI Gateway enabled.
- What is at risk: Full remote code execution with GitLab process privileges; access to repositories, CI/CD pipelines, secrets, and underlying infrastructure.
- Likelihood: High — active exploitation underway; public details available.
RECOMMENDED ACTIONS
- Immediate: Identify all self-hosted GitLab instances in your environment and their current AI Gateway status.
- Patch: Update to the patched GitLab version immediately. If patched version unavailable, disable AI Gateway until patch is released.
- Investigate: Review GitLab audit logs and process execution logs from the vulnerability disclosure date forward for signs of exploitation (unexpected command execution, process spawning).
- Review secrets: Assume potential compromise of any secrets accessible to the GitLab process (API tokens, SSH keys, database credentials); rotate high-value secrets.
- Monitor: Watch for unusual API activity, pipeline executions, or repository access from the disclosure date onward.
SOURCES
- news4hackers: “GitLab Warns of Critical RCE Vulnerability in AI Gateway Service”
- CISA advisory: “Critical GitLab Vulnerability Exploited in Cyberattacks”
- The Hacker News: “GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers”
NOTE: Provided summaries do not include specific CVE ID, exact affected versions, or detailed technical vector. Consult official GitLab security advisory for patch version and complete mitigation guidance.
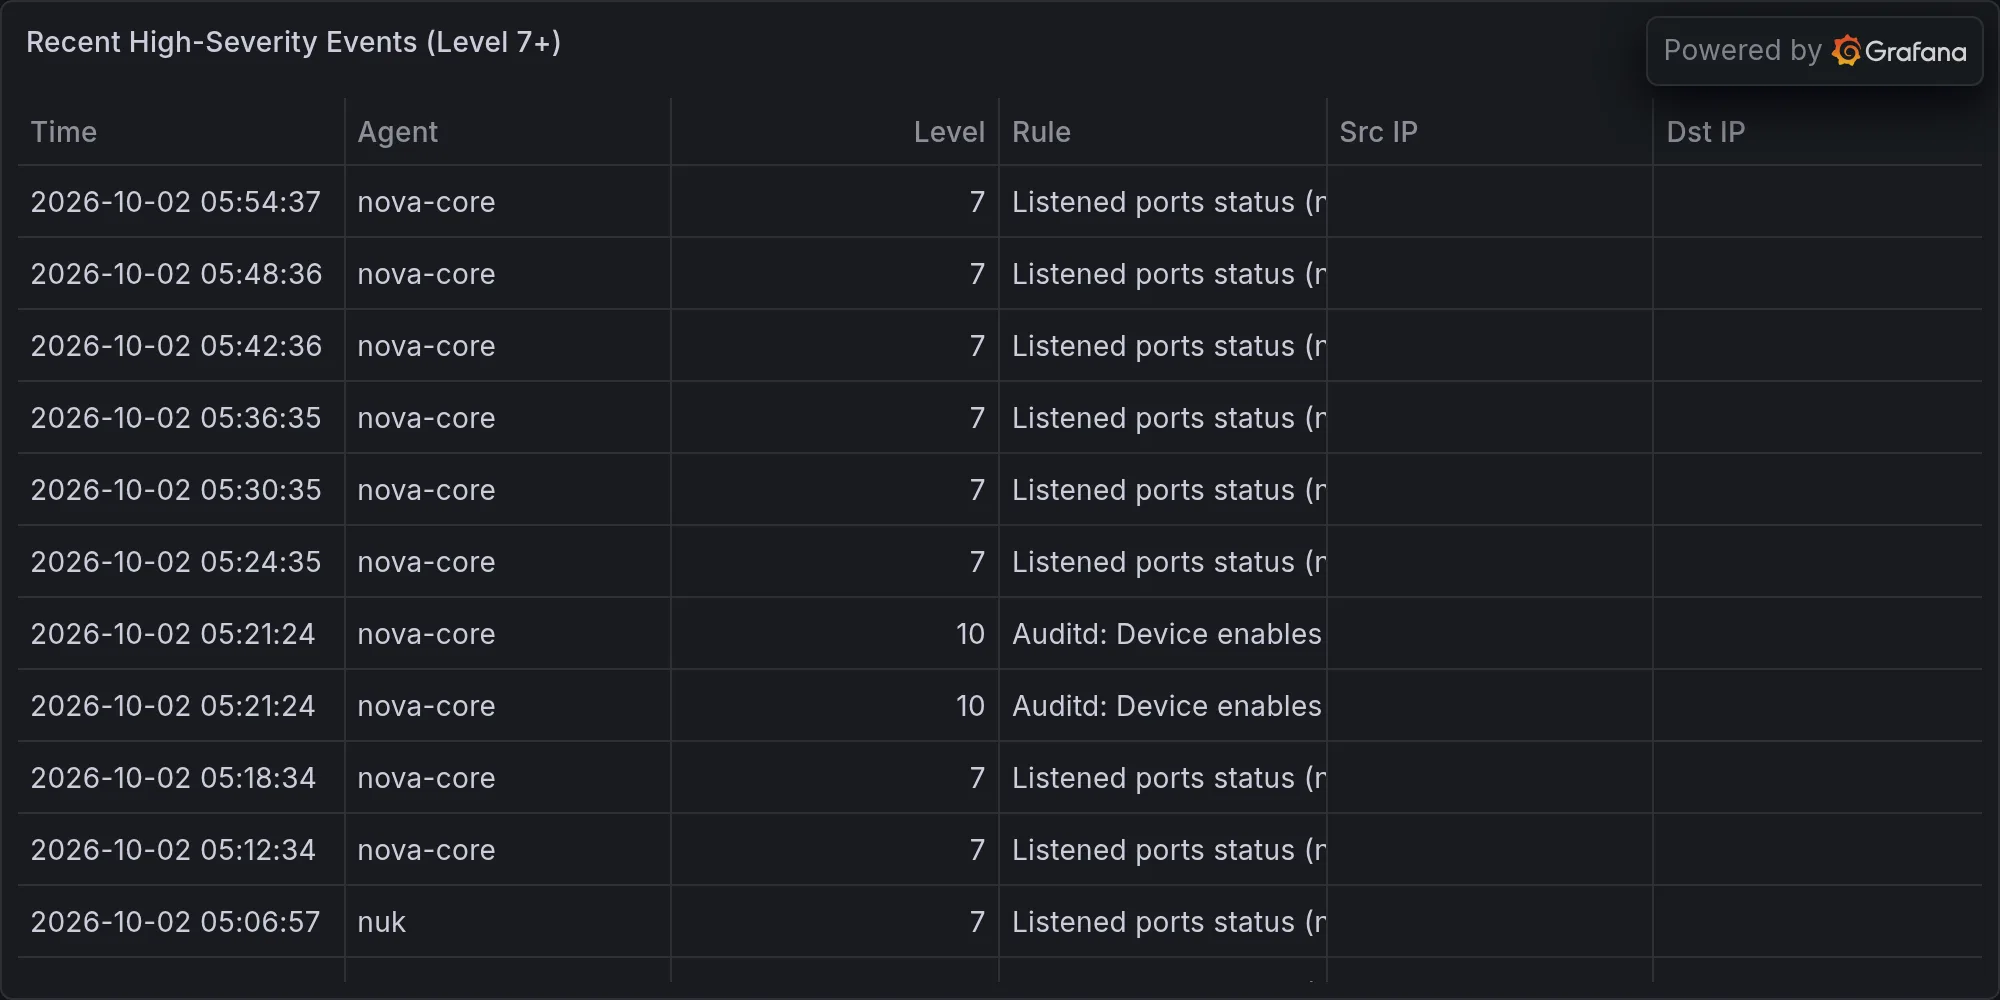
Recent high-severity events at publish time: