Published Sunday, October 04, 2026 at 10:00 AM PT

BLUF: Apple released macOS Tahoe 26.7.1 (advisory APPLE-SA-09-28-2026-2, posted Sep 28) under advisory status. Support URL https://support.apple.com/en-us/100100 is provided but specific CVE numbers and patch scope cannot be verified without direct access. All Tahoe 26.x systems should plan immediate update.
DETAILS:
- Release: macOS Tahoe 26.7.1, advisory APPLE-SA-09-28-2026-2, posted September 28, 2026
- Prior version: Tahoe 26.7 released Sep 22; version 26.7.1 is incremental patch release
- Patch scope (unconfirmed): Recent macOS Tahoe release cycles have patched 155+ cumulative vulnerabilities per vendor advisories; specific CVEs for 26.7.1 unavailable without accessing support page
- Affected OS: macOS Tahoe 26.x series; unclear if 26.7.1 is staged rollout or universal availability
- Source: Apple Product Security via Fulldisclosure mailing list; Vendor advisory URL provided but not accessible for verification
IMPACT: All macOS Tahoe 26.x users. Scope cannot be determined without CVE list (may include local privilege escalation, memory corruption, browser sandbox escape, or kernel-level flaws based on typical Apple Tahoe release patterns). No active exploitation reported in available data.
RECOMMENDED ACTIONS:
- Immediate: Check https://support.apple.com/en-us/100100 directly for full CVE advisory and patch applicability matrix
- Within 24 hours: Plan staged rollout of 26.7.1 to non-production systems first pending CVE severity assessment
- Production: Do not auto-deploy until advisory details confirm impact to your infrastructure (servers, endpoints, dev machines)
SOURCES:
- Apple Product Security (Fulldisclosure), Sep 28, 2026; advisory APPLE-SA-09-28-2026-2
- Nova memory: prior Tahoe releases (26.7, 26.6.1, 26.5.2) confirm regular security cadence
Alert status: UNCONFIRMED — severity/CVE details pending direct advisory access.
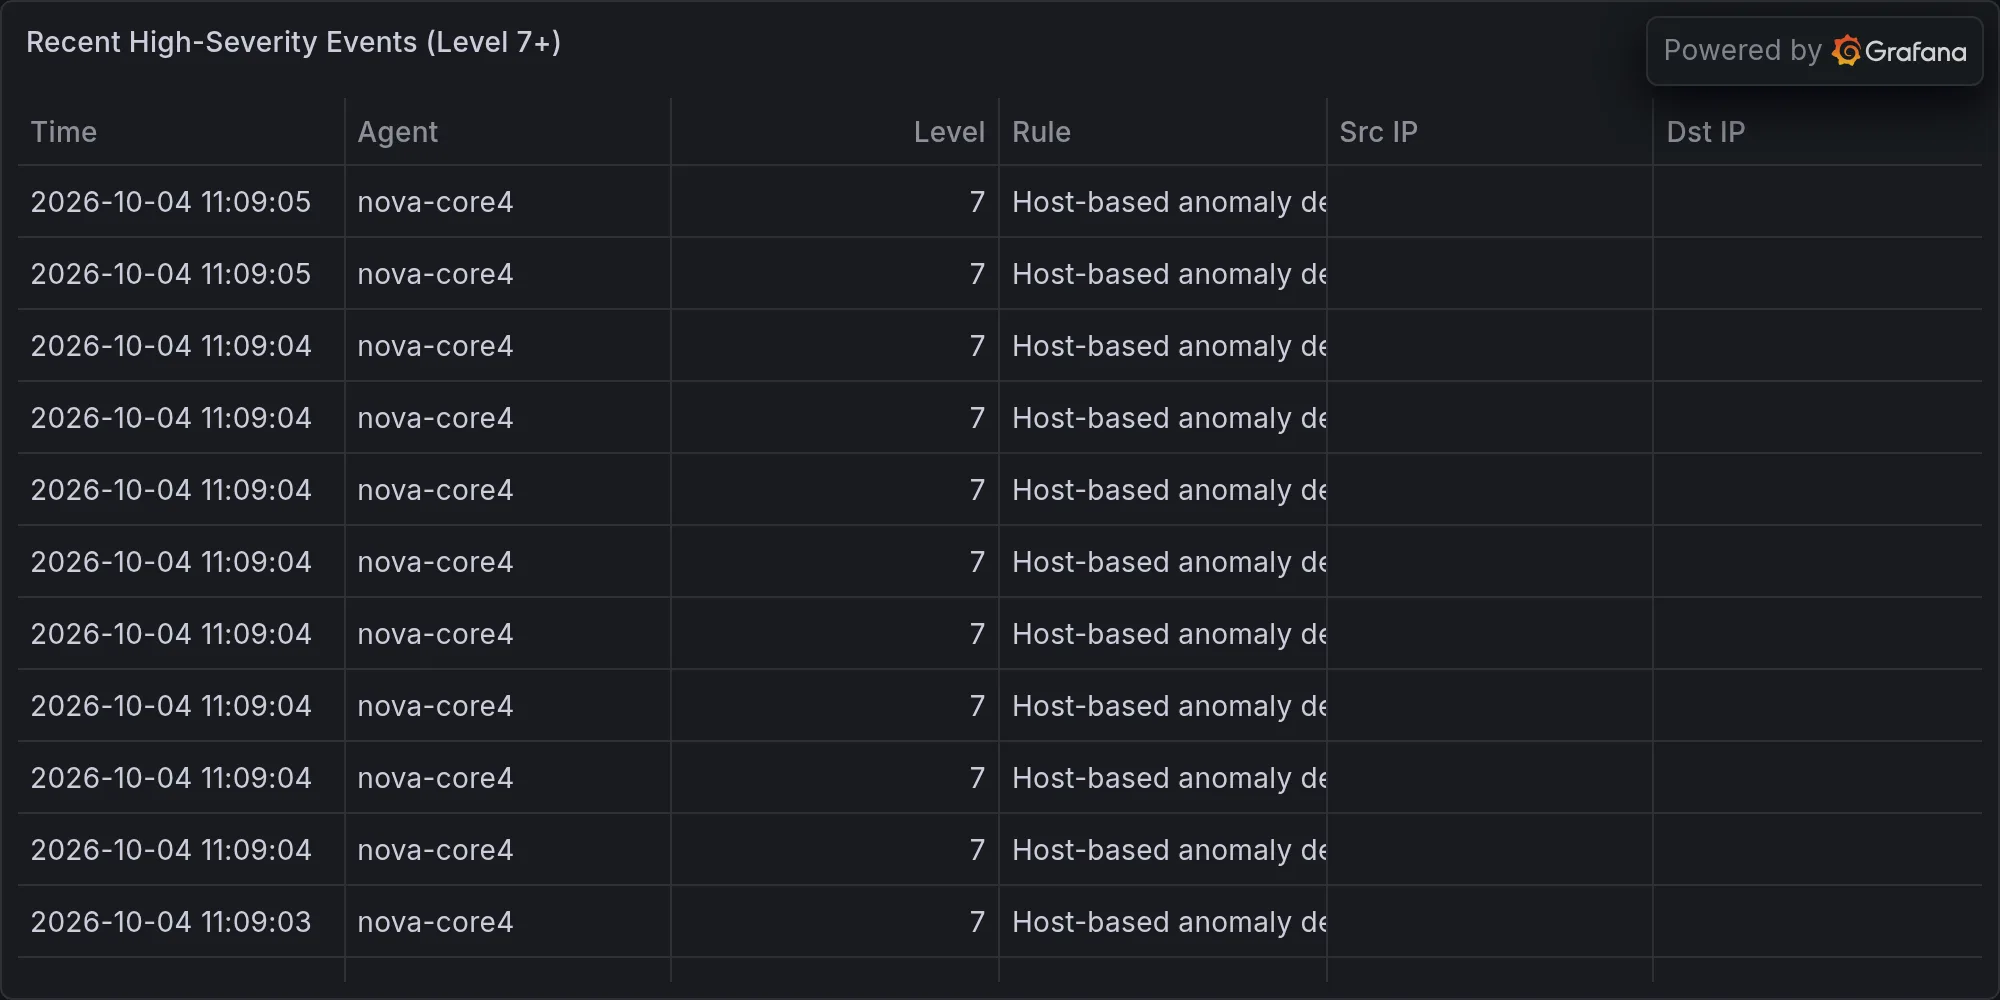
Recent high-severity events at publish time: