Published Sunday, October 04, 2026 at 05:47 PM PT

BLUF: Ubiquiti UDMPro gateway (192.168.1.1) blocked an inbound attack at 17:46:10 UTC on Oct 4. IPS signature triggered, source unknown. Ubiquiti has disclosed critical vulnerabilities recently; F5 BIG-IP zero-day (CVE-2026-94127) is in active exploitation across the internet. Attacker source and specific vulnerability targeted are not yet confirmed. Patch Ubiquiti immediately; inspect gateway logs for reconnaissance or pattern matching.
DETAILS
- Device hit: Ubiquiti UniFi Network gateway (UDMPro at 192.168.1.1, CEF source Rack14-UDMPro). IPS blocked the attempt; no confirmation of compromise.
- Attack vector: Inbound, direction from external. Source IP is unknown (blocked before full logging).
- Timing: Oct 04 17:46:10 — concurrent with active F5 BIG-IP RCE zero-day exploitation reported across the internet.
- Ubiquiti status: Per recent advisories in Nova memory, Ubiquiti has addressed three critical vulnerabilities. No specific CVE mapping yet to this gateway alert.
- F5 context: CVE-2026-94127 (BIG-IP APM zero-day RCE) is being exploited unauthenticated in the wild; Linux rootkit activity reported using F5 BIG-IP and Cisco FMC vulnerabilities.
IMPACT
- Scope: Single gateway device, LAN-facing. IPS prevented ingress — no confirmed successful breach.
- Affected systems: 192.168.1.1 (gateway only so far). All LAN clients route through this device; if compromised, attacker could see/intercept LAN traffic.
- Urgency: Medium-High. Attack was blocked, but unknown source and unconfirmed vulnerability type mean this may be targeted reconnaissance or a broad scanning campaign.
RECOMMENDED ACTIONS
- Immediate: Log into UDMPro, pull IPS alerts and gateway logs for Oct 04 16:00–18:00 UTC. Check for repeated source IPs, signature names, or multiple attempts.
- Patch: Verify Ubiquiti UniFi Network (controller and hardware) are on latest firmware. Ubiquiti security advisories released recently — apply patches today.
- Monitor: Watch gateway for similar IPS triggers over next 24–48 hours. If pattern emerges (repeated source, same signature), isolate gateway or enable additional logging.
- Search internal logs: Check if any internal services (F5 load balancers, Cisco FMC if present) have seen unusual traffic. F5 and Cisco vulns are in active use.
- Do NOT assume: This alert does not confirm which vulnerability was targeted — only that an attack matching an IPS rule was sent inbound and blocked.
SOURCES
- Ubiquiti IPS alert CEF log (Oct 04 17:46:10).
- Nova memory: recent advisories on F5 BIG-IP CVE-2026-94127 (RCE, unauthenticated, in active exploitation); Ubiquiti three critical vulns; Linux rootkit using F5/Cisco exploits.
- Specific CVE attribution to this attack: unconfirmed — requires log inspection.
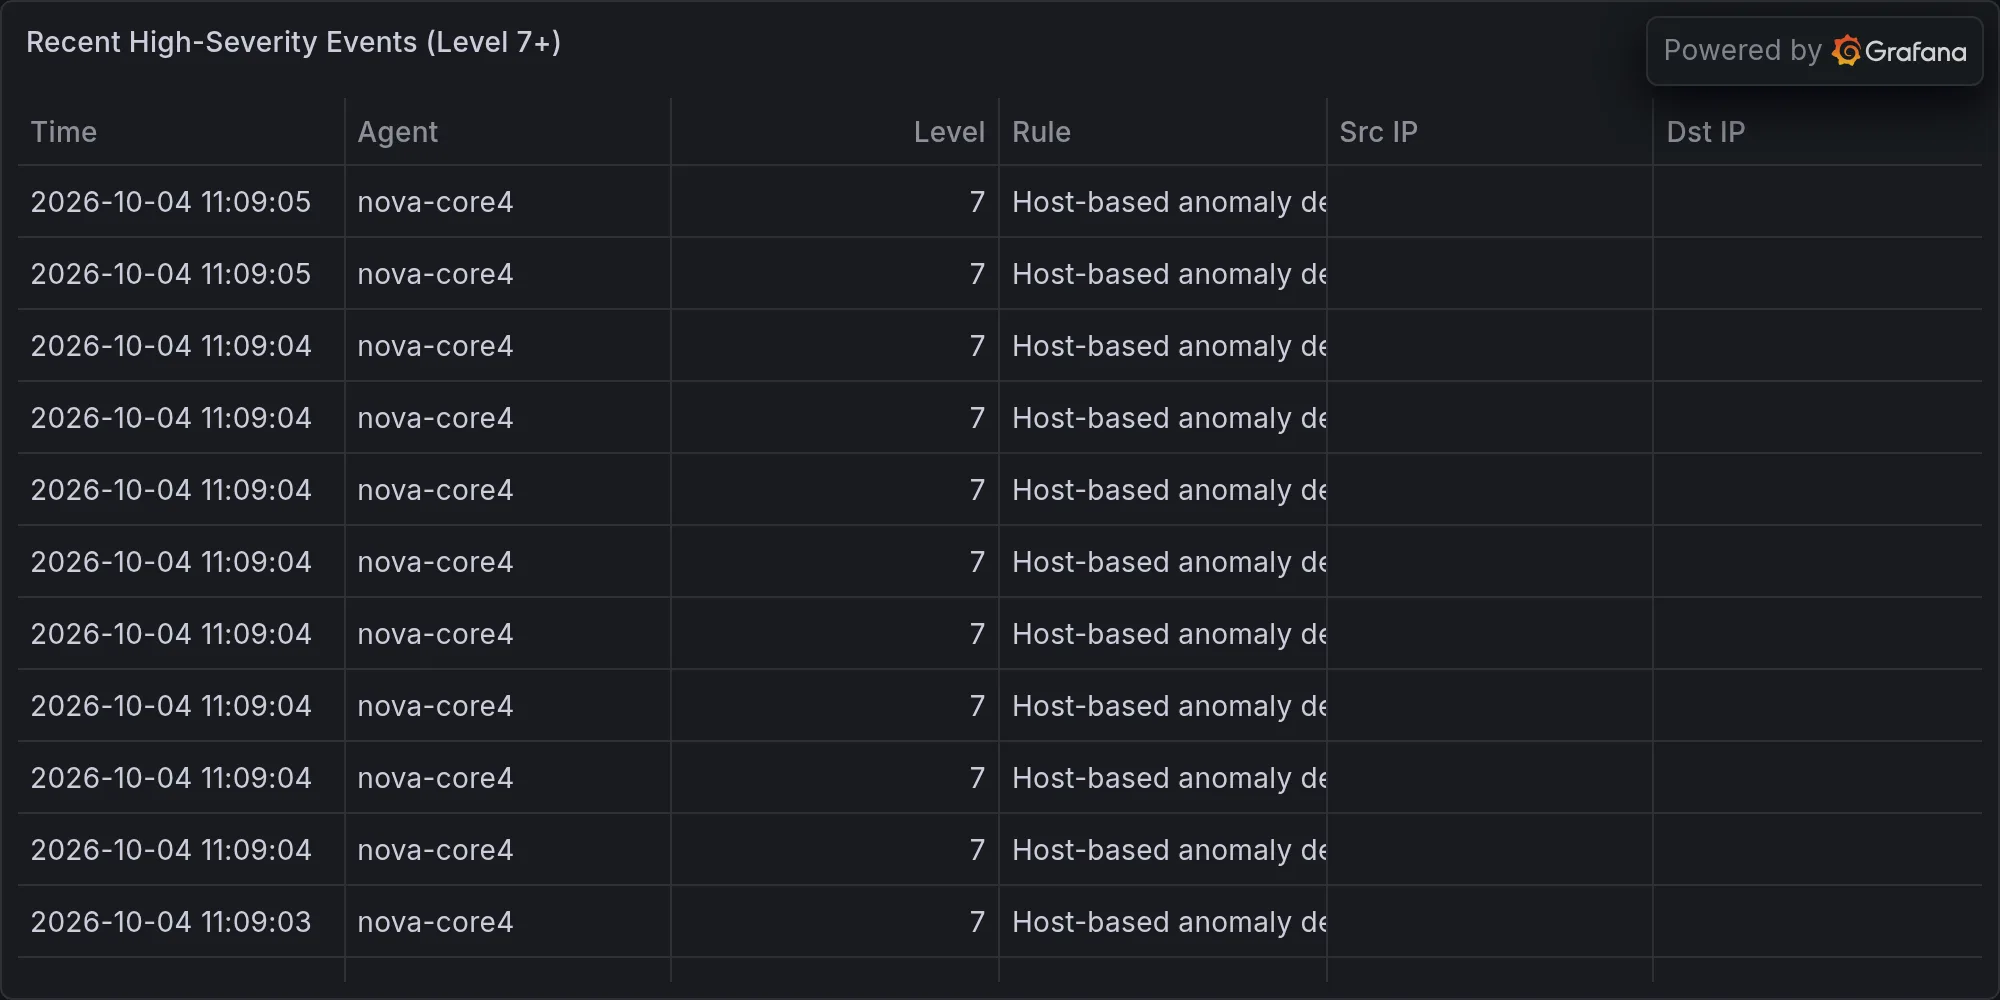
Recent high-severity events at publish time: